

ብዙ የመጫኛ ቁሳቁሶች አሉ። WordPress, የጉግል ፍለጋ ለቁልፍ ቃላት "WordPress install" ወደ ግማሽ ሚሊዮን የሚጠጉ ውጤቶችን ይመልሳል። ሆኖም፣ ከነሱ መካከል ለመጫን እና ለማዋቀር በጣም ጥቂት ጠቃሚ መመሪያዎች አሉ። WordPress እና መሰረታዊው ኦፕሬቲንግ ሲስተም ለረጅም ጊዜ ሊደገፉ ይችላሉ። ምናልባት ትክክለኛዎቹ ቅንብሮች በተወሰኑ ፍላጎቶች ላይ በእጅጉ የተመካ ሊሆን ይችላል፣ ወይም ምናልባት ይህ ሊሆን የቻለው ዝርዝር ማብራሪያው ጽሑፉን ለማንበብ አስቸጋሪ ስለሚያደርገው ነው።
በዚህ ጽሑፍ ውስጥ፣ ለራስ-ሰር ጭነት የ bash ስክሪፕት በማቅረብ ከሁለቱም አቀራረቦች ውስጥ ምርጡን ለማጣመር እንሞክራለን። WordPress ላይ Ubuntuእንዲሁም እያንዳንዱን ክፍል ምን እንደሚያደርግ እና በእድገቱ ላይ ያደረግናቸውን ስምምነቶች እናብራራለን። ልምድ ያለው ተጠቃሚ ከሆኑ፣ ጽሑፉን መዝለል እና በቀላሉ ማግኘት ይችላሉ። ለማሻሻያ እና በአካባቢዎ ውስጥ ጥቅም ላይ የሚውል። የስክሪፕት ውፅዓት ብጁ ጭነት ነው። WordPress በ NGINX ዩኒት ላይ የሚሰራ እና ለምርት አገልግሎት ተስማሚ የሆነ የ Let's Encrypt ድጋፍ ያለው።
ለማሰማራት የዳበረ ሥነ-ሕንፃ WordPress የNGINX ዩኒት አጠቃቀም በሚከተለው ውስጥ ተገልጿል አሁን እዚያ ያልተሸፈኑ ነገሮችን (እንደሌሎች ብዙ አጋዥ ስልጠናዎች) እናዋቅራቸዋለን።
- WordPress CLI
- የ TLSSSL ሰርተፍኬቶችን እናመስጥር
- የምስክር ወረቀቶችን በራስ ሰር እድሳት
- NGINX መሸጎጫ
- NGINX መጭመቂያ
- HTTPS እና HTTP/2 ድጋፍ
- የሂደት ራስ-ሰር
ጽሁፉ በአንድ አገልጋይ ላይ መጫኑን ይገልፃል፣ እሱም በተመሳሳይ ጊዜ የማይንቀሳቀስ ፕሮሰሲንግ አገልጋይ፣ ፒኤችፒ ፕሮሰሲንግ አገልጋይ እና የውሂብ ጎታ ያስተናግዳል። በርካታ ምናባዊ አስተናጋጆችን እና አገልግሎቶችን የሚደግፍ ጭነት ለወደፊቱ ትልቅ ርዕስ ነው። በእነዚህ ጽሑፎች ውስጥ ስለሌለው ነገር እንድንጽፍ ከፈለጉ በአስተያየቶቹ ውስጥ ይጻፉ.
መስፈርቶች
- መያዣ አገልጋይ ( ወይም )፣ ቢያንስ 512 ሜባ ራም ያለው እና የተጫነ ምናባዊ ማሽን ወይም መደበኛ የሃርድዌር አገልጋይ Ubuntu 18.04 ወይም ከዚያ በኋላ።
- በይነመረብ ተደራሽ ወደቦች 80 እና 443
- ከዚህ አገልጋይ ይፋዊ አይፒ አድራሻ ጋር የተጎዳኘ የጎራ ስም
- ስርወ መዳረሻ (ሱዶ)።
የሕንፃ አጠቃላይ እይታ
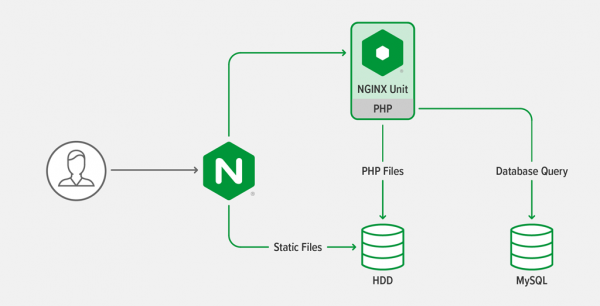
አርክቴክቸር ከተገለፀው ጋር ተመሳሳይ ነው። ፣ ባለ ሶስት ደረጃ የድር መተግበሪያ። በPHP ኢንጂን ላይ የሚሰሩ የPHP ስክሪፕቶችን እና በድር አገልጋይ የሚሰሩ የማይንቀሳቀሱ ፋይሎችን ያካትታል።
አጠቃላይ መመሪያዎች
- በስክሪፕት ውስጥ ያሉ ብዙ የማዋቀር ትእዛዞች ለ idempotency ከተጠቀለሉ፡ ስክሪፕቱ ቀደም ሲል የነበሩትን መቼቶች የመቀየር አደጋ ሳያስከትል ብዙ ጊዜ ሊሰራ ይችላል።
- ስክሪፕቱ ሶፍትዌሮችን ከማከማቻዎች ለመጫን ይሞክራል፣ ስለዚህ የስርዓት ዝመናዎችን በአንድ ትዕዛዝ መተግበር ይችላሉ (
apt upgradeለ Ubuntu). - ትዕዛዞቹ በኮንቴይነር ውስጥ እየሮጡ መሆናቸውን ለማወቅ ይሞክራሉ ስለዚህ ቅንብሮቻቸውን በዚሁ መሰረት መቀየር ይችላሉ።
- በቅንብሮች ውስጥ ለመጀመር የክር ሂደቶችን ቁጥር ለማዘጋጀት ስክሪፕቱ በመያዣዎች ፣ በቨርቹዋል ማሽኖች እና በሃርድዌር አገልጋዮች ውስጥ ለመስራት አውቶማቲክ መቼቶችን ለመገመት ይሞክራል።
- መቼቶችን ስንገልጽ በመጀመሪያ ስለ አውቶሜሽን እናስባለን, ይህም የራስዎን መሠረተ ልማት እንደ ኮድ ለመፍጠር መሰረት ይሆናል ብለን ተስፋ እናደርጋለን.
- ሁሉም ትዕዛዞች እንደ ተጠቃሚ ነው የሚሄዱት። ሥርዋናውን የስርዓት ቅንብሮችን ስለሚቀይሩ፣ ግን በቀጥታ WordPress ከመደበኛ ተጠቃሚ ይሰራል።
የአካባቢ ተለዋዋጮችን ማቀናበር
ስክሪፕቱን ከማሄድዎ በፊት የሚከተሉትን የአካባቢ ተለዋዋጮች ያዘጋጁ።
WORDPRESS_DB_PASSWORD- ወደ የውሂብ ጎታ የይለፍ ቃል WordPressWORDPRESS_ADMIN_USER- የአስተዳዳሪ ስም WordPressWORDPRESS_ADMIN_PASSWORD- የአስተዳዳሪ የይለፍ ቃል WordPressWORDPRESS_ADMIN_EMAIL- የአስተዳዳሪ ኢሜይል WordPressWORDPRESS_URL— ሙሉ የድር ጣቢያ ዩአርኤል WordPressጀምሮhttps://.LETS_ENCRYPT_STAGING- በነባሪ ባዶ ነገር ግን እሴቱን ወደ 1 በማዘጋጀት ሴቲንግዎን ሲሞክሩ በተደጋጋሚ የምስክር ወረቀቶችን ለመጠየቅ አስፈላጊ የሆኑትን Let's Encrypt staging serversን ትጠቀማለህ፣ ካልሆነ ግን ኢንክሪፕት እናድርግ በብዙ ጥያቄዎች የተነሳ የአይ ፒ አድራሻህን ለጊዜው ሊዘጋው ይችላል። .
ስክሪፕቱ እነዚህ ተዛማጅነት እንዳላቸው ያረጋግጣል WordPress ተለዋዋጮች ተዘጋጅተዋል፣ ካልሆነ ደግሞ መውጫዎች አሉ።
የስክሪፕት መስመሮች 572-576 እሴቱን ያረጋግጡ LETS_ENCRYPT_STAGING.
የተገኙ የአካባቢ ተለዋዋጮችን በማቀናበር ላይ
በመስመሮች 55-61 ላይ ያለው ስክሪፕት የሚከተሉትን የአካባቢ ተለዋዋጮች ያዘጋጃል፣ ለአንዳንድ ሃርድ-ኮድ እሴት ወይም ባለፈው ክፍል ከተቀመጡት ተለዋዋጮች የተገኘውን እሴት በመጠቀም።
DEBIAN_FRONTEND="noninteractive"- አፕሊኬሽኖች በስክሪፕት እየሰሩ መሆናቸውን እና የተጠቃሚ መስተጋብር ሊኖር እንደማይችል ይነግራል።WORDPRESS_CLI_VERSION="2.4.0"- የመተግበሪያው ስሪት WordPress CLI።WORDPRESS_CLI_MD5= "dedd5a662b80cda66e9e25d44c23b25c"- የሚተገበር ፋይል ቼክ ድምር WordPress CLI 2.4.0 (ስሪት በተለዋዋጭ ውስጥ ተገልጿልWORDPRESS_CLI_VERSION) በመስመር 162 ላይ ያለው ስክሪፕት ትክክለኛውን ፋይል መውረዱን ለማረጋገጥ ይህንን እሴት ይጠቀማል። WordPress CLI።UPLOAD_MAX_FILESIZE="16M"- ሊሰቀል የሚችል ከፍተኛው የፋይል መጠን WordPressይህ ቅንብር በበርካታ ቦታዎች ጥቅም ላይ ይውላል፣ ስለዚህ በአንድ ቦታ ማስቀመጥ ቀላል ነው።TLS_HOSTNAME= "$(echo ${WORDPRESS_URL} | cut -d'/' -f3)"— የስርዓት አስተናጋጅ ስም፣ ከWORDPRESS_URL ተለዋዋጭ የተወሰደ። ተገቢውን የTLS/SSL የምስክር ወረቀቶችን ከEncrypt እንዲሁም ለውስጣዊ ማረጋገጫ ለማግኘት ይጠቅማል። WordPress.NGINX_CONF_DIR="/etc/nginx"- ዋናውን ፋይል ጨምሮ ከ NGINX ቅንብሮች ጋር ወደ ማውጫው የሚወስደው መንገድnginx.conf.CERT_DIR="/etc/letsencrypt/live/${TLS_HOSTNAME}"— ለጣቢያው ወደ Let's Encrypt የምስክር ወረቀቶች የሚወስደው መንገድ WordPressከተለዋዋጭ የተገኘTLS_HOSTNAME.
የአስተናጋጅ ስም ምደባ WordPress አገልጋይ
ስክሪፕቱ የአገልጋዩን አስተናጋጅ ስም ከጣቢያው ጎራ ስም ጋር እንዲዛመድ ያዘጋጃል። ይህ አያስፈልግም፣ ነገር ግን በስክሪፕቱ እንደተዋቀረ አንድ አገልጋይ ሲያዋቅሩ የወጪ ደብዳቤ በSMTP በኩል ለመላክ የበለጠ ምቹ ነው።
የስክሪፕት ኮድ
# Change the hostname to be the same as the WordPress hostname
if [ ! "$(hostname)" == "${TLS_HOSTNAME}" ]; then
  echo " Changing hostname to ${TLS_HOSTNAME}"
  hostnamectl set-hostname "${TLS_HOSTNAME}"
fi
የአስተናጋጅ ስም ወደ /etc/hosts በማከል ላይ
ተጨማሪ ወቅታዊ ተግባራትን ለማስኬድ የሚያገለግል፣ ያንን ይጠይቃል WordPress በ HTTP በኩል ራሱን መድረስ ይችላል። WP-Cron በሁሉም አካባቢዎች ላይ በትክክል እንዲሰራ ለማረጋገጥ፣ ስክሪፕቱ በፋይሉ ላይ መስመር ያክላል። / ወዘተ / አስተናጋጆች፣ ስለዚህ WordPress በ loopback በይነገጽ በኩል እራሱን ማግኘት ይችላል፡
የስክሪፕት ኮድ
# Add the hostname to /etc/hosts
if [ "$(grep -m1 "${TLS_HOSTNAME}" /etc/hosts)" = "" ]; then
  echo " Adding hostname ${TLS_HOSTNAME} to /etc/hosts so that WordPress can ping itself"
  printf "::1 %sn127.0.0.1 %sn" "${TLS_HOSTNAME}" "${TLS_HOSTNAME}" >> /etc/hosts
fi
ለቀጣይ ደረጃዎች የሚያስፈልጉትን መሳሪያዎች መጫን
የተቀረው ስክሪፕት አንዳንድ ፕሮግራሞችን ይፈልጋል እና ማከማቻዎቹ የተዘመኑ ናቸው ብሎ ያስባል። የማጠራቀሚያዎችን ዝርዝር እናዘምነዋለን ፣ ከዚያ በኋላ አስፈላጊዎቹን መሳሪያዎች እንጭነዋለን-
የስክሪፕት ኮድ
# Make sure tools needed for install are present
echo " Installing prerequisite tools"
apt-get -qq update
apt-get -qq install -y
  bc
  ca-certificates
  coreutils
  curl
  gnupg2
  lsb-release
NGINX ክፍል እና NGINX ማከማቻዎችን በማከል ላይ
ስክሪፕቱ የቅርብ ጊዜዎቹ የደህንነት መጠገኛዎች እና የሳንካ ጥገናዎች ጥቅም ላይ መዋላቸውን ለማረጋገጥ ከኦፊሴላዊው የNGINX ማከማቻዎች NGINX Unit እና ክፍት ምንጭ NGINX ይጭናል።
ስክሪፕቱ የ NGINX ዩኒት ማከማቻ እና የ NGINX ማከማቻን ይጨምራል፣የማከማቻዎች ቁልፍ እና የማዋቀር ፋይሎችን ይጨምራል። apt, በበይነመረብ በኩል ወደ ማከማቻዎች መዳረሻን መወሰን.
ትክክለኛው የ NGINX ዩኒት እና NGINX መጫኛ በሚቀጥለው ክፍል ይከሰታል። ሜታዳታውን ብዙ ጊዜ እንዳናዘምን ለማድረግ ማከማቻዎቹን አስቀድመን እንጨምራለን፣ ይህም መጫኑን ፈጣን ያደርገዋል።
የስክሪፕት ኮድ
# Install the NGINX Unit repository
if [ ! -f /etc/apt/sources.list.d/unit.list ]; then
  echo " Installing NGINX Unit repository"
  curl -fsSL https://nginx.org/keys/nginx_signing.key | apt-key add -
  echo "deb https://packages.nginx.org/unit/ubuntu/ $(lsb_release -cs) unit" > /etc/apt/sources.list.d/unit.list
fi

# Install the NGINX repository
if [ ! -f /etc/apt/sources.list.d/nginx.list ]; then
  echo " Installing NGINX repository"
  curl -fsSL https://nginx.org/keys/nginx_signing.key | apt-key add -
  echo "deb https://nginx.org/packages/mainline/ubuntu $(lsb_release -cs) nginx" > /etc/apt/sources.list.d/nginx.list
fi
NGINX፣ NGINX Unit፣ PHP MariaDB፣ Certbot (እንመስጥር) እና ጥገኛዎቻቸውን በመጫን ላይ
ሁሉም የውሂብ ማከማቻዎች ከተጨመሩ በኋላ፣ ሜታዳታውን እናዘምናለን እና አፕሊኬሽኖቹን እንጭናለን። በስክሪፕቱ የተጫኑት ፓኬጆች በጅምር ላይ የሚመከሩ የ PHP ቅጥያዎችንም ያካትታሉ። WordPress.org
የስክሪፕት ኮድ
echo " Updating repository metadata"
apt-get -qq update

# Install PHP with dependencies and NGINX Unit
echo " Installing PHP, NGINX Unit, NGINX, Certbot, and MariaDB"
apt-get -qq install -y --no-install-recommends
  certbot
  python3-certbot-nginx
  php-cli
  php-common
  php-bcmath
  php-curl
  php-gd
  php-imagick
  php-mbstring
  php-mysql
  php-opcache
  php-xml
  php-zip
  ghostscript
  nginx
  unit
  unit-php
  mariadb-server
PHPን ከ NGINX ዩኒት ጋር ለመጠቀም ማዋቀር እና WordPress
ስክሪፕቱ በማውጫው ውስጥ የቅንብሮች ፋይል ይፈጥራል conf.d. ይህ ለPHP ሰቀላዎች ከፍተኛውን መጠን ያዘጋጃል፣ የPHP ስህተት ውፅዓትን ወደ STDERR ያበራል ስለዚህ ወደ NGINX Unit መዝገብ ይፃፉ እና የ NGINX ክፍልን እንደገና ያስጀምራል።
የስክሪፕት ኮድ
# Find the major and minor PHP version so that we can write to its conf.d directory
PHP_MAJOR_MINOR_VERSION="$(php -v | head -n1 | cut -d' ' -f2 | cut -d'.' -f1,2)"

if [ ! -f "/etc/php/${PHP_MAJOR_MINOR_VERSION}/embed/conf.d/30-wordpress-overrides.ini" ]; then
  echo " Configuring PHP for use with NGINX Unit and WordPress"
  # Add PHP configuration overrides
  cat > "/etc/php/${PHP_MAJOR_MINOR_VERSION}/embed/conf.d/30-wordpress-overrides.ini" << EOM
; Set a larger maximum upload size so that WordPress can handle
; bigger media files.
upload_max_filesize=${UPLOAD_MAX_FILESIZE}
post_max_size=${UPLOAD_MAX_FILESIZE}
; Write error log to STDERR so that error messages show up in the NGINX Unit log
error_log=/dev/stderr
EOM
fi

# Restart NGINX Unit because we have reconfigured PHP
echo " Restarting NGINX Unit"
service unit restart
የማሪያ ዲቤዝድ የውሂብ ጎታ ቅንብሮችን ለ ማዋቀር WordPress
ማሪያ ዲቢን ከ MySQL በላይ መርጠናል ፣ ምክንያቱም ብዙ የማህበረሰብ እንቅስቃሴ ስላለው እና በተጨማሪም ሊሆን ይችላል። (ምናልባት፣ እዚህ ሁሉም ነገር ቀላል ነው፡ MySQL ን ለመጫን ሌላ ማከማቻ ማከል ያስፈልግዎታል፣ በግምት። ተርጓሚ)።
ስክሪፕቱ አዲስ የውሂብ ጎታ ይፈጥራል እና የመዳረሻ ምስክርነቶችን ይፈጥራል። WordPress በ loopback በይነገጽ በኩል
የስክሪፕት ኮድ
# Set up the WordPress database
echo " Configuring MariaDB for WordPress"
mysqladmin create wordpress || echo "Ignoring above error because database may already exist"
mysql -e "GRANT ALL PRIVILEGES ON wordpress.* TO "wordpress"@"localhost" IDENTIFIED BY "$WORDPRESS_DB_PASSWORD"; FLUSH PRIVILEGES;"
ፕሮግራሙን መጫን WordPress CLI
በዚህ ደረጃ, ስክሪፕቱ ፕሮግራሙን ይጭናል በእሱ እርዳታ ቅንብሮችን ማዘጋጀት እና ማስተዳደር ይችላሉ WordPress ፋይሎችን በእጅ ማርትዕ፣ የውሂብ ጎታውን ማዘመን ወይም ወደ መቆጣጠሪያ ፓነሉ መግባት ሳያስፈልግ። እንዲሁም ገጽታዎችን እና ተጨማሪዎችን ለመጫን እና ዝመናዎችን ለማከናወን ሊያገለግል ይችላል። WordPress.
የስክሪፕት ኮድ
if [ ! -f /usr/local/bin/wp ]; then
  # Install the WordPress CLI
  echo " Installing the WordPress CLI tool"
  curl --retry 6 -Ls "https://github.com/wp-cli/wp-cli/releases/download/v${WORDPRESS_CLI_VERSION}/wp-cli-${WORDPRESS_CLI_VERSION}.phar" > /usr/local/bin/wp
  echo "$WORDPRESS_CLI_MD5 /usr/local/bin/wp" | md5sum -c -
  chmod +x /usr/local/bin/wp
fi
ጭነት እና ውቅር WordPress
ስክሪፕቱ የቅርብ ጊዜውን ስሪት ይጭናል WordPress ወደ ካታሎግ /var/www/wordpressእና እንዲሁም ቅንብሮቹን ይለውጣል:
- የመረጃ ቋቱ ግንኙነት የTCP ትራፊክን ለመቀነስ በ loopback ላይ ከTCP ይልቅ በዩኒክስ ጎራ ሶኬት ላይ ይሰራል።
- WordPress ቅድመ ቅጥያ ያክላል https:// ደንበኞች ከNGINX በ HTTPS ከተገናኙ እና የርቀት አስተናጋጅ ስም (በNGINX እንደቀረበው) ወደ PHP ከላከ ወደ URL። ይህንን ለማዘጋጀት አንድ ኮድ እንጠቀማለን.
- WordPress ለመግባት HTTPS ያስፈልጋል
- ነባሪው የዩአርኤል መዋቅር በንብረቶች ላይ የተመሰረተ ነው።
- ትክክለኛው የፋይል ስርዓት ፈቃዶች ለማህደሩ ተቀናብረዋል። WordPress.
የስክሪፕት ኮድ
if [ ! -d /var/www/wordpress ]; then
  # Create WordPress directories
  mkdir -p /var/www/wordpress
  chown -R www-data:www-data /var/www

  # Download WordPress using the WordPress CLI
  echo " Installing WordPress"
  su -s /bin/sh -c 'wp --path=/var/www/wordpress core download' www-data

  WP_CONFIG_CREATE_CMD="wp --path=/var/www/wordpress config create --extra-php --dbname=wordpress --dbuser=wordpress --dbhost="localhost:/var/run/mysqld/mysqld.sock" --dbpass="${WORDPRESS_DB_PASSWORD}""

  # This snippet is injected into the wp-config.php file when it is created;
  # it informs WordPress that we are behind a reverse proxy and as such
  # allows it to generate links using HTTPS
  cat > /tmp/wp_forwarded_for.php << 'EOM'
/* Turn HTTPS 'on' if HTTP_X_FORWARDED_PROTO matches 'https' */
if (isset($_SERVER['HTTP_X_FORWARDED_PROTO']) && strpos($_SERVER['HTTP_X_FORWARDED_PROTO'], 'https') !== false) {
    $_SERVER['HTTPS'] = 'on';
}
if (isset($_SERVER['HTTP_X_FORWARDED_HOST'])) {
    $_SERVER['HTTP_HOST'] = $_SERVER['HTTP_X_FORWARDED_HOST'];
}
EOM

  # Create WordPress configuration
  su -s /bin/sh -p -c "cat /tmp/wp_forwarded_for.php | ${WP_CONFIG_CREATE_CMD}" www-data
  rm /tmp/wp_forwarded_for.php
  su -s /bin/sh -p -c "wp --path=/var/www/wordpress config set 'FORCE_SSL_ADMIN' 'true'" www-data

  # Install WordPress
  WP_SITE_INSTALL_CMD="wp --path=/var/www/wordpress core install --url="${WORDPRESS_URL}" --data-gt-translate-attributes='["title"]' title="${WORDPRESS_SITE_TITLE}" --admin_user="${WORDPRESS_ADMIN_USER}" --admin_password="${WORDPRESS_ADMIN_PASSWORD}" --admin_email="${WORDPRESS_ADMIN_EMAIL}" --skip-email"
  su -s /bin/sh -p -c "${WP_SITE_INSTALL_CMD}" www-data

  # Set permalink structure to a sensible default that isn't in the UI
  su -s /bin/sh -p -c "wp --path=/var/www/wordpress option update permalink_structure '/%year%/%monthnum%/%postname%/'" www-data

  # Remove sample file because it is cruft and could be a security problem
  rm /var/www/wordpress/wp-config-sample.php

  # Ensure that WordPress permissions are correct
  find /var/www/wordpress -type d -exec chmod g+s {} ;
  chmod g+w /var/www/wordpress/wp-content
  chmod -R g+w /var/www/wordpress/wp-content/themes
  chmod -R g+w /var/www/wordpress/wp-content/plugins
fi
NGINX ክፍልን በማዘጋጀት ላይ
ስክሪፕቱ የNGINX ዩኒት PHPን እንዲያሄድ እና ዱካዎችን እንዲቆጣጠር ያዋቅራል። WordPressየ PHP ሂደት የስም ቦታን መለየት እና የአፈጻጸም ቅንብሮችን ማመቻቸት። ልብ ሊባሉ የሚገቡ ሶስት ባህሪያት አሉ፡
- ስክሪፕቱ በእቃ መያዢያ ውስጥ እየሰራ መሆኑን በማጣራት ላይ በመመስረት የስም ቦታዎች ድጋፍ በሁኔታዎች ይወሰናል. ይህ አስፈላጊ ነው ምክንያቱም አብዛኛው የእቃ መያዢያ ቅንጅቶች የጎጆ መያዣዎችን ማስጀመር አይደግፉም።
- ለስም ቦታዎች ድጋፍ ካለ የስም ቦታውን ያሰናክሉ። አውታረ መረብይህ ለመፍቀድ አስፈላጊ ነው WordPress በተመሳሳይ ጊዜ ከመጨረሻ ነጥቦች ጋር ይገናኙ እና በይነመረብ ላይ ተደራሽ ይሁኑ።
- ከፍተኛው የሂደቶች ብዛት እንደሚከተለው ይገለጻል. (MariaDB እና NGINX Uniy ን ለማስኬድ የሚያስችል ማህደረ ትውስታ)/(የራም ገደብ በ PHP + 5)
ይህ ዋጋ በNGINX ዩኒት ቅንጅቶች ውስጥ ተቀናብሯል።
ይህ እሴት ሁልጊዜ ቢያንስ ሁለት የ PHP ሂደቶችን እያሄዱ መሆናቸውን ያመለክታል፣ ይህም አስፈላጊ ነው ምክንያቱም WordPress ብዙ ያልተመሳሰሉ ጥያቄዎችን ለራሱ ያደርጋል፣ እና ያለ ተጨማሪ ሂደቶች፣ ለምሳሌ WP-Cron ማስኬድ አይሳካም። እዚህ የተፈጠሩት ቅንብሮች ወግ አጥባቂ ስለሆኑ እነዚህን ገደቦች በአካባቢያዊ ቅንብሮችዎ ላይ በመመስረት መጨመር ወይም መቀነስ ይፈልጉ ይሆናል። በአብዛኛዎቹ የምርት ስርዓቶች ላይ፣ ቅንብሮቹ ከ10 እስከ 100 መካከል ናቸው።
የስክሪፕት ኮድ
if [ "${container:-unknown}" != "lxc" ] && [ "$(grep -m1 -a container=lxc /proc/1/environ | tr -d ' ')" == "" ]; then
  NAMESPACES='"namespaces": {
        "cgroup": true,
        "credential": true,
        "mount": true,
        "network": false,
        "pid": true,
        "uname": true
    }'
else
  NAMESPACES='"namespaces": {}'
fi

PHP_MEM_LIMIT="$(grep 'memory_limit' /etc/php/7.4/embed/php.ini | tr -d ' ' | cut -f2 -d= | numfmt --from=iec)"
AVAIL_MEM="$(grep MemAvailable /proc/meminfo | tr -d ' kB' | cut -f2 -d: | numfmt --from-unit=K)"
MAX_PHP_PROCESSES="$(echo "${AVAIL_MEM}/${PHP_MEM_LIMIT}+5" | bc)"
echo " Calculated the maximum number of PHP processes as ${MAX_PHP_PROCESSES}. You may want to tune this value due to variations in your configuration. It is not unusual to see values between 10-100 in production configurations."

echo " Configuring NGINX Unit to use PHP and WordPress"
cat > /tmp/wordpress.json << EOM
{
  "settings": {
    "http": {
      "header_read_timeout": 30,
      "body_read_timeout": 30,
      "send_timeout": 30,
      "idle_timeout": 180,
      "max_body_size": $(numfmt --from=iec ${UPLOAD_MAX_FILESIZE})
    }
  },
  "listeners": {
    "127.0.0.1:8080": {
      "pass": "routes/wordpress"
    }
  },
  "routes": {
    "wordpress": [
      {
        "match": {
          "uri": [
            "*.php",
            "*.php/*",
            "/wp-admin/"
          ]
        },
        "action": {
          "pass": "applications/wordpress/direct"
        }
      },
      {
        "action": {
          "share": "/var/www/wordpress",
          "fallback": {
            "pass": "applications/wordpress/index"
          }
        }
      }
    ]
  },
  "applications": {
    "wordpress": {
      "type": "php",
      "user": "www-data",
      "group": "www-data",
      "processes": {
        "max": ${MAX_PHP_PROCESSES},
        "spare": 1
      },
      "isolation": {
        ${NAMESPACES}
      },
      "targets": {
        "direct": {
          "root": "/var/www/wordpress/"
        },
        "index": {
          "root": "/var/www/wordpress/",
          "script": "index.php"
        }
      }
    }
  }
}
EOM

curl -X PUT --data-binary @/tmp/wordpress.json --unix-socket /run/control.unit.sock http://localhost/config
NGINX በማዋቀር ላይ
መሰረታዊ የ NGINX ቅንብሮችን በማዋቀር ላይ
ስክሪፕቱ ለ NGINX መሸጎጫ ማውጫ ይፈጥራል ከዚያም ዋናውን የውቅር ፋይል ይፈጥራል nginx.conf. ለተቆጣጣሪ ሂደቶች ብዛት እና ለመስቀል ከፍተኛው የፋይል መጠን ቅንብር ትኩረት ይስጡ። እንዲሁም በሚቀጥለው ክፍል የተገለፀውን የማመቂያ ቅንጅቶች ፋይልን እና የመሸጎጫ ቅንጅቶችን የሚያካትት መስመር አለ።
የስክሪፕት ኮድ
# Make directory for NGINX cache
mkdir -p /var/cache/nginx/proxy

echo " Configuring NGINX"
cat > ${NGINX_CONF_DIR}/nginx.conf << EOM
user nginx;
worker_processes auto;
error_log  /var/log/nginx/error.log warn;
pid        /var/run/nginx.pid;
events {
    worker_connections  1024;
}
http {
    include       ${NGINX_CONF_DIR}/mime.types;
    default_type  application/octet-stream;
    log_format  main  '$remote_addr - $remote_user [$time_local] "$request" '
                      '$status $body_bytes_sent "$http_referer" '
                      '"$http_user_agent" "$http_x_forwarded_for"';
    access_log  /var/log/nginx/access.log  main;
    sendfile        on;
    client_max_body_size ${UPLOAD_MAX_FILESIZE};
    keepalive_timeout  65;
    # gzip settings
    include ${NGINX_CONF_DIR}/gzip_compression.conf;
    # Cache settings
    proxy_cache_path /var/cache/nginx/proxy
        levels=1:2
        keys_zone=wp_cache:10m
        max_size=10g
        inactive=60m
        use_temp_path=off;
    include ${NGINX_CONF_DIR}/conf.d/*.conf;
}
EOM
NGINX መጭመቂያ በማዘጋጀት ላይ
ይዘቱን ወደ ደንበኞች ከመላኩ በፊት በበረራ ላይ መጨናነቅ የጣቢያን አፈፃፀም ለማሻሻል ጥሩ መንገድ ነው ፣ ግን መጭመቅ በትክክል ከተዋቀረ ብቻ ነው። ይህ የስክሪፕቱ ክፍል በቅንብሮች ላይ የተመሰረተ ነው። .
የስክሪፕት ኮድ
cat > ${NGINX_CONF_DIR}/gzip_compression.conf << 'EOM'
# Credit: https://github.com/h5bp/server-configs-nginx/
# ----------------------------------------------------------------------
# | Compression                                                        |
# ----------------------------------------------------------------------
# https://nginx.org/en/docs/http/ngx_http_gzip_module.html
# Enable gzip compression.
# Default: off
gzip on;
# Compression level (1-9).
# 5 is a perfect compromise between size and CPU usage, offering about 75%
# reduction for most ASCII files (almost identical to level 9).
# Default: 1
gzip_comp_level 6;
# Don't compress anything that's already small and unlikely to shrink much if at
# all (the default is 20 bytes, which is bad as that usually leads to larger
# files after gzipping).
# Default: 20
gzip_min_length 256;
# Compress data even for clients that are connecting to us via proxies,
# identified by the "Via" header (required for CloudFront).
# Default: off
gzip_proxied any;
# Tell proxies to cache both the gzipped and regular version of a resource
# whenever the client's Accept-Encoding capabilities header varies;
# Avoids the issue where a non-gzip capable client (which is extremely rare
# today) would display gibberish if their proxy gave them the gzipped version.
# Default: off
gzip_vary on;
# Compress all output labeled with one of the following MIME-types.
# `text/html` is always compressed by gzip module.
# Default: text/html
gzip_types
  application/atom+xml
  application/geo+json
  application/javascript
  application/x-javascript
  application/json
  application/ld+json
  application/manifest+json
  application/rdf+xml
  application/rss+xml
  application/vnd.ms-fontobject
  application/wasm
  application/x-web-app-manifest+json
  application/xhtml+xml
  application/xml
  font/eot
  font/otf
  font/ttf
  image/bmp
  image/svg+xml
  text/cache-manifest
  text/calendar
  text/css
  text/javascript
  text/markdown
  text/plain
  text/xml
  text/vcard
  text/vnd.rim.location.xloc
  text/vtt
  text/x-component
  text/x-cross-domain-policy;
EOM
NGINX ን ማዋቀር ለ WordPress
ቀጥሎ፣ ስክሪፕቱ ለ የውቅር ፋይል ይፈጥራል WordPress default.conf በካታሎግ ውስጥ conf.d. እዚህ የተዋቀረ ነው፡-
- በሰርትቦት በኩል ከኑ ኢንክሪፕት እንስጥ የተቀበሉ የTLS ሰርተፊኬቶችን ማግበር (ማዋቀር በሚቀጥለው ክፍል ውስጥ ይሆናል)
- ከኑ ኢንክሪፕት በመጡ ምክሮች ላይ በመመስረት የTLS የደህንነት ቅንብሮችን በማዋቀር ላይ
- በነባሪነት ለ1 ሰአት የመሸጎጫ ጥያቄዎችን መዝለልን አንቃ
- ለሁለት የተለመዱ የተጠየቁ ፋይሎች፡- favicon.ico እና robots.txt የመዳረሻ ምዝግብ ማስታወሻን እንዲሁም ፋይል ካልተገኘ የስህተት ምዝግብ ማስታወሻን ያሰናክሉ።
- የተደበቁ ፋይሎችን እና አንዳንድ ፋይሎችን መድረስን ይከለክላል .phpሕገ-ወጥ መዳረሻን ወይም ያልታሰበ ጅምርን ለመከላከል
- የማይንቀሳቀሱ እና የቅርጸ-ቁምፊ ፋይሎችን የመዳረሻ ምዝግብ ማስታወሻን ያሰናክሉ።
- የራስጌ ቅንብር ለቅርጸ-ቁምፊ ፋይሎች
- ለindex.php እና ለሌሎች ስታቲስቲክስ ማዞሪያን በማከል ላይ።
የስክሪፕት ኮድ
cat > ${NGINX_CONF_DIR}/conf.d/default.conf << EOM
upstream unit_php_upstream {
    server 127.0.0.1:8080;
    keepalive 32;
}
server {
    listen 80;
    listen [::]:80;
    # ACME-challenge used by Certbot for Let's Encrypt
    location ^~ /.well-known/acme-challenge/ {
      root /var/www/certbot;
    }
    location / {
      return 301 https://${TLS_HOSTNAME}$request_uri;
    }
}
server {
    listen      443 ssl http2;
    listen [::]:443 ssl http2;
    server_name ${TLS_HOSTNAME};
    root        /var/www/wordpress/;
    # Let's Encrypt configuration
    ssl_certificate         ${CERT_DIR}/fullchain.pem;
    ssl_certificate_key     ${CERT_DIR}/privkey.pem;
    ssl_trusted_certificate ${CERT_DIR}/chain.pem;
    include ${NGINX_CONF_DIR}/options-ssl-nginx.conf;
    ssl_dhparam ${NGINX_CONF_DIR}/ssl-dhparams.pem;
    # OCSP stapling
    ssl_stapling on;
    ssl_stapling_verify on;
    # Proxy caching
    proxy_cache wp_cache;
    proxy_cache_valid 200 302 1h;
    proxy_cache_valid 404 1m;
    proxy_cache_revalidate on;
    proxy_cache_background_update on;
    proxy_cache_lock on;
    proxy_cache_use_stale error timeout http_500 http_502 http_503 http_504;
    location = /favicon.ico {
        log_not_found off;
        access_log off;
    }
    location = /robots.txt {
        allow all;
        log_not_found off;
        access_log off;
    }

    # Deny all attempts to access hidden files such as .htaccess, .htpasswd,
    # .DS_Store (Mac)
    # Keep logging the requests to parse later (or to pass to firewall utilities
    # such as fail2ban)
    location ~ /. {
        deny all;
    }
    # Deny access to any files with a .php extension in the uploads directory;
    # works in subdirectory installs and also in multi-site network.
    # Keep logging the requests to parse later (or to pass to firewall utilities
    # such as fail2ban).
    location ~* /(?:uploads|files)/.*.php$ {
        deny all;
    }
    # WordPress: deny access to wp-content, wp-includes PHP files
    location ~* ^/(?:wp-content|wp-includes)/.*.php$ {
        deny all;
    }
    # Deny public access to wp-config.php
    location ~* wp-config.php {
        deny all;
    }
    # Do not log access for static assets, media
    location ~* .(?:css(.map)?|js(.map)?|jpe?g|png|gif|ico|cur|heic|webp|tiff?|mp3|m4a|aac|ogg|midi?|wav|mp4|mov|webm|mpe?g|avi|ogv|flv|wmv)$ {
        access_log off;
    }
    location ~* .(?:svgz?|ttf|ttc|otf|eot|woff2?)$ {
        add_header Access-Control-Allow-Origin "*";
        access_log off;
    }
    location / {
        try_files $uri @index_php;
    }
    location @index_php {
        proxy_socket_keepalive on;
        proxy_http_version 1.1;
        proxy_set_header Connection "";
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
        proxy_set_header Host $host;
        proxy_pass       http://unit_php_upstream;
    }
    location ~* .php$ {
        proxy_socket_keepalive on;
        proxy_http_version 1.1;
        proxy_set_header Connection "";
        proxy_set_header X-Real-IP $remote_addr;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
        proxy_set_header Host $host;
        try_files        $uri =404;
        proxy_pass       http://unit_php_upstream;
    }
}
EOM
ሰርትቦትን ከኑ ኢንክሪፕት እናመስጥር ላሉ ሰርተፊኬቶች በማዘጋጀት እና በራስ-እድሳት
የTLS ሰርተፍኬቶችን ከእንክሪፕት እንስጠራው በራስ ሰር እንድታድሱ የሚያስችል ከኤሌክትሮኒክስ ፍሮንትየር ፋውንዴሽን (ኢኤፍኤፍ) ነፃ መሳሪያ ነው። ስክሪፕቱ Certbotን በNGINX ውስጥ እናመስጥርን የምስክር ወረቀቶችን ለመስራት ለማዋቀር የሚከተለውን ያደርጋል።
- NGINXን ያቆማል
- ማውረዶች የሚመከሩ የTLS ቅንብሮች
- ለጣቢያው የምስክር ወረቀቶችን ለማግኘት Certbot ን ያስኬዳል
- የምስክር ወረቀቶችን ለመጠቀም NGINXን እንደገና ያስጀምራል።
- የምስክር ወረቀቶች መታደስ ካለባቸው ለመፈተሽ Certbot በየቀኑ 3፡24 AM ላይ እንዲሰራ ያዋቅራል፣ እና አስፈላጊ ከሆነ አዲስ የምስክር ወረቀቶችን ያውርዱ እና NGINXን እንደገና ያስጀምሩ።
የስክሪፕት ኮድ
echo " Stopping NGINX in order to set up Let's Encrypt"
service nginx stop

mkdir -p /var/www/certbot
chown www-data:www-data /var/www/certbot
chmod g+s /var/www/certbot

if [ ! -f ${NGINX_CONF_DIR}/options-ssl-nginx.conf ]; then
  echo " Downloading recommended TLS parameters"
  curl --retry 6 -Ls -z "Tue, 14 Apr 2020 16:36:07 GMT"
    -o "${NGINX_CONF_DIR}/options-ssl-nginx.conf"
    "https://raw.githubusercontent.com/certbot/certbot/master/certbot-nginx/certbot_nginx/_internal/tls_configs/options-ssl-nginx.conf"
    || echo "Couldn't download latest options-ssl-nginx.conf"
fi

if [ ! -f ${NGINX_CONF_DIR}/ssl-dhparams.pem ]; then
  echo " Downloading recommended TLS DH parameters"
  curl --retry 6 -Ls -z "Tue, 14 Apr 2020 16:49:18 GMT"
    -o "${NGINX_CONF_DIR}/ssl-dhparams.pem"
    "https://raw.githubusercontent.com/certbot/certbot/master/certbot/certbot/ssl-dhparams.pem"
    || echo "Couldn't download latest ssl-dhparams.pem"
fi

# If tls_certs_init.sh hasn't been run before, remove the self-signed certs
if [ ! -d "/etc/letsencrypt/accounts" ]; then
  echo " Removing self-signed certificates"
  rm -rf "${CERT_DIR}"
fi

if [ "" = "${LETS_ENCRYPT_STAGING:-}" ] || [ "0" = "${LETS_ENCRYPT_STAGING}" ]; then
  CERTBOT_STAGING_FLAG=""
else
  CERTBOT_STAGING_FLAG="--staging"
fi

if [ ! -f "${CERT_DIR}/fullchain.pem" ]; then
  echo " Generating certificates with Let's Encrypt"
  certbot certonly --standalone
         -m "${WORDPRESS_ADMIN_EMAIL}"
         ${CERTBOT_STAGING_FLAG}
         --agree-tos --force-renewal --non-interactive
         -d "${TLS_HOSTNAME}"
fi

echo " Starting NGINX in order to use new configuration"
service nginx start

# Write crontab for periodic Let's Encrypt cert renewal
if [ "$(crontab -l | grep -m1 'certbot renew')" == "" ]; then
  echo " Adding certbot to crontab for automatic Let's Encrypt renewal"
  (crontab -l 2>/dev/null; echo "24 3 * * * certbot renew --nginx --post-hook 'service nginx reload'") | crontab -
fi
የጣቢያዎን ተጨማሪ ማበጀት።
የኛ ስክሪፕት NGINX እና NGINX Unitን ለምርት ዝግጁ የሆነ ጣቢያ በ TLSSSL እንዲያገለግል እንዴት እንደሚያዋቅር ከላይ ተነጋግረናል። እንዲሁም እንደ ፍላጎቶችዎ ወደፊት ማከል ይችላሉ፡
- ድጋፍ ፣ በ HTTPS ላይ በበረራ ላይ የተሻሻለ መጭመቂያ
- с በጣቢያዎ ላይ አውቶማቲክ ጥቃቶችን ለመከላከል
- ለ WordPress, ለእርስዎ ተስማሚ
- በ እገዛ (በርቷል Ubuntu)
- ፖስትፊክስ ወይም msmtp ወደ WordPress ደብዳቤ መላክ ይችል ነበር
- ምን ያህል ትራፊክ ማስተናገድ እንደሚችል ለመረዳት ጣቢያዎን በመፈተሽ ላይ
ለተሻለ የጣቢያ አፈጻጸም፣ ወደ ማላቅ እንመክራለን በክፍት ምንጭ NGINX ላይ የተመሠረተ የእኛ የንግድ ፣ የድርጅት ደረጃ ምርታችን። ተመዝጋቢዎቹ በተለዋዋጭ የተጫነ ብሮትሊ ሞጁል እንዲሁም (ለተጨማሪ ክፍያ) ይቀበላሉ። . እኛም እናቀርባለን። ከF5 በኢንዱስትሪ መሪ የደህንነት ቴክኖሎጂ ላይ የተመሰረተ የ WAF ሞጁል ለ NGINX Plus።
ማሳሰቢያ በጣም የተጫነ ጣቢያን ለመደገፍ, ስፔሻሊስቶችን ማነጋገር ይችላሉ . በማንኛውም ጭነት ውስጥ የእርስዎን ድር ጣቢያ ወይም አገልግሎት ፈጣን እና አስተማማኝ አሠራር እናረጋግጣለን።
ምንጭ: hab.com
