

Exploit for a 0day vulnerability is already being sold on relevant forums.
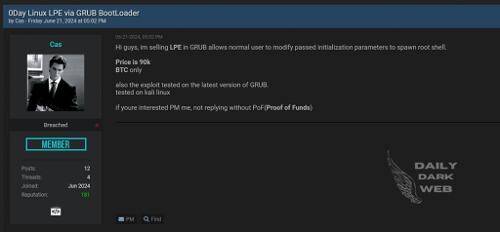
On June 21, information about the sale of an exploit for a zero-day vulnerability in the GRUB bootloader for Linux appeared on one of the forums, allowing for local privilege escalation (LPE).
According to Dark Web Intelligence, the attacker claims to have found a vulnerability in GRUB that allows bypassing authentication mechanisms and obtaining root access on the system.
According to a message from a dark forum participant under the nickname 'Cas', the vulnerability affects GRUB — a critical component of most Linux systems that manages the booting process, allowing attackers to install hidden and persistent malware that can be quite difficult to detect and eliminate. The exploit is being sold for $90,000.
It is noteworthy that GRUB has been targeted in attacks in the past. Thus, in 2015, a vulnerability CVE-2015-8370 was discovered that allowed bypassing authentication by pressing the backspace key 28 times during the username entry stage in GRUB. This vulnerability affected GRUB versions from 1.98 to 2.02 and was widely exploited until a patch was released. In 2020, another vulnerability was identified — CVE-2020-10713, also known as BootHole, which allowed malware installation during the boot process.
Major Linux distributions, such as Debian, RedHat, and Ubuntu, promptly released recommendations and patches for previous GRUB vulnerabilities and are likely to do so this time as well. However, the problem is exacerbated by the fact that the vulnerability was discovered by malicious actors, not ethical hackers. This means that its discovery and fixing by security researchers may take significantly longer.
Kilde: linux.org.ru
