

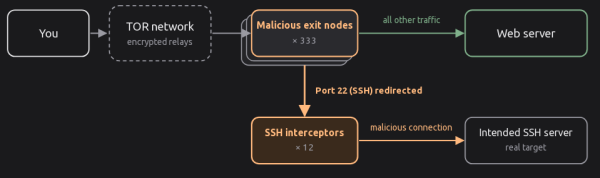
Details of the incident have been published, during which attackers were able to gain control over 333 exit nodes in the Tor network (there are about 3000 exit nodes in total in Tor) and organize the interception of unencrypted traffic and redirection of SSH connections on them. The attack began on October 2 (Friday evening) but was identified and began to be blocked on October 4. On October 5, all compromised servers were disconnected by operators or the attackers themselves. Investigations revealed that the attackers gained access to the servers two months prior to the attack on Tor users and installed the Ebury 1.8.3 malware on the compromised systems.
The purpose of the attack was to intercept passwords, keys, and confidential information in unencrypted transit traffic, as well as capture passwords for SSH. In analyzing the unencrypted traffic, the attackers focused on unencrypted requests to mail servers. To encourage a rollback to unencrypted work on the exit nodes, blocking of network ports was carried out that were used to establish an encrypted communication channel with the mail servers. Servern. Unencrypted traffic was analyzed on the fly.
To collect SSH passwords, SSH requests were redirected to one of 12 attacker servers. These servers accepted the SSH connection and prompted for a password on behalf of Server, to which the connection was being made. Since the host keys did not match, SSH on the client side issued a warning about connecting to an unknown zu einem Server.
If the user ignored this warning and entered the password for the connection, then the malicious Server transmitted the connection to the legitimate target SSH server, stored the password entered by the victim, and intercepted information about actions in the SSH session. At the same time, it connected to the target server with the captured password and installed the Ebury malware on it. By gaining control over Linux servers that were not exit nodes of Tor, the attackers changed the settings in the torrc file and turned them into new malicious Tor exit nodes.
Um alle bösartigen Exit-Knoten zu identifizieren, verwendete der Forscher das Tool exitmap, um alle Exit-Knoten zu scannen, eine SSH-Verbindung über jeden von ihnen herzustellen und zu überprüfen, ob eine Umleitung der Anfrage stattgefunden hat. Wie genau die Angreifer Zugriff auf die kompromittierten Tor-Knoten erhielten, ist noch unklar, unter anderem gibt es
Vermutungen über eine Kompromittierung der Hosting-Anbieter.
Quelle: opennet.ru
