

Israeli security researcher Ido Hoorvitch from Tel Aviv published the results of an experiment studying the reliability of passwords used to access wireless networks. During the research on intercepted frames with PMKID identifiers, he was able to crack passwords for 3,663 out of 5,000 (73%) studied wireless networks in Tel Aviv. The conclusion drawn was that most wireless network owners set unreliable passwords, susceptible to hash cracking, making their networks vulnerable to attacks using standard utilities like hashcat, hcxtools, and hcxdumptool.
Ido used a portable computer with Ubuntu Linux to intercept packets from wireless networks, placing it in a backpack and wandering around the city until he managed to capture frames with PMKID (Pairwise Master Key Identifier) from five thousand different wireless networks. After that, he employed a computer with 8 NVIDIA QUADRO RTX 8000 48GB GPUs for cracking passwords from the hashes extracted from the PMKID identifier. The cracking performance on this setup server was almost 7 million hashes per second. For comparison, a regular laptop achieves about 200,000 hashes per second, which is sufficient to crack a single 10-digit password in approximately 9 minutes.
To speed up the cracking, the attempt was limited to sequences consisting only of 8 lowercase letters, along with 8, 9, or 10 digits. This restriction was enough to determine passwords for 3,663 out of 5,000 networks. The most common were 10-digit passwords, used in 2,349 networks. Eight-digit passwords were present in 596 networks, nine-digit in 368, while 8 lowercase letter passwords were used in 320. A repeat attempt using the rockyou.txt dictionary, which is 133 MB in size, allowed for the immediate recovery of 900 passwords.
It is assumed that the situation concerning password reliability in wireless networks in other cities and countries is roughly the same, and most passwords can be cracked within a few hours, spending around $50 on a wireless card that supports monitoring mode (the experiment used the ALFA Network AWUS036ACH card). The PMKID-based attack is applicable only to access points that support roaming, but as practice has shown, most manufacturers do not disable this feature.
The attack utilized a standard method of hacking wireless networks with WPA2, known since 2018. Unlike the classical method, which requires intercepting handshake packets during a user's connection, the method based on intercepting PMKID is not tied to a new user's connection to the network and can be carried out at any time. To obtain data sufficient to start password cracking, only the interception of a single packet with the PMKID identifier is necessary. Such packets can be obtained both in passive mode, tracking roaming-related activity, and by forcibly initiating the transmission of PMKID packets into the air by sending an authentication request to the access point.
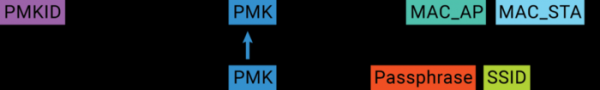
PMKID is a hash generated using the password, the MAC address of the access point, the MAC address of the client, and the wireless network name (SSID). The last three parameters (MAC AP, MAC Station, and SSID) are initially known, allowing for dictionary attack methods to determine the password, similar to how user passwords in a system can be cracked when their hash is leaked. Thus, the security of accessing a wireless network entirely depends on the strength of the set password.
Source: opennet.ru
