

Three libraries containing malicious code have been identified in the PyPI (Python Package Index) catalog. Before the issues were discovered and the packages were removed from the catalog, they had been downloaded almost 15,000 times in total.
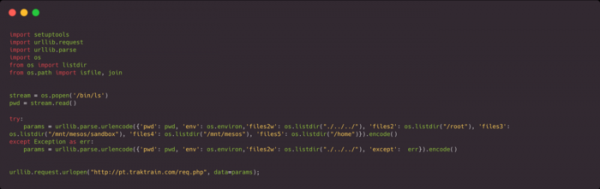
The packages dpp-client (10,194 downloads) and dpp-client1234 (1,536 downloads) were distributed since February and included code to send the contents of environment variables, which could include access keys, tokens, or passwords for continuous integration systems or cloud environments such as AWS. The packages also transmitted to an external host a list of the contents of the directories ‘/home’, ‘/mnt/mesos/’, and ‘mnt/mesos/sandbox.’
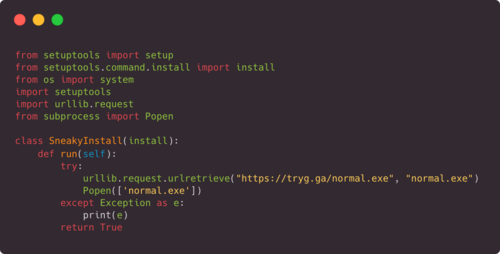
The package aws-login0tool (3,042 downloads) was uploaded to the PyPI repository on December 1 and included code to download and execute a trojan application to take control over hosts running Windows. The chosen package name was based on the assumption that the keys ‘0’ and ‘-’ are close together, increasing the likelihood that a developer would type ‘aws-login0tool’ instead of ‘aws-login-tool.’
The problematic packages were identified during a simple experiment, where a portion of PyPI packages (about 200,000 out of 330,000 packages in the repository) was downloaded using the Bandersnatch utility. Afterward, packages in which the setup.py file mentioned the call ‘import urllib.request’, typically used for sending requests to external hosts, were isolated and analyzed using the grep utility.
Source: opennet.ru
