

The release of the lightweight HTTP server lighttpd 1.4.64 has taken place. The new version includes 95 changes, including previously planned updates to default values and a cleaning of outdated functionality.
- The default timeout for graceful restart/shutdown operations has been reduced from infinity to 8 seconds. The timeout can be configured using the 'server.graceful-shutdown-timeout' option.
- The transition to using the build with the PCRE2 library (—with-pcre2) has been implemented; to revert to the old PCRE variant, the '—with-pcre' option can be used.
- Modules previously declared deprecated have been removed:
- mod_geoip (you should use mod_maxminddb),
- mod_authn_mysql (you should use mod_authn_dbi),
- mod_mysql_vhost (you should use mod_vhostdb_dbi),
- mod_cml (you should use mod_magnet),
- mod_flv_streaming (has lost relevance since the end of Adobe Flash's life),
- mod_trigger_b4_dl (you should use a replacement in Lua).
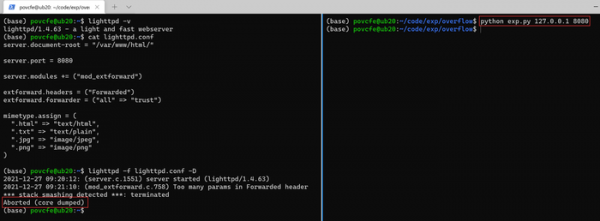
In lighttpd 1.4.64, a vulnerability (CVE-2022-22707) in the mod_extforward module has also been addressed, which could lead to a 4-byte buffer overflow when processing data in the Forwarded HTTP header. According to the developers, the issue is limited to denial of service and allows for remote initiation of the background process's crash. Exploitation is only possible if the Forwarded header handler is enabled and does not occur in default configuration.
Source: opennet.ru
