

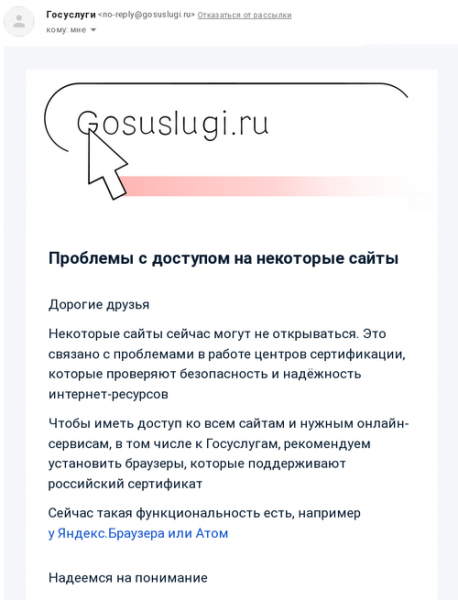
Users of the Russian Federation's government services portal (gosuslugi.ru) received a notification about the creation of a state certification authority with its own root TLS certificate, which is not included in the root certificate stores of operating systems and major browsers. Certificates are issued on a voluntary basis to legal entities and are intended for use in the event of revocation or non-renewal of TLS certificates due to sanctions. For example, certification authorities under U.S. jurisdiction, such as DigiCert, have stopped issuing certificates for the websites of organizations listed in the sanctions list.
Currently, the state root certificate is integrated only into Yandex.Browser and Atom products. To ensure trust in websites using certificates from the state certification authority in other browsers, the root certificate must be manually added to the system or browser certificate store.
Among the websites that have already received state TLS certificates are various banks (Sber, VTB, Central Bank) and organizations and projects affiliated with government structures. At the time of this news, traditional TLS certificates supported by all browsers continue to be used on the main websites of Sber and VTB, but specific subdomains (for example, online-alpha.vtb.ru) have already switched to the new certificate.
In the event of the imposition of a new certification authority or the discovery of abuses, such as carrying out MITM attacks, it is likely that the manufacturers of the Firefox, Chrome, Edge, and Safari browsers will take action to add the problematic root certificate to the revoked certificates list, as was already done with the certificate implemented for intercepting HTTPS traffic in Kazakhstan.
Source: opennet.ru
