

Google has begun rolling out a new firmware based on the Fuchsia OS for the smart photo frames Nest Hub Max, released since 2019. In the first phase, the Fuchsia-based firmware will be delivered to participants of the Google Preview Program, and if no unforeseen issues arise during the trial implementation, the firmware will be applied to other Nest Hub Max users' devices.
The Nest Hub Max has become the second consumer device equipped with the Fuchsia operating system. A year ago, the Fuchsia-based firmware was first received by the Nest Hub model, which features a smaller screen and lacks the built-in camera used for security and surveillance systems. Despite the operating system change, the user interface and functionality remain fully intact, and end users should notice no differences since the interface is built on the Flutter framework and abstracted from low-level components. Previously, the Nest Hub Max devices, which combine the functions of a photo frame, multimedia system, and smart home management interface, used firmware based on the Cast shell and the Linux kernel.
The Fuchsia OS has been developed by Google since 2016, addressing scaling and security shortcomings inherent in the Android platform. The system is based on the Zircon microkernel, derived from the LK project, expanded for use across various classes of devices, including smartphones and personal computers. Zircon extends LK with process and shared library support, user-level capabilities, an object processing system, and a security model based on capabilities. Drivers are implemented as dynamic libraries running in user space, loaded by the devhost process and managed by the device manager (devmg, Device Manager).
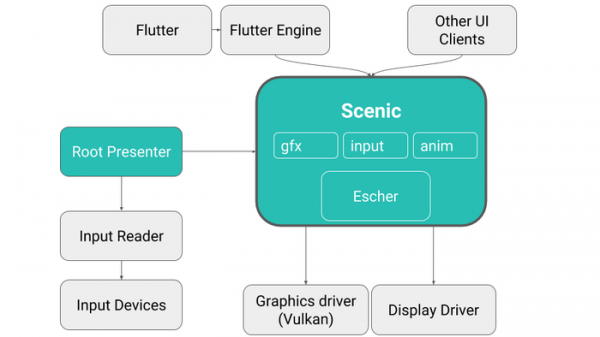
Fuchsia has its own graphical interface developed in Dart using the Flutter framework. The project also includes the development of the user interface framework Peridot, the package manager Fargo, the standard library libc, the rendering system Escher, the Vulkan driver Magma, the compositor Scenic, the file systems MinFS, MemFS, ThinFS (FAT in Go), and Blobfs, as well as the partition manager FVM. For application development, support is provided for C/C++ and Dart, with Rust permitted in system components, Go in the network stack, and Python in the build system.
During boot, a system manager is used, which includes appmgr for creating the initial program environment, sysmgr for forming the boot environment, and basemgr for configuring the user environment and organizing system login. An advanced sandbox isolation system ensures security, where new processes have no access to kernel objects, cannot allocate memory, and cannot execute code. Resource access is managed through a namespace system that defines available permissions. The platform provides a framework for creating components that are programs running in their own sandbox, able to interact with other components via IPC.
Source: opennet.ru
