

After two years of development, the release of Kata Containers 3.0 has been published, advancing the stack for running containers using full-fledged virtualization mechanisms for isolation. The project was created by Intel and Hyper by merging Clear Containers and runV technologies. The code is written in Go and Rust and is distributed under the Apache 2.0 license. The project is overseen by a working group established under the independent OpenStack Foundation, which includes companies such as Canonical, China Mobile, Dell/EMC, EasyStack, Google, Huawei, NetApp, Red Hat, SUSE, and ZTE.
The core of Kata is a runtime that enables the creation of compact virtual machines running with a full hypervisor instead of traditional containers that use a shared Linux kernel and are isolated through namespaces and cgroups. The use of of virtual machines provides a higher level of security, protecting against attacks resulting from the exploitation of vulnerabilities in the Linux kernel.
Kata Containers is geared towards integration into existing container isolation infrastructures with the possibility of using such virtual machines to enhance the security of traditional containers. The project provides mechanisms to ensure compatibility of lightweight virtual machines with various container isolation infrastructures, container orchestration platforms, and specifications such as OCI (Open Container Initiative), CRI (Container Runtime Interface), and CNI (Container Networking Interface). Tools for integration with Docker, Kubernetes, QEMU, and OpenStack are available.
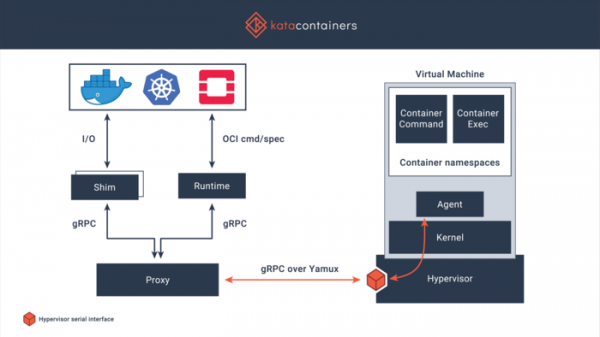
Integration with container management systems is achieved through a layer that simulates container management, which accesses the controlling agent in the virtual machine through a gRPC interface and a special proxy. Inside the virtual environment, which is launched by the hypervisor, a specially optimized Linux kernel is used, containing only the minimum set of necessary features.
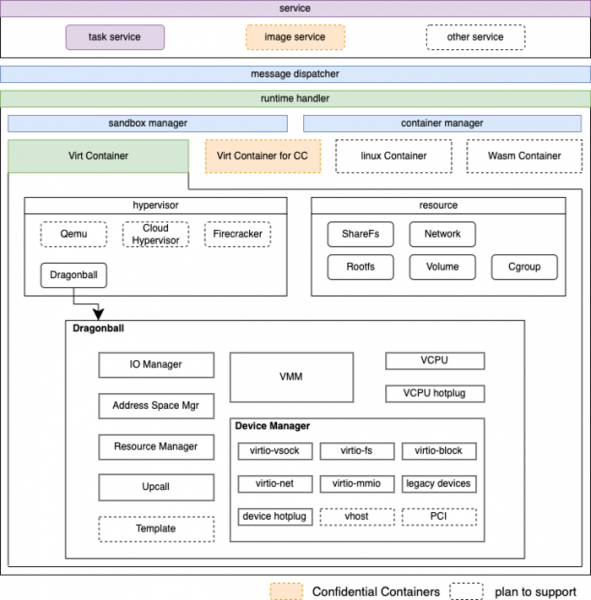
Dragonball Sandbox (a KVM-based hypervisor optimized for containers) is supported as the hypervisor, along with QEMU tools, Firecracker, and Cloud Hypervisor. The environment includes an initialization daemon and an agent. The agent facilitates the execution of user-defined container images in OCI format for Docker and CRI for Kubernetes. When used with Docker, a separate environment is created for each container. the virtual machine, meaning that the environment running on top of the hypervisor is used for nested container execution.
To reduce memory usage, the DAX mechanism (direct access to the file system bypassing the page cache without using block device levels) is applied, while the KSM (Kernel Samepage Merging) technology is used for deduplicating identical memory regions, allowing for resource sharing of the host system and connecting a shared template of the environment to different guest systems.
In the new version:
- An alternative runtime (runtime-rs) has been proposed, creating the contents of containers, written in Rust (the previously supplied runtime was written in Go). The runtime is compatible with OCI, CRI-O, and Containerd, allowing its use with Docker and Kubernetes.
- A new hypervisor dragonball has been proposed, based on KVM and rust-vmm.
- Support for GPU access passthrough using VFIO has been added.
- Support for cgroup v2 has been added.
- Support has been implemented for overriding settings without modifying the main configuration file by replacing blocks in separate files placed in the 'config.d/' directory.
- A new library for safe file path handling has been engaged in components written in Rust.
- The virtiofsd component (written in C) has been replaced with virtiofsd-rs (written in Rust).
- Support for sandbox isolation of QEMU components has been added.
- In QEMU, the io_uring API has been utilized for asynchronous input/output.
- For QEMU and Cloud-hypervisor, support for Intel TDX (Trusted Domain Extensions) has been implemented.
- Components updated: QEMU 6.2.0, Cloud-hypervisor 26.0, Firecracker 1.1.0, Linux kernel 5.19.2.
Source: opennet.ru
