

Sysdig, the company behind the open-source system monitoring tool of the same name, published the results of a study of over 250,000 Linux container images hosted in the Docker Hub catalog without any signs of being verified or official images. In total, 1,652 images were classified as malicious.
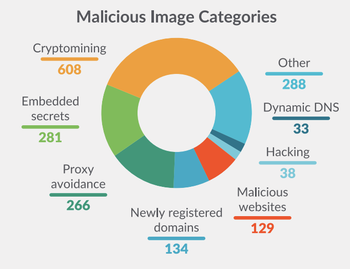
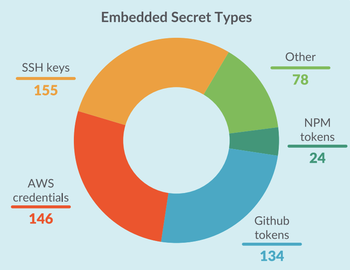
Among the images, 608 contained components for cryptocurrency mining, 288 left access tokens (155 with SSH keys, 146 with AWS tokens, 134 with GitHub tokens, and 24 with NPM API tokens), 266 had means to bypass firewalls through proxies, 134 had recently registered domains, and 129 made calls to websites recognized as malicious.
Some images with cryptocurrency miners aimed at attracting users used names that included the titles of well-known open-source projects, such as ubuntu, golang, joomla, liferay, and drupal, or applied a technique called typosquatting (assigning similar names that differ by a few characters). Among the most popular malicious images were vibersastra/ubuntu and vibersastra/golang, which were downloaded over 10,000 and 6,900 times, respectively.
Source: opennet.ru
