

The developers of the anonymous Tor network have published the results of an audit of the Tor Browser and the tools developed by the project, including OONI Probe, rdsys, BridgeDB, and Conjure, which are used to bypass censorship. The audit was conducted by Cure53 from November 2022 to April 2023.
During the assessment, 9 vulnerabilities were identified, two of which were classified as critical, one was assigned a medium severity level, and 6 were categorized as minor issues. Additionally, 10 problems unrelated to security deficiencies were found in the codebase. Overall, the Tor project code was noted as being consistent with safe programming practices.
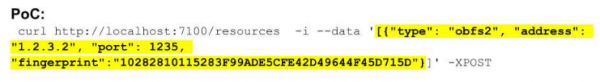
The first critical vulnerability was present in the backend of the distributed system rdsys, which provides resources such as proxy lists and download links to censored users. The vulnerability was caused by a lack of authentication when accessing the resource registration handler, allowing an attacker to register their own malicious resource for delivery to users. Exploitation consists of sending an HTTP request to the rdsys handler.
The second critical vulnerability found in the Tor Browser was due to a lack of verification of the digital signature when obtaining the list of bridge nodes via rdsys and BridgeDB. Since the list is loaded into the browser before connecting to the anonymous Tor network, the absence of verification with a cryptographic digital signature allowed an attacker to tamper with the contents of the list, for example, through connection interception or hacking server, through which the list is distributed. In the event of a successful attack, the attacker could direct users to their own compromised bridge node.
A medium-severity vulnerability was present in the rdsys subsystem in the deployment script and allowed an attacker to elevate their privileges from the user nobody to the user rdsys, given access to server and the ability to write to the temporary files directory. Exploiting the vulnerability involves replacing the executable file placed in the /tmp directory. Gaining rdsys user rights allows the attacker to make changes to executables run through rdsys.
Low-risk vulnerabilities were mainly associated with the use of outdated dependencies that contained known vulnerabilities or the potential for denial of service. Among the minor vulnerabilities in Tor Browser, there is the possibility of bypassing the JavaScript execution ban when the highest level of protection is set, lack of restrictions on file uploads, and potential information leakage through the user’s homepage, which allows tracking users between restarts.
Currently, all vulnerabilities have been addressed, including the implementation of authentication for all rdsys handlers and the addition of verification for the uploaded lists in Tor Browser through digital signatures.
Additionally, it's worth noting the release of Tor Browser 13.0.1. This release is synchronized with the Firefox 115.4.0 ESR codebase, which has fixed 19 vulnerabilities (13 classified as critical). Vulnerability fixes from the Firefox 119 branch have been ported to Tor Browser 13.0.1 for Android.
Source: opennet.ru
