

The release of the Arkime 5.0 system for capturing, storing, and indexing network packets has been published. This system provides tools for visual traffic flow assessment and finding information related to network activity. The project was originally developed by AOL to create an open-source alternative to commercial network packet processing platforms, supporting deployment on private servers and capable of scaling to handle traffic at speeds of tens of gigabits per second. The traffic capture component is written in C, with the interface implemented in Node.js/JavaScript. The source code is distributed under the Apache 2.0 license. It is compatible with Linux and FreeBSD, with ready-made packages prepared for Arch Linux, RHEL/CentOS, and Ubuntu.
Arkime includes tools for capturing and indexing traffic in PCAP format and provides means for quick access to indexed data. The use of the standard PCAP format simplifies integration with existing traffic analyzers like Wireshark. The amount of stored data is limited only by the size of the available disk array. Session metadata is indexed in a cluster based on the Elasticsearch or OpenSearch engine. The traffic capture component operates in multi-threaded mode, handling tasks such as monitoring, recording PCAP dumps to disk, parsing captured packets, and sending metadata about sessions (SPI, Stateful Packet Inspection) and protocols to the Elasticsearch/OpenSearch cluster. PCAP files can be stored in an encrypted format.
A web interface is provided for analyzing the accumulated information, allowing navigation, searching, and exporting samples. The web interface offers several viewing modes—from overall statistics, connection maps, and visual graphs showing changes in network activity to tools for studying individual sessions, analyzing activity by used protocols, and parsing data from PCAP dumps. An API is also provided, enabling the transfer of captured packet data in PCAP format and parsed sessions in JSON format to third-party applications.
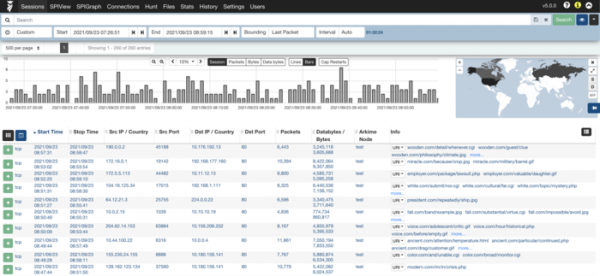
In the new version:
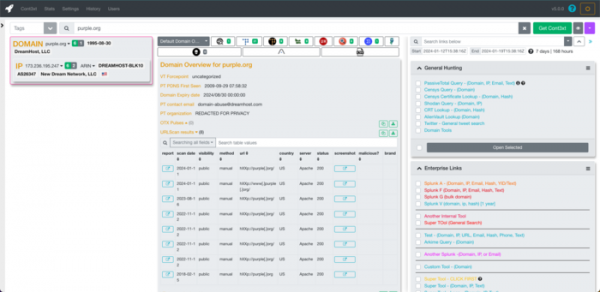
- The ability to send combined search queries for information via the Cont3xt service has been added to gather available information from various open sources (OSINT) simultaneously about multiple entities.

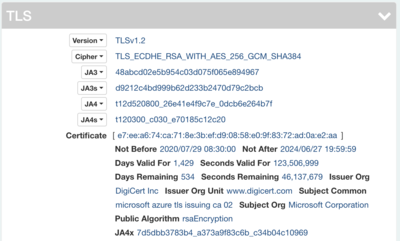
- Support for traffic fingerprinting methods JA4 and JA4+ has been added to identify network protocols and applications.

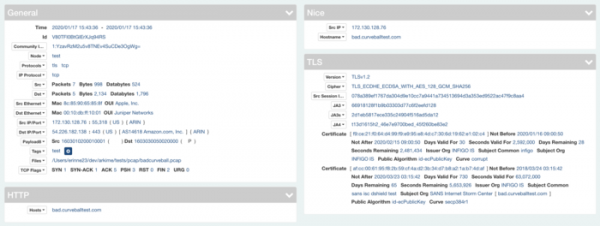
- The design of the detailed session information block has been modified to minimize unused space and implement a two-column layout for larger screens.

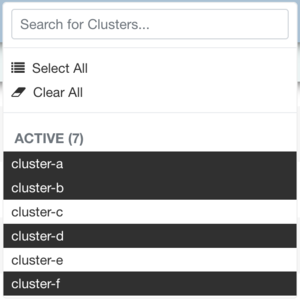
- Dropdown blocks for searching across multiple instances of the statistics viewing interface (Viewer) have been added to the Files, History, and Stats tabs.

- The authorization system has been unified and separated into a distinct module, now used across all Arkime applications. Instead of the default anonymous authorization mode, the digest method is now employed. New authorization modes have been added: basic, form, basic+form, basic+oidc, headerOnly, header+digest, and header+basic.
- All applications have been migrated to a unified configuration subsystem that supports processing settings in various formats (ini, json, yaml) and can load configurations from different sources, such as from disk, over the network via HTTPS, or from OpenSearch/Elasticsearch.
- Support for importing saved (offline) PCAP dumps has been added with the ability to upload via URL over HTTPS or from Amazon S3 storage, without the need for prior saving on the local system.
Source: opennet.ru
