

Researchers from Aqua Security have highlighted the potential for an attack on users of the Ubuntu distribution, leveraging the peculiarities of the 'command-not-found' handler, which provides suggestions when attempting to launch a program that is not available on the system. The issue is that, in evaluating commands that are not present in the system, 'command-not-found' considers not only packages from the official repositories but also snap packages from the snapcraft.io directory.
When generating recommendations based on the contents of the snapcraft.io directory, the 'command-not-found' handler does not take into account the status of the package and encompasses packages added by unverified users. Thus, an attacker can upload a package with hidden malicious content to snapcraft.io, whose name intersects with existing DEB packages, or create names for programs that do not originally exist in the repository or are fictitious applications, with names reflecting common typos and errors made by users when typing popular utility names.
For example, an attacker could upload packages named 'tracert' and 'tcpdamp', anticipating that the user may err when typing the names of the utilities 'traceroute' and 'tcpdump', leading 'command-not-found' to recommend installing the malicious packages hosted on snapcraft.io. The user may not notice the deception and believe that the system is recommending only verified packages. The attacker could also upload a package to snapcraft.io with a name overlapping with existing deb packages, in which case 'command-not-found' would yield two installation recommendations for deb and snap, and the user might opt for snap, thinking it is more secure or tempted by a newer version.
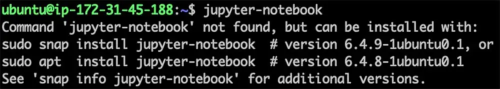
Applications in the snap format, which are subject to automatic review on snapcraft.io, can only run in an isolated environment (snap packages without isolation are only published after manual review). It may be sufficient for an attacker to operate in an isolated environment with network access, for example, for cryptocurrency mining, launching DDoS attacks, or sending spam.
An attacker can also use methods in malicious packages to bypass isolation, such as exploiting unpatched vulnerabilities in the kernel and isolation mechanisms, leveraging snap interfaces to access external resources (for covert audio and video recording), or capturing keyboard input when using the X11 protocol (to create functioning keyloggers in a sandbox environment).
Source: opennet.ru
