

The release of the Apache HTTP Server 2.4.62 is now available, addressing two vulnerabilities and introducing six modifications. The first vulnerability (CVE-2024-40898) allows for an SSRF (Server-side request forgery) attack on mod_rewrite. This issue only manifests on the Windows platform and can lead to the leakage of NTLM hashes to a server controlled by the attacker when specifically crafted requests are sent.
The second vulnerability (CVE-2024-40725) allows for viewing the code of scripts processed through the AddType directive. For instance, a specially crafted request to a PHP script may display its content rather than execute it. The fix blocks an additional exploitation variant of vulnerability CVE-2024-39884, which was addressed in version 2.4.61.
Among the non-security-related changes is the addition in mod_ssl of the ability to load certificates and keys from stores that support the pkcs11 standard.
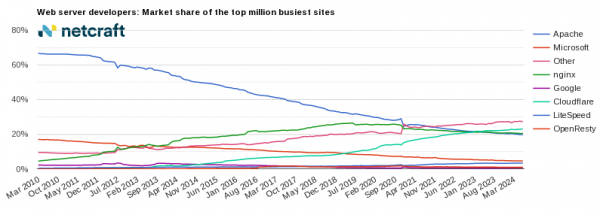
According to Netcraft's June report, approximately 212 million sites (down from 228 million a year ago) are powered by the Apache HTTP Server. The share of Apache httpd is estimated at 19.28% of all sites, making it the second most popular in this category (Nginx holds 21.35%, Cloudflare 11.05%, OpenResty - based on nginx and LuaJIT - 0.79%). When only considering active sites, Apache ranks first with a share of 19.13% (Nginx 18.09%, Cloudflare 14.80%, Google 10.01%). Among the million most visited sites globally, Apache is in third place with a share of 19.69% (led by Cloudflare 23.10% and Nginx 20.50%).
Source: opennet.ru
