

The Linux Foundation, in collaboration with Harvard's Innovation Lab, has prepared a new edition of the Census III study aimed at identifying the most widely used open-source projects in need of prioritized security audits. The study analyzed shared open code implicitly used in various corporate projects in the form of dependencies downloaded from external repositories. In total, more than 12 million open libraries used in applications across 10,000 different companies were examined.
Based on the collected statistics, lists of the 500 most frequently used libraries have been compiled, the security and quality of which require special attention, as vulnerabilities and compromises in third-party dependencies can undermine all efforts to enhance the security of the core product. In total, 8 lists have been proposed, with content ranked according to various criteria, such as availability in the NPM repository and presence of version information when determining dependencies.
Some findings:
- 17% of the 50 most popular projects not represented in the NPM repository have only one developer, while 40% have one or two developers who made 80% of the commits.
- Compared to the previous report from 2022, there has been an increase in the use of packages for interacting with cloud services among important packages.
- The transition of projects from Python 2 to Python 3 continues.
- The popularity of Maven packages remains strong, and the use of packages from PIP (Python), Cargo (Rust), and NuGet (.NET) repositories is increasing.
- As before, the need for standardized naming schemes for software components is evident.
- The relevance of securing developer accounts has increased. Many of the most sought-after packages are hosted under the accounts of individual developers, which are less secure than those created under the accounts of organizations.
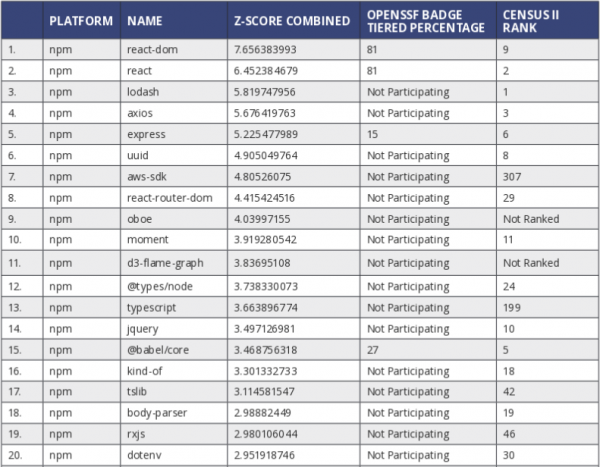
- The 20 most frequently used JavaScript packages from the NPM repository, downloaded by applications without version binding:

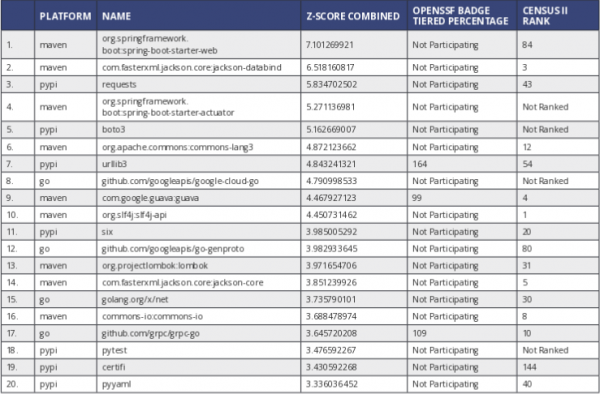
- The 20 most frequently used packages from repositories other than NPM, downloaded by applications without version binding:

Source: opennet.ru
