

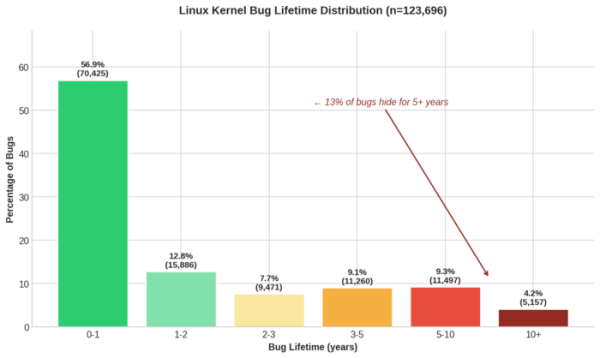
The results of a study on the time taken to detect and fix bugs in the Linux kernel have been published. The data was obtained from the analysis of 125,000 bugs marked in the Git repository with the tag 'Fixes:', referring to the commit where the bug originated. The average time to detect bugs in the kernel was 2.1 years. Considering only the bugs fixed in 2025, this figure was 2.8 years.
30% of bugs were fixed by the same developers who introduced them. 56.9% of bugs are eliminated within a year. 13.5% of bugs remained unnoticed for more than 5 years (for only those bugs fixed in 2025 — 19.4%). Due to the uneven distribution, the median age of a bug in the kernel code was 8 months for the sample from 2005, and 1 year for bugs fixed in 2025. The longest-existing bug in the code was a buffer overflow in ethtool, fixed after 20.7 years.
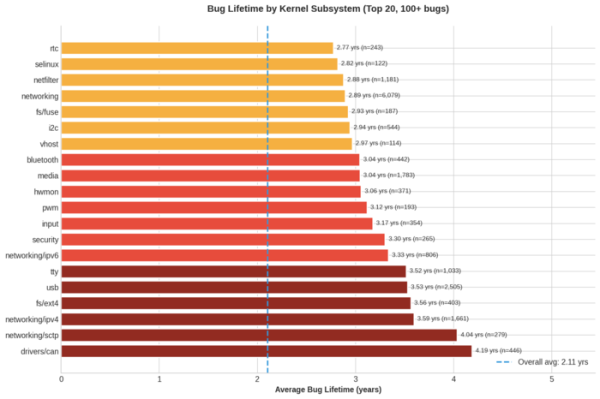
The dynamics of bug detection significantly differ from the average for some subsystems, for example, in the CAN bus driver and SCTP stack, problem detection on average takes about 4 years, in the IPv4 stack — 3.6 years, USB and TTY — 3.5, Netfilter and network stack — 2.9, VM — 1.8, GPU — 1.4, BPF — 1.1 years.
Detection time correlates with bug types: the average detection time for race condition-related bugs was 5.1 years, integer overflow — 3.9, use-after-free — 3.2, buffer overflow and memory leak — 3.1, reference counting — 2.8, null pointer dereference and deadlocks — 2.2 years.
The obtained statistics also show the impact of introducing new tools for automated bug detection, static analysis, and code testing, such as Syzkaller, KASAN, KMSAN, and KCSAN. For example, in 2010, no bug fixes were recorded within a year. While in 2014, 31% of bugs were identified within a year, in 2018 — 54%, and in 2022 — 69% of bugs.
The obtained statistics were used to create the VulnBERT machine learning model, which predicts the presence of vulnerabilities in commits. When tested on commits from 2024, the error detection accuracy was 92.2% with a false positive rate of 1.2% (for comparison, the previously available CodeBERT model identified 89.2% of issues with a false positive rate of 48.1%).
Source: opennet.ru
