

After a short break, we return to NSX. Today, I will show you how to configure NAT and Firewall.
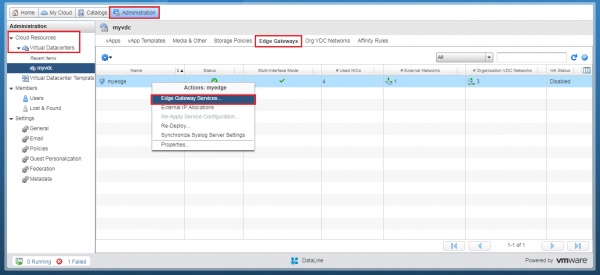
In the tab Administration go to your virtual data center – Cloud Resources – Virtual Datacenters.
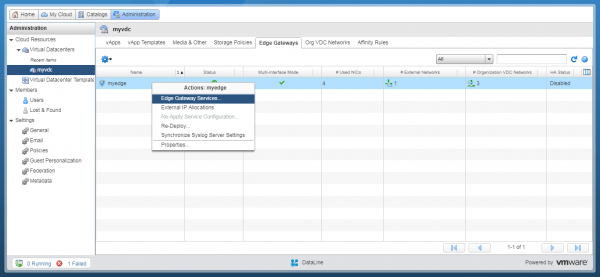
Select the tab Edge Gateways and right-click on the desired NSX Edge. From the context menu, select the option Edge Gateway Services. The NSX Edge control panel will open in a new tab.
Configuring Firewall rules
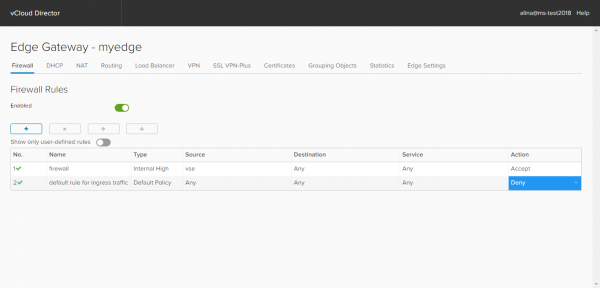
By default, in the item default rule for ingress traffic the Deny option is selected, meaning the Firewall will block all traffic.
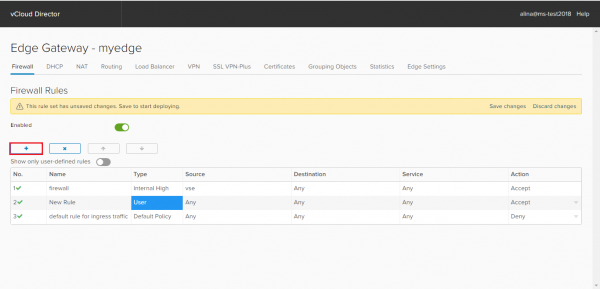
To add a new rule, click +. A new entry with the name New rule. Edit its fields according to your requirements.
In the field Name set a name for the rule, for example, Internet.
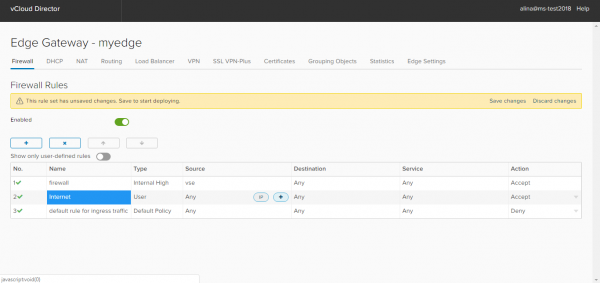
In the field Source enter the necessary source addresses. The IP button can be used to specify a single IP address, a range of IP addresses, or CIDR.
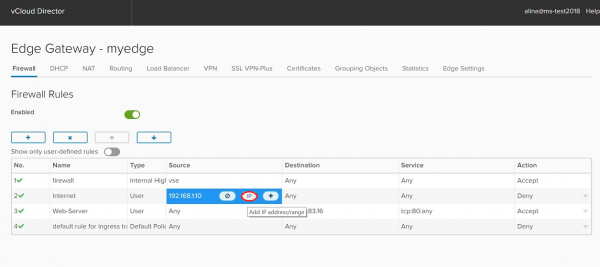
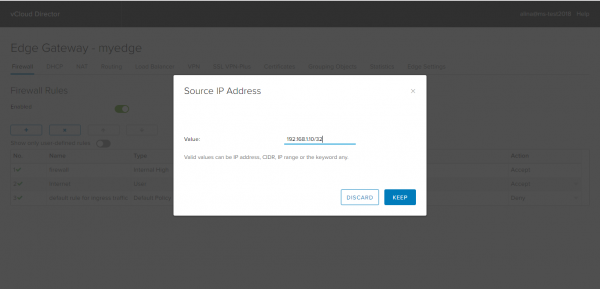
By clicking +, you can specify other objects:
- Gateway interfaces. All internal networks (Internal), all external networks (External), or Any.
- Virtual machines. We attach rules to a specific virtual machine.
- OrgVdcNetworks. Organization-level networks.
- IP Sets. A pre-created user group of IP addresses (created in Grouping object).
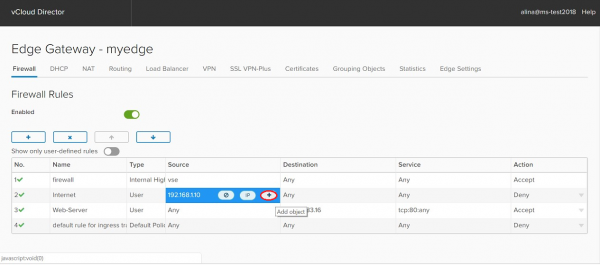
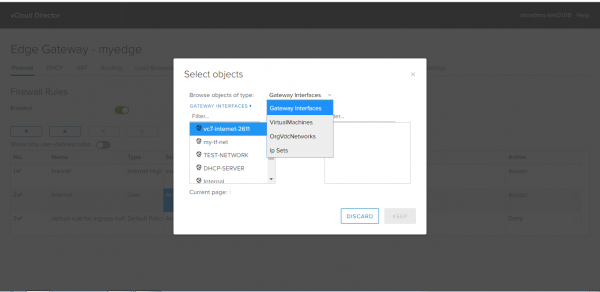
In the field Destination specify the destination address. The same options as in the Source field are available here.
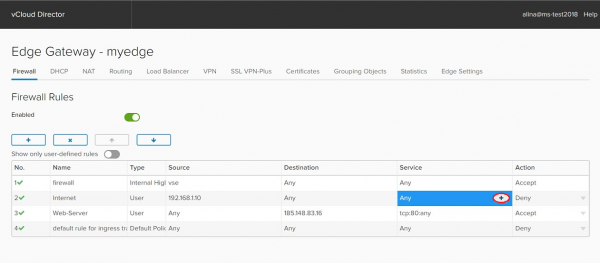
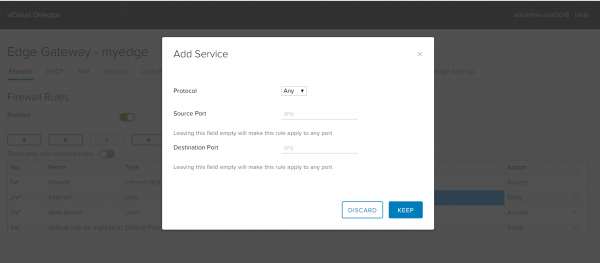
In the field Service you can select or manually specify the destination port (Destination Port), the required protocol (Protocol), and the source port (Source Port). Click Keep.
In the field Action select the necessary action: allow traffic that matches this rule or deny it.
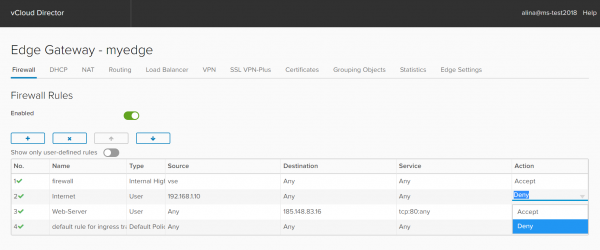
We apply the entered configuration by selecting Save changes.
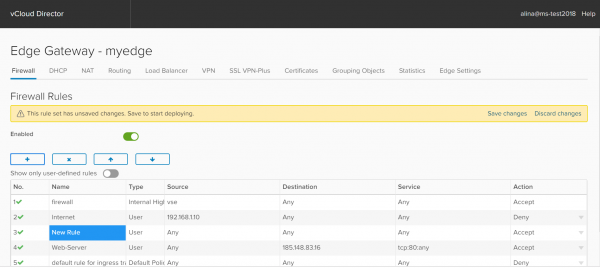
Rule Examples
Rule 1 for Firewall (Internet) allows access to the Internet for any protocols from the server with IP 192.168.1.10.
Rule 2 for Firewall (Web-server) allows access from the Internet using (TCP protocol, port 80) through your external address. In this case – 185.148.83.16:80.
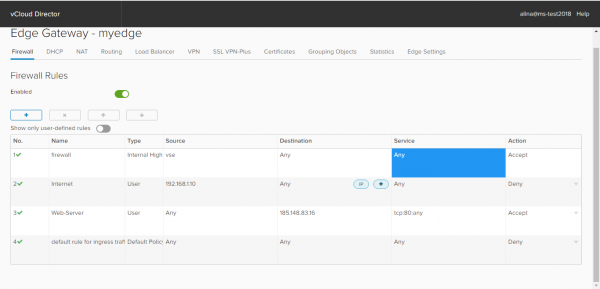
Configuring NAT
NAT (Network Address Translation) – translates private (gray) IP addresses to public (white) ones, and vice versa. Thanks to this process, a virtual machine gets Internet access. To configure this mechanism, you need to set up SNAT and DNAT rules.
Important! NAT only works when the Firewall is enabled and the appropriate allow rules are configured.
Creating an SNAT rule. SNAT (Source Network Address Translation) is a mechanism whose essence consists of replacing the source address when forwarding a packet.
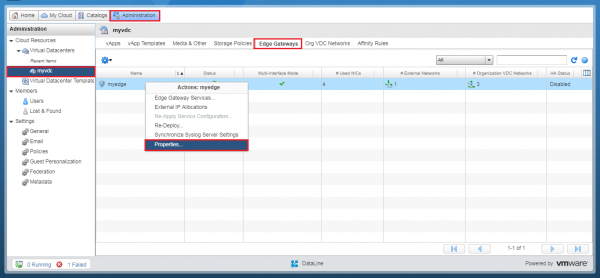
First, you need to find out the available external IP address or range of IP addresses. For this, go to the section Administration and double-click on the virtual data center. In the settings menu that appears, go to the tab Edge Gateways. Select the required NSX Edge and right-click on it. Choose the option Properties.
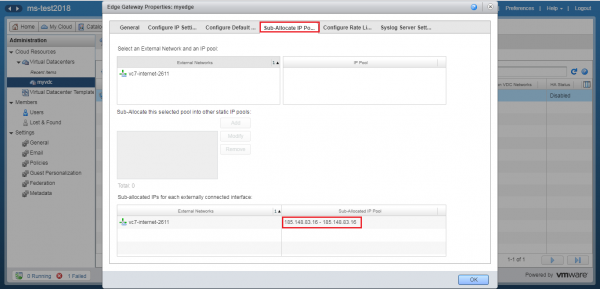
In the window that appears, under the tab Sub-Allocate IP Pools you can view the external IP address or range of IP addresses. Note it down or remember it.
Next, right-click on the NSX Edge. In the menu that appears, select the option Edge Gateway Services. And we are back in control panel NSX Edge.
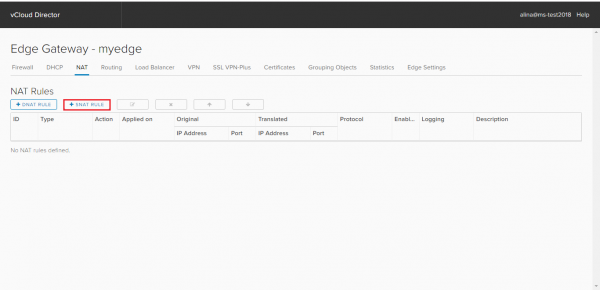
In the window that appears, open the NAT tab and click Add SNAT.
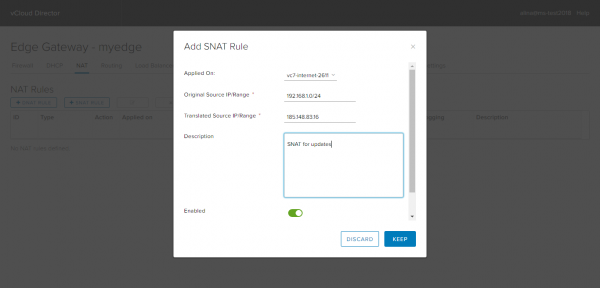
In the new window, specify:
- in the Applied on field – the external network (not the organization-level network!);
- Original Source IP/range – the internal range of addresses, for example, 192.168.1.0/24;
- Translated Source IP/range – the external address through which you will access the Internet, which you found in the Sub-Allocate IP Pools tab.
Click Keep.
Creating a DNAT rule. DNAT – a mechanism that changes the destination address of a packet as well as the destination port. It is used to redirect incoming packets from an external address/port to a private IP address/port within a private network.
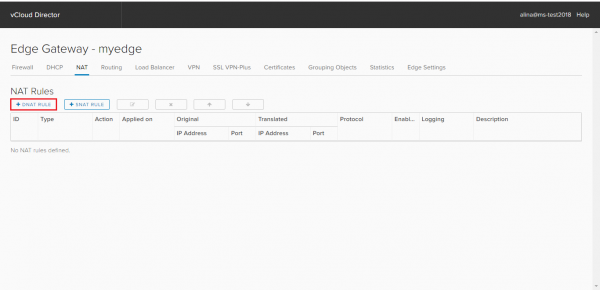
Select the NAT tab and click Add DNAT.
In the window that appears, specify:
— in the Applied on field – the external network (not the organization-level network!);
— Original IP/range – the external address (the address from the Sub-Allocate IP Pools tab);
— Protocol – the protocol;
— Original Port – the port for the external address;
— Translated IP/range – the internal IP address, for example, 192.168.1.10
— Translated Port – the port for the internal address, to which the port of the external address will be translated.
Click Keep.
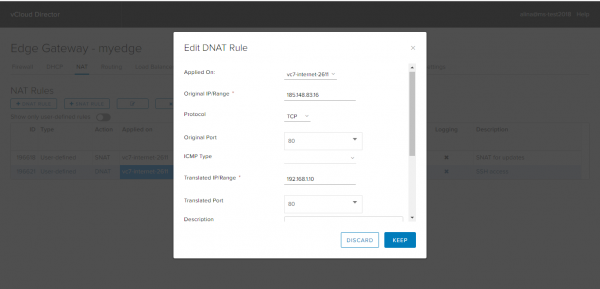
We apply the entered configuration by selecting Save changes.
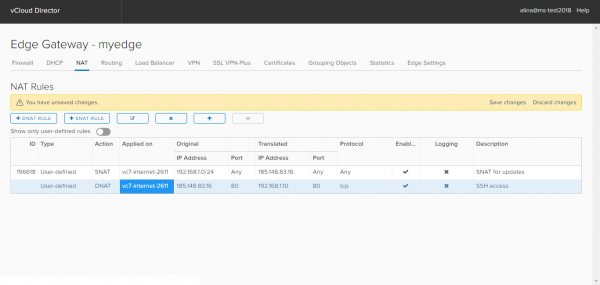
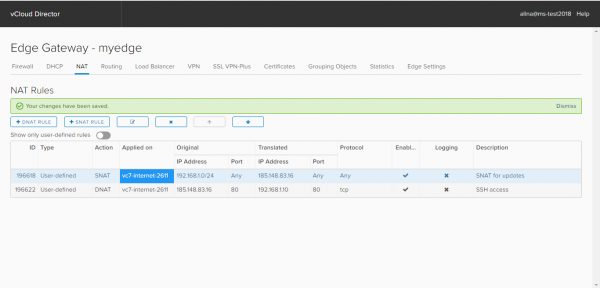
Done.
Next, we have the DHCP instructions, including setting up DHCP Bindings and Relay.
Source: habr.com
