

ESET reports that malicious applications have appeared in the Google Play store, aiming to access one-time passwords to bypass two-factor authentication.
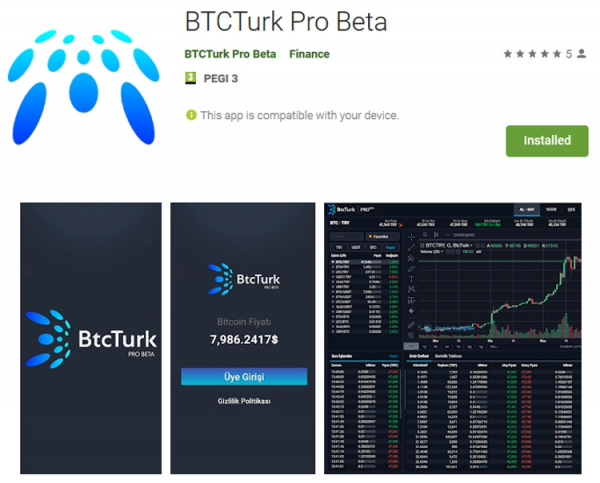
ESET specialists have determined that the malware is disguised as the legitimate cryptocurrency exchange BtcTurk. Specifically, malicious programs have been found under the names BTCTurk Pro Beta, BtcTurk Pro Beta, and BTCTURK PRO.
After downloading and installing one of these applications, the user is prompted to allow access to notifications. Next, a window appears for entering login credentials for the BtcTurk system.
Entering authentication details ends with the victim receiving an error message. Meanwhile, the provided information and pop-up notifications with the authentication code are sent to a remote server cybercriminals.
ESET notes that the discovery of malicious applications with such functions is the first known case since restrictions were imposed on Android applications accessing call logs and SMS.
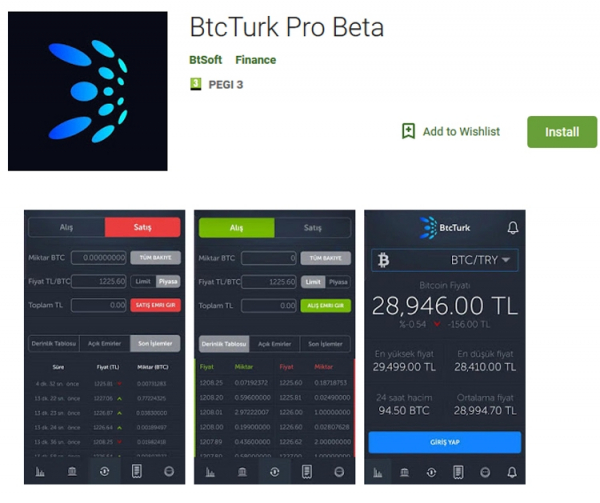
Fake cryptocurrency applications were uploaded to Google Play this month. Currently, the detected programs have been removed, but attackers may upload malicious applications with described functions under different names to Google Play.
Source: 3dnews.ru
