

In the LibreOffice office suite vulnerability (), which can be exploited to execute arbitrary code when opening documents crafted by an attacker.
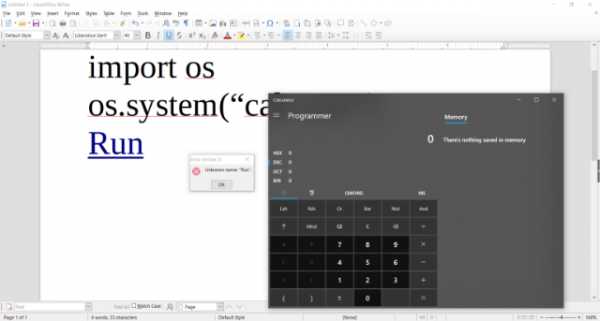
The vulnerability arises from the fact that the LibreLogo component, intended for teaching programming and inserting vector graphics, translates its operations into Python code. By executing LibreLogo instructions, an attacker can run any Python code in the context of the user's current session, leveraging the 'run' command provided in LibreLogo. From Python, any arbitrary system commands can be invoked using the system() function.
LibreLogo is an optional component, but LibreOffice by default offers macros that allow calling LibreLogo without requiring confirmation for operation execution and do not display warnings even when the macro security mode is set to maximum (selecting 'Very High' level).
To execute an attack, such a macro can be tied to an event handler that is triggered when, for example, the mouse cursor hovers over a specific area or when the input focus on the document is activated (onFocus event). As a result, opening a document prepared by an attacker may lead to the hidden execution of Python code, unnoticed by the user. For instance, in the demonstrated exploit example, the system calculator starts without any warning when the document is opened.
The vulnerability was quietly patched in the LibreOffice 6.2.5 update released on July 1, but it turns out the issue was not fully resolved (only the call to LibreLogo from macros was blocked) and Moreover, the problem is not fixed in the 6.1.6 release recommended for corporate users. A complete fix for the vulnerability is planned for the upcoming LibreOffice 6.3 release, expected next week. Until a full update is released, users are advised to explicitly disable the LibreLogo component, which is by default available in many distributions. The vulnerability has been partially mitigated in , , and .
Source: opennet.ru
