

Siemens Company release of the open hypervisor . The hypervisor supports operation on x86_64 systems with VMX+EPT or SVM+NPT (AMD-V) extensions, as well as on ARMv7 and ARMv8/ARM64 processors with virtualization extensions. Separately image generator for the Jailhouse hypervisor, created based on Debian packages for supported devices. The project code is licensed under GPLv2.
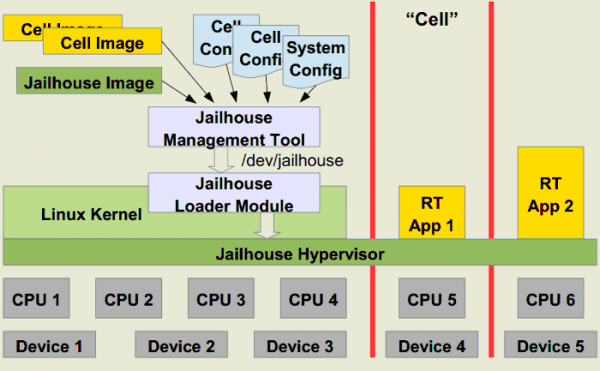
is implemented as a module for the Linux kernel, providing virtualization at the kernel level. Components for guest systems are already included in the main Linux kernel. Hardware virtualization mechanisms provided by modern CPUs are used to manage isolation. The distinctive features of Jailhouse are its lightweight implementation and focus on binding virtual machines to a fixed CPU, memory areas, and hardware devices. This approach allows multiple independent virtual environments to operate on a single physical multi-core server, each tied to its own CPU core.
With strict binding to the CPU, the overhead from the hypervisor's operation is minimized and its implementation is greatly simplified since there's no need for a complex resource allocation scheduler — dedicating a CPU core guarantees that no other tasks will run on that CPU. The advantage of this approach is the ability to ensure guaranteed access to resources and predictable performance, making Jailhouse a suitable solution for creating tasks that require real-time operations. The downside is limited scalability, constrained by the number of CPU cores.
In Jailhouse terminology, virtual environments are referred to as 'cells'. Inside a cell, the system appears as a single-processor server, showing performance to that of a dedicated CPU core. An environment of any operating system can run in a cell, as well as stripped-down environments for running a single application or specially prepared separate applications for real-time tasks. The configuration is specified in , defining the allocated environment CPU, memory regions, and input/output ports.
In the new release,
- Support has been added for Raspberry Pi 4 Model B and Texas Instruments J721E-EVM platforms.
- the ivshmem device, used to facilitate interaction between cells. A transport for VIRTIO can be implemented on top of the new ivshmem.
- The ability to disable the creation of large memory pages (hugepage) to block vulnerabilities has been implemented. in Intel processors, which allows an unprivileged attacker to initiate a denial of service, causing the system to hang in a 'Machine Check Error' state.
- Support for SMMUv3 (System Memory Management Unit) and TI PVU (Peripheral Virtualization Unit) has been implemented for systems with ARM64 processors. PCI support has been added for isolated environments running on bare metal.
- On x86 systems, for root chambers, the provided CR4.UMIP (User-Mode Instruction Prevention) mode from Intel processors has been enabled, allowing the prohibition of executing certain instructions in user space, such as SGDT, SLDT, SIDT, SMSW, and STR, which can be used in attacks aimed at privilege escalation in the system.
Source: opennet.ru
