

At the end of 2019, several Russian entrepreneurs approached the Group-IB cybercrime investigations department, encountering a problem of unauthorized access by unknown individuals to their correspondence in the Telegram messenger. The incidents occurred on both iOS and Android devices, regardless of which federal mobile operator the victim was using.
The attack began with the user receiving a message in the Telegram messenger from the Telegram service channel (this is the official channel of the messenger with the blue verification tick) containing a confirmation code that the user did not request. Following this, an SMS with the activation code arrived on the victim's smartphone — and almost immediately, a notification was sent to the Telegram service channel indicating that the account had been logged in from a new device.
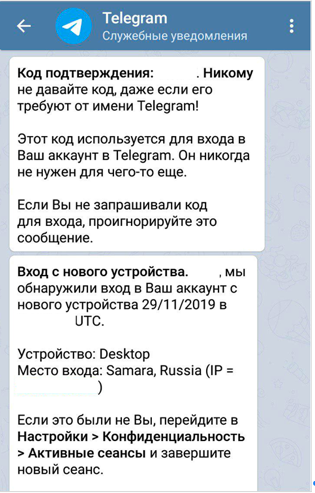
In all cases known to Group-IB, the attackers accessed чужой аккаунт through mobile internet (presumably using disposable SIM cards), and in most instances, the IP address of the attackers was located in Samara.
Access by request
An investigation by the Group-IB Computer Forensics Lab, which received the victims' electronic devices, showed that the devices were not infected with spyware or banking trojans, accounts were not hacked, and there was no SIM card swapping. In all cases, the attackers gained access to the victim's messenger using SMS codes received when logging into the account from a new device.
This procedure works as follows: when activating the messenger on a new device, Telegram sends a code via the service channel to all of the user's devices, and then (upon request) an SMS notification is sent to the phone. Knowing this, the attackers themselves initiate a request for the messenger to send an SMS with the activation code, intercept this SMS, and use the obtained code to successfully log in to the messenger.
Thus, attackers gain unauthorized access to all current chats except for secret ones, as well as to the message history in these chats, including files and photos that were shared. Upon discovering this, a legitimate Telegram user can forcibly terminate the attacker's session. Thanks to the implemented protection mechanism, the reverse cannot happen; the attacker cannot terminate older sessions of the actual user within 24 hours. Therefore, it is important to quickly identify an unauthorized session and end it to avoid losing access to the account. Group-IB specialists have notified the Telegram team about their research on the situation.
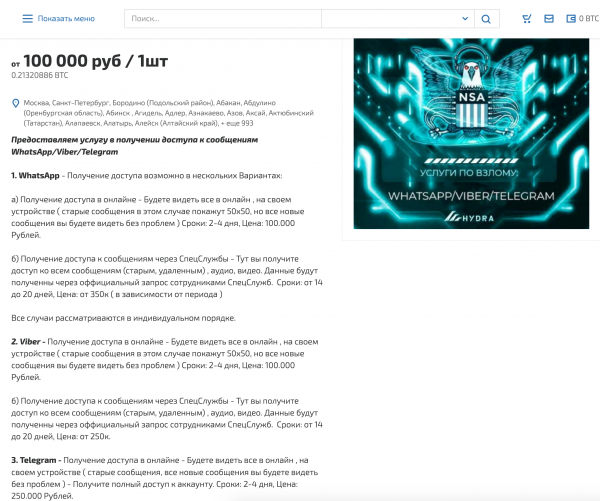
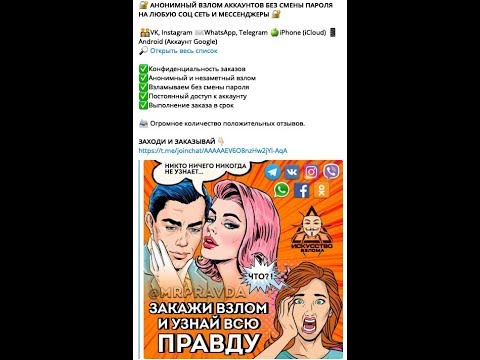
The investigation of the incidents continues, and at this moment it is not precisely established which scheme was used to bypass the SMS factor. Researchers have provided examples of intercepting SMS messages through attacks on the SS7 or Diameter protocols used in mobile networks at different times. Theoretically, such attacks can be carried out using illegal special technical means or insider access within mobile operators. In particular, there are recent listings on hacker forums in the Darknet offering hacking various messengers, including Telegram.
Experts in different countries, including Russia, have repeatedly stated that social networks, mobile banking, and messengers can be hacked using a vulnerability in the SS7 protocol. However, these were isolated cases of targeted attacks or experimental studies, says Sergey Lupanin, head of the cybercrime investigations department at Group-IB. In a series of new incidents, of which there are already more than 10, it is evident that attackers aim to turn this method of earning into a routine. To prevent this from happening, it is necessary to enhance one’s own level of digital hygiene: at a minimum, use two-factor authentication wherever possible and add a mandatory second factor to SMS, which is functionally included in Telegram.
How to protect yourself?
1. Telegram has already implemented all the necessary cybersecurity options that will nullify the efforts of attackers.
2. On iOS and Android devices for Telegram, you need to go to the Telegram settings, select the 'Privacy' tab, and set up the 'Cloud Password Two-step Verification' or 'Two-step verification'. A detailed description of how to enable this option is provided in the instructions on the official messenger website: (https://telegram.org/blog/sessions-and-2-step-verification)
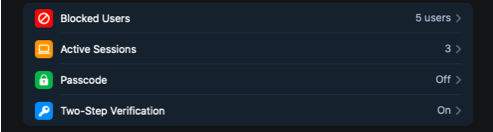
3. It is important not to set an email address for recovering this password, as password recovery for the email usually also happens via SMS. Similarly, you can enhance the security of your account in WhatsApp.
Source: habr.com
