

Positive Technologies Company announces the release of a new version of the MaxPatrol SIEM software suite 5.1, designed for monitoring information security events and identifying various incidents in real time.
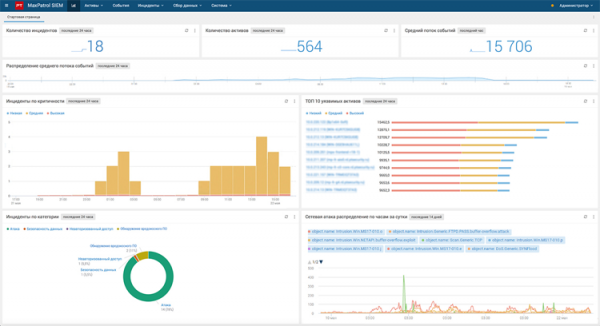
The MaxPatrol SIEM platform collects data on current events and automatically detects threats, including previously unknown ones. The system helps information security services to respond promptly to an attack, conduct a detailed investigation, and prevent reputational and financial damage to the organization.
In MaxPatrol SIEM version 5.1, a transition to a new Elasticsearch database architecture has been made, which, according to the developers, allowed for a more than one-third increase in product performance.
Another innovation of the software suite is a flexible user role management model. Previously, the system allowed for the assignment of two roles—'Administrator' or 'Operator'; now IT administrators can create additional roles, granting or restricting access to certain sections of the product.
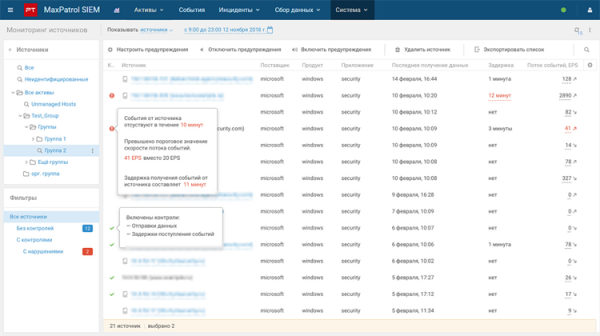
Among other product features are enhanced attack detection capabilities, an improved user interface, and additional analytics and information security event processing tools.
Detailed information about the MaxPatrol SIEM system is available for review on the website .
Source: 3dnews.ru
