

The antivirus solutions developer 'Doctor Web' about the discovery of a dangerous backdoor being distributed by attackers disguised as an update for the popular Google Chrome browser. It is reported that over 2,000 people have already fallen victim to cybercriminals, and the number continues to rise.
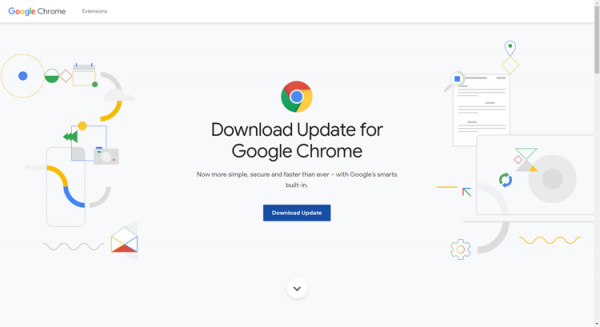
According to the virus laboratory 'Doctor Web', to maximize audience reach, the attackers have used resources based on the WordPress CMS — from news blogs to corporate portals, to which hackers managed to gain administrative access. A JavaScript script is embedded in the code of the pages of the compromised sites that redirects users to a phishing site disguised as the official Google company website (see screenshot above).
With the help of the backdoor, attackers gain the ability to deliver 'useful' payloads in the form of malicious applications to infected devices. Among them are: the X-Key Keylogger, the Predator The Thief stealer, and a trojan for remote control via the RDP protocol.
To avoid unpleasant incidents, specialists from 'Doctor Web' recommend being extremely cautious while working on the Internet and advise not to overlook the phishing resource filter provided in many modern browsers.
Source: 3dnews.ru
