

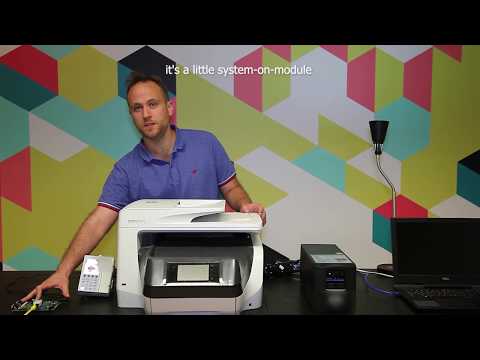
In the proprietary TCP/IP stack , exploited through the sending of specially crafted packets. The vulnerabilities are codenamed . Some vulnerabilities are also found in the KASAGO TCP/IP stack by Zuken Elmic (Elmic Systems), which has common roots with Treck. The Treck stack is used in many industrial, medical, communication, embedded, and consumer devices (from smart bulbs to printers and uninterruptible power supplies), as well as in energy, transportation, aerospace, commercial, and oil extraction equipment.
Among the notable target devices that utilize the Treck TCP/IP stack are HP network printers and Intel chips. Issues in the Treck TCP/IP stack have also led to recent in Intel AMT and ISM subsystems, exploited through the sending of network packets. The presence of vulnerabilities has been confirmed by manufacturers Intel, HP, Hewlett Packard Enterprise, Baxter, Caterpillar, Digi, Rockwell Automation, and Schneider Electric. Additionally,
, whose products utilize the Treck TCP/IP stack, have not yet responded to the issues. Five manufacturers, including AMD, stated that their products are not affected by the problems.
Problems have been found in the implementation of protocols IPv4, IPv6, UDP, DNS, DHCP, TCP, ICMPv4, and ARP, caused by improper handling of parameters with data sizes (using a size field without checking the actual data size), input validation errors, double free memory issues, reading out of buffer bounds, integer overflows, improper access control, and problems with processing null-terminated strings.
The two most critical issues (CVE-2020-11896, CVE-2020-11897) with a CVSS level of 10 allow code execution on the device through the sending of specially crafted IPv4/UDP or IPv6 packets. The first critical issue manifests on devices supporting IPv4 tunnels, while the second appears in versions supporting IPv6 released before 06/04/2009. Another critical vulnerability (CVSS 9) exists in the DNS resolver (CVE-2020-11901) and allows code execution through the sending of a specially crafted DNS request (this issue was used to demonstrate the breach of Schneider Electric APC UPS and is present on devices supporting DNS).
Other vulnerabilities CVE-2020-11898, CVE-2020-11899, CVE-2020-11902, CVE-2020-11903, CVE-2020-11905 allow for the exposure of system memory content through specially crafted packets including IPv4/ICMPv4, IPv6OverIPv4, DHCP, and DHCPv6. Other issues may lead to denial of service or leakage of residual data from system buffers.
Most vulnerabilities have been addressed in the release of Treck 6.0.1.67 (issue CVE-2020-11897 fixed in 5.0.1.35, CVE-2020-11900 in 6.0.1.41, CVE-2020-11903 in 6.0.1.28, CVE-2020-11908 in 4.7.1.27). Since preparing firmware updates for specific devices may take time or be impossible (the Treck stack has been in use for over 20 years, many devices are no longer supported or are difficult to update), administrators are advised to isolate affected devices and configure packet inspection systems, firewalls, or routers to normalize or block fragmented packets, block IP tunnels (IPv6-in-IPv4 and IP-in-IP), block source routing, enable inspection of invalid options in TCP packets, block unused ICMP control messages (MTU Update and Address Mask), prohibit IPv6 multicast, and redirect DNS queries to a secure recursive DNS server.
Source: opennet.ru
