

At Google, we believe that cloud computing will increasingly move towards private, encrypted services that ensure users have complete confidence in data confidentiality.
Google Cloud already encrypts customer data in transit and at rest, but it still needs to be decrypted for processing. Confidential computing is a revolutionary technology used to encrypt data during processing. Environments based on confidential computing allow encrypted data to be stored in memory and other locations outside the CPU.
Confidential VMs are currently in beta testing and are the first product in the Google Cloud Confidential Computing lineup. We are already implementing various methods of isolation and sandboxing in our cloud infrastructure to ensure the security of a multi-tenant architecture. Confidential VMs take security to the next level by offering memory encryption for additional isolation of their workloads in the cloud, helping our clients protect sensitive data. We believe this will particularly interest those operating in regulated industries (such as GDPR and other related matters. translator's note).
Opening New Opportunities
With Asylo, the open-source platform for confidential computing, we focused on simplifying the deployment and use of confidential computing environments, offering high performance and applications for any workload you choose to run in the cloud. We believe you shouldn't have to compromise on usability, flexibility, performance, and security.
With the transition of Confidential VMs to beta, we have become the first major cloud service provider to offer such a level of security and isolation — providing customers with a straightforward and easy-to-use option for both new applications and 'ported' applications (aiming to run in the cloud without significant modifications. translator's note). We ensure:
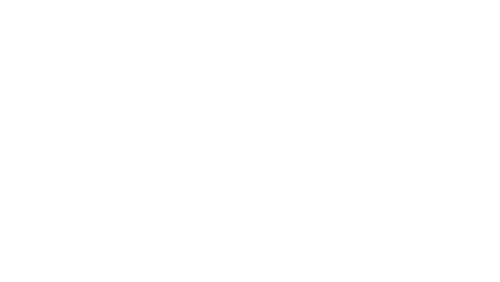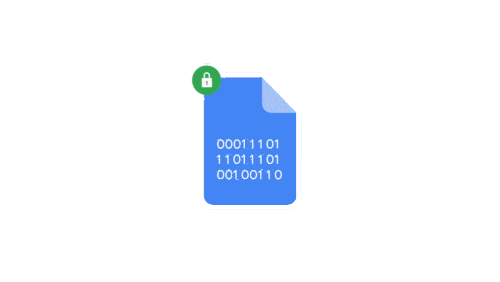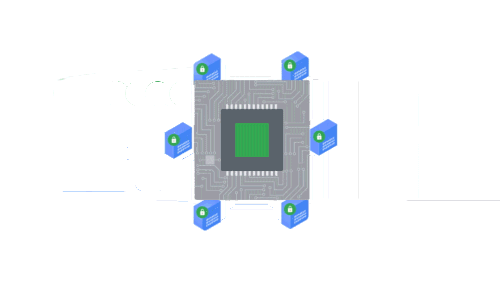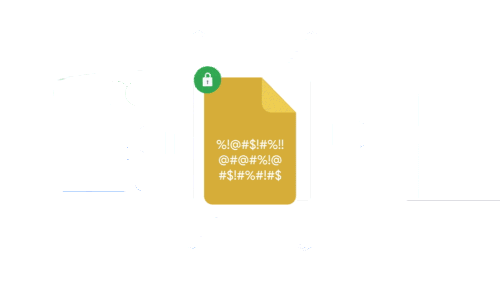
Unmatched confidentiality: clients can protect the privacy of their sensitive data in the cloud even during processing. Confidential VMs use the Secure Encrypted Virtualization (SEV) feature of the second generation AMD EPYC processors. Your data remains encrypted during use, indexing, querying, and training. Encryption keys are generated in hardware separately for each virtual machine and never leave the hardware.
Enhanced innovations: confidential computing can open processing scenarios that were previously impossible. Companies can now share sets of sensitive data and collaborate on research in the cloud while maintaining confidentiality.
Confidentiality for 'ported' workloads: our goal is to simplify confidential computing. Transitioning to Confidential VMs is seamless—all workloads in GCP running in virtual machines can switch to Confidential VMs. It's easy—just check one box.
Protection against advanced threats: confidential computing builds on the Shielded VMs protection against rootkits and bootkits, helping to ensure the integrity of the operating system selected to run in a Confidential VM.
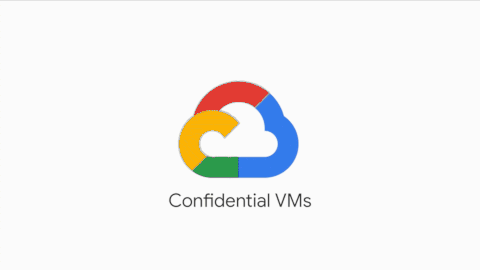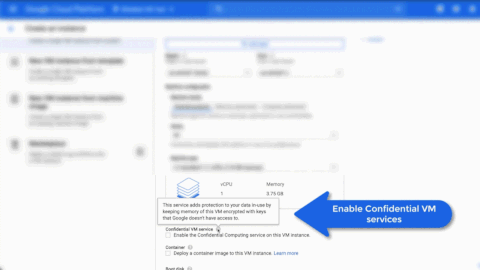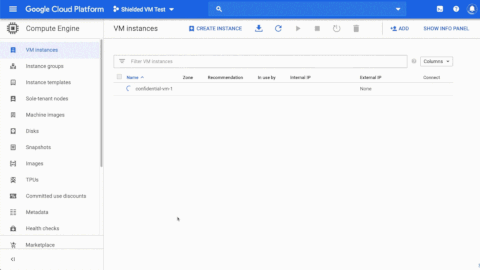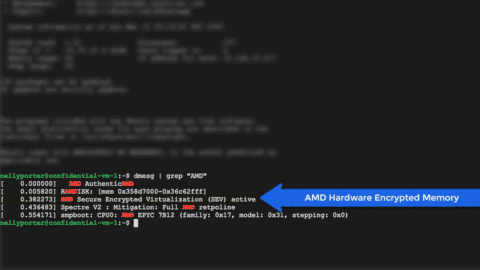
Basics of Confidential VMs
Confidential VMs operate on N2D virtual machines that run on second-generation AMD EPYC processors. With AMD SEV, high performance is ensured for most demanding computing tasks while keeping the virtual machine's memory encrypted with a unique key created and managed by the EPYC processor for each virtual machine. Keys are created by the AMD Secure Processor upon the virtual machine's creation and exist solely within it, making them inaccessible to both Google and other virtual machines operating on the same node.
In addition to built-in hardware encryption of memory, we create Confidential VMs on top of Shielded VMs to ensure resilience against OS image tampering, firmware integrity checks, and kernel and driver binary integrity. Google's offered images include Ubuntu 18.04, Ubuntu 20.04, Container Optimized OS (COS v81), and RHEL 8.2. We are working on CentOS, Debian, and others to offer additional operating system images.
We also work closely with the AMD Cloud Solutions engineering team to ensure that memory encryption of virtual machines does not impact performance. We have added support for new OSS drivers (nvme and gvnic) to handle storage subsystem requests and network traffic with higher bandwidth than older protocols. This has ensured that the performance metrics of Confidential VMs are close to those of standard virtual machines.
Thanks to Secure Encrypted Virtualization, built into the second generation of AMD EPYC processors, an innovative hardware security feature is provided to protect data in a virtualized environment. To support the new GCE Confidential VMs N2D, we collaborated with Google to help customers safeguard their data and ensure the performance of their workloads. We are excited to see that Confidential VMs show the same level of high performance for various workloads as the standard N2D virtual machines.
Raghu Nambiar, Vice President, Data Center Ecosystem, AMD
A game-changing technology
Confidential computing can help transform the way enterprises process data in the cloud while maintaining confidentiality and security. Additionally, among other advantages, companies will be able to collaborate without compromising the secrecy of data sets. Such collaboration, in turn, could lead to the development of even more transformative technologies and ideas; for instance, imagine the rapid development of vaccines and treatments for diseases resulting from such secure collaboration.
We can’t wait to see the opportunities that this technology opens up for your company. See , to learn more.
P.S. Not for the first time, and hopefully not the last, Google is rolling out technology that changes the world. Just as it was with Kubernetes not long ago. We are doing our part to support and spread Google technologies — training IT professionals in Russia. Our company is one of 3 Kubernetes Certified Service Providers and the only Kubernetes Training Partner in Russia. Therefore, we conduct intensive Kubernetes training sessions every spring and autumn. The next sessions will be held from September 28-30 and October 14-16. .
Source: habr.com
