

A vulnerability (CVE-2021-27365) has been discovered in the iSCSI subsystem code of the Linux kernel that allows an unprivileged local user to execute code at the kernel level and gain root privileges in the system. A working exploit prototype is available for testing. The vulnerability has been fixed in Linux kernel updates 5.11.4, 5.10.21, 5.4.103, 4.19.179, 4.14.224, 4.9.260, and 4.4.260. Kernel package updates are available in the Debian, Ubuntu, SUSE/openSUSE, Arch Linux, and Fedora distributions. Fixes have not yet been released for RHEL.
The issue is caused by an error in the iscsi_host_get_param() function of the libiscsi module, introduced back in 2006 during the development of the iSCSI subsystem. Due to insufficient size checks, some iSCSI string attributes, such as hostname or username, may exceed the PAGE_SIZE (4 KB). The vulnerability can be exploited by an unprivileged user sending Netlink messages that set iSCSI attributes to values exceeding PAGE_SIZE. When reading these attribute data through sysfs or seqfs, code is invoked that passes the attributes to the sprintf function for copying into a buffer of size PAGE_SIZE.
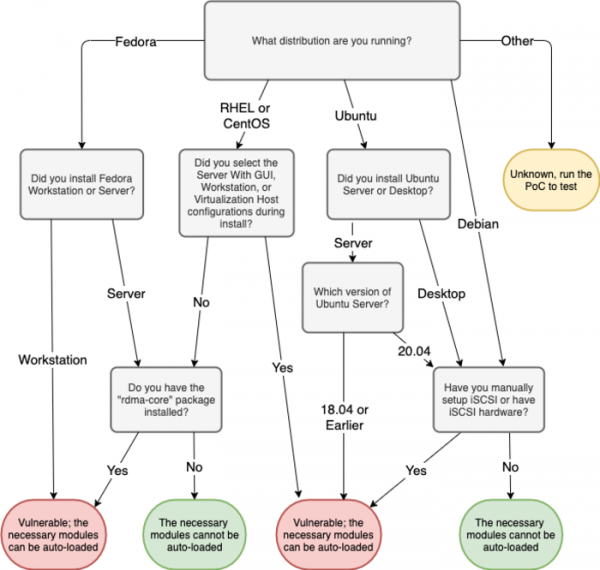
Exploitation of the vulnerability in distributions depends on the support for auto-loading the scsi_transport_iscsi kernel module when attempting to create a NETLINK_ISCSI socket. In distributions where this module loads automatically, the attack can be carried out regardless of the use of iSCSI functionality. For a successful exploit, registration of at least one iSCSI transport is also required. The ib_iser kernel module, which loads automatically when an unprivileged user attempts to create a NETLINK_RDMA socket, can be used for transport registration.
Automatic loading of the necessary exploit modules is supported in CentOS 8, RHEL 8, and Fedora when the rdma-core package, which is a dependency for some popular packages and is installed by default in configurations for workstations, server systems with a GUI, and virtualization host environments, is installed. However, rdma-core is not installed when using the server build that operates solely in console mode or when installing a minimal installation image. For example, the package is included in the base distribution of Fedora 31 Workstation but is not included in Fedora 31 Server. Debian and Ubuntu are less prone to this issue since the rdma-core package loads the necessary kernel modules for the attack only when RDMA hardware is present.
As a workaround for protection, you can disable the automatic loading of the libiscsi module: echo "install libiscsi /bin/true" >> /etc/modprobe.d/disable-libiscsi.conf
Additionally, two less severe vulnerabilities have been addressed in the iSCSI subsystem that could lead to data leakage from the kernel: CVE-2021-27363 (leak of transport descriptor information for iSCSI through sysfs) and CVE-2021-27364 (reading outside the buffer boundaries). These vulnerabilities could be exploited to interact via a netlink socket with the iSCSI subsystem without the necessary privileges. For instance, an unprivileged user could connect to iSCSI and send the "end a session" command to terminate a session.
Source: opennet.ru
