

Welcome! You have arrived at the seventh lesson of the course. . On We have learned about security profiles such as Web Filtering, Application Control, and HTTPS Inspection. In this lesson, we will continue our exploration of security profiles. First, we will familiarize ourselves with the theoretical aspects of antivirus and intrusion prevention systems, followed by a practical examination of how these security profiles operate.
Let's start with antivirus. First, we will discuss the technologies that FortiGate uses to detect viruses:
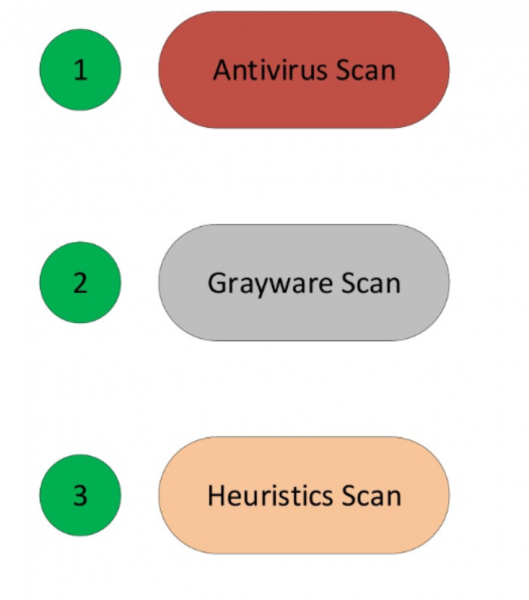
Antivirus scanning is the simplest and fastest method for detecting viruses. It identifies viruses that exactly match the signatures contained in the antivirus database.
Grayware Scan, or unwanted software scanning, utilizes this technology to identify unwanted programs that are installed without the user's knowledge or consent. Technically, these programs are not viruses. They often come bundled with other software and negatively affect the system upon installation, which is why they are classified as malicious. Such programs can often be detected using simple grayware signatures from the FortiGuard research database.
Heuristic scanning is based on probabilities, which can result in false positive effects. However, it can also detect zero-day viruses. Zero-day viruses are new viruses that have not been researched yet, and there are no existing signatures that could identify them. Heuristic scanning is not enabled by default and must be activated in the command line.
If all antivirus options are enabled, FortiGate applies them in the following order: antivirus scanning, grayware scanning, heuristic scanning.
FortiGate can utilize multiple antivirus databases depending on the tasks at hand:
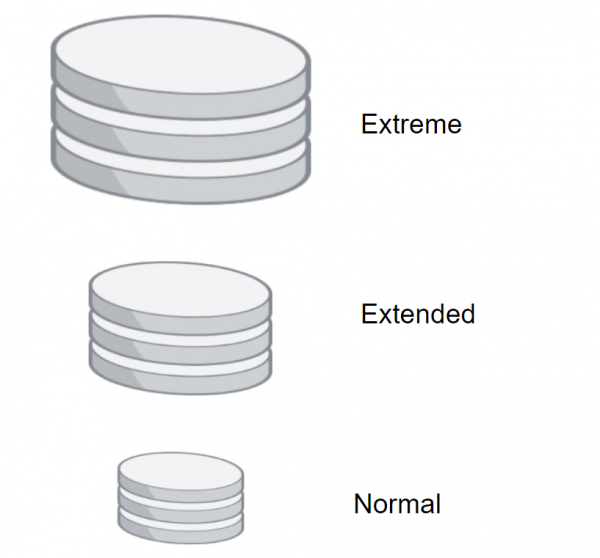
- Normal antivirus database is included in all FortiGate models. It contains signatures for viruses that have been identified in recent months. This is the smallest antivirus database, so scanning is performed the fastest when using it. However, this database cannot detect all known viruses.
- The Extended (Extend) database is supported by most FortiGate models. It helps detect viruses that are no longer active. Many platforms remain vulnerable to these viruses. Additionally, these viruses could cause issues in the future.
- The last, extreme database (Extreme) is used in infrastructures where a high level of security is required. It helps detect all known viruses, including those targeted at outdated operating systems that are currently not widely used. This type of signature database is also not supported by all FortiGate models.
There is also a compact signature database designed for quick scanning. We will discuss this a bit later.
Antivirus databases can be updated in various ways.
The first method, Push Update, allows databases to be updated as soon as the FortiGuard research database releases an update. This is useful for infrastructures that require a high level of security because FortiGate will receive urgent updates immediately after they are released.
The second method is to set a schedule. This way, updates can be checked every hour, day, or week. Thus, the time frame is set at your discretion.
These methods can be used together.
However, it is important to note that in order for updates to be performed, the antivirus profile must be enabled on at least one firewall policy. Otherwise, updates will not occur.
Updates can also be downloaded from the Fortinet support site, and then manually uploaded to FortiGate.
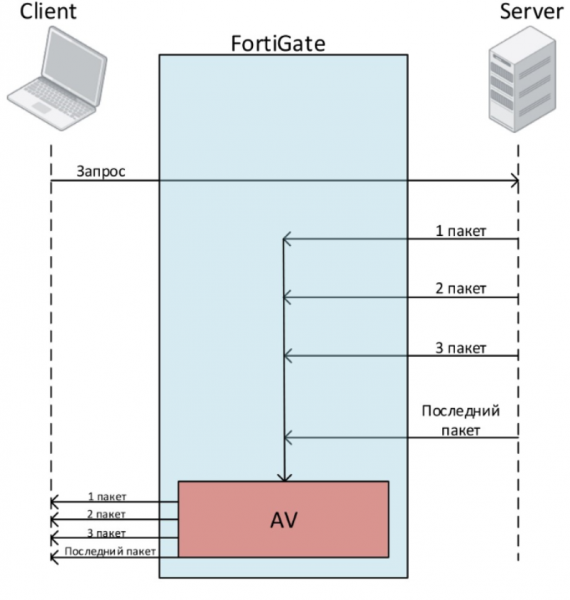
Let's consider the scanning modes. There are three in total — Full Mode in Flow Based mode, Quick Mode in Flow Based mode, and Full Mode in proxy mode. Let's start with Full Mode in Flow mode.
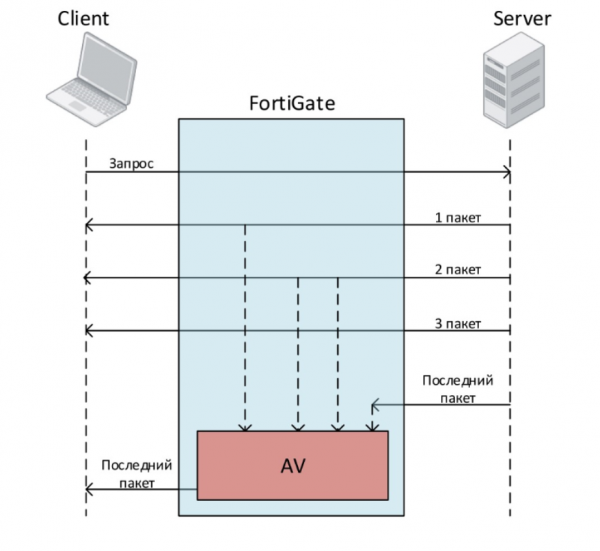
Suppose a user wants to download a file. They send a request. The server begins to send them the packets that make up the file. The user immediately receives these packets. But before sending these packets to the user, FortiGate caches them. Once FortiGate receives the last packet, it starts scanning the file. At this time, the last packet is queued and not sent to the user. If the file contains no viruses, the last packet is sent to the user. If a virus is detected, FortiGate breaks the connection with the user.
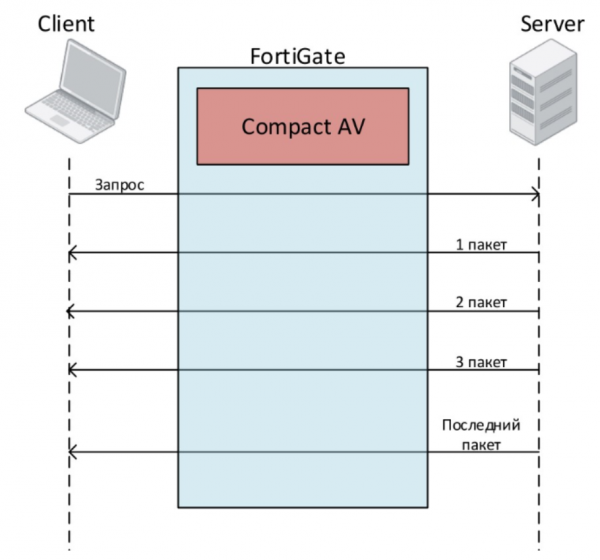
The second scanning mode available in Flow Based is Quick Mode. It uses a compact signature database that contains fewer signatures than a standard database. It also has some limitations compared to Full Mode:
- It cannot send files to the sandbox
- It cannot use heuristic analysis
- It also cannot utilize packets associated with mobile malware
- Some entry-level models do not support this mode.
Quick mode also checks traffic for viruses, worms, trojans, and malware, but without buffering. This provides better performance, but at the same time, the likelihood of detecting a virus decreases.
In Proxy mode, there is only one scanning mode available — Full Mode. In this mode, FortiGate first saves the entire file locally (as long as the allowable file size for scanning is not exceeded). The client must wait until the scanning is completed. If a virus is detected during scanning, the user is notified immediately. Since FortiGate saves the entire file first and then scans it, this can take quite a long time. As a result, the client may terminate the connection before receiving the file due to a prolonged delay.
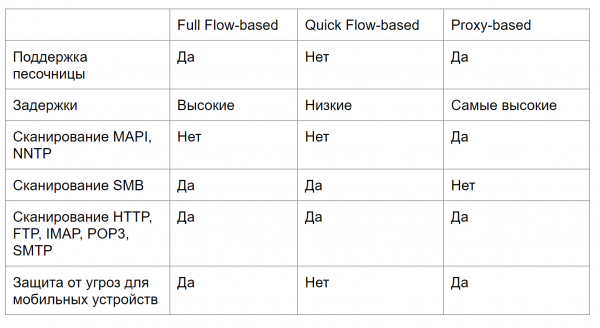
The table below provides a comparative overview of the scanning modes — it will help you determine which type of scanning is suitable for your tasks. The setup and operational verification of the antivirus are discussed practically in the video at the end of the article.
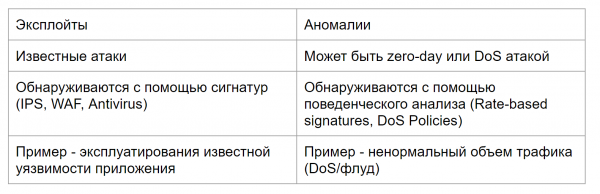
Let's move on to the second part of the lesson — the intrusion prevention system. However, to begin studying IPS, it is essential to differentiate exploits from anomalies and understand the mechanisms used by FortiGate to protect against them.
Exploits are known attacks with specific patterns that can be detected using IPS, WAF, or antivirus signatures.
Anomalies are unusual behavior in the network, such as an unusually large volume of traffic or higher than normal CPU consumption. Anomalies need to be monitored since they can indicate a new, yet unexplored attack. Anomalies are typically detected using behavioral analysis — known as rate-based signatures and DoS policies.
Ultimately, the IPS on FortiGate utilizes signature databases to detect known attacks and rate-based signatures and DoS policies to identify various anomalies.
By default, the initial set of IPS signatures is included in every version of the FortiGate operating system. Through updates, FortiGate receives new signatures, ensuring that IPS remains effective against new exploits. The FortiGuard service updates IPS signatures quite frequently.
An important point that applies to both IPS and antivirus is that if your licenses have expired, you can still use the most recently obtained signatures. However, you will not be able to obtain new ones without licenses. Therefore, the absence of licenses is extremely undesirable — when new attacks emerge, you cannot defend yourself with old signatures.
The IPS signature databases are divided into standard and extended. The standard database contains signatures for common attacks that rarely, if ever, trigger false positives. The preconfigured action for most of these signatures is to block.
The extended database contains additional attack signatures that significantly impact system performance or that cannot be blocked due to their specific nature. Due to the size of this database, it is unavailable for FortiGate models with limited disk space or RAM. However, for highly secure environments, the use of the extended database may be necessary.
The configuration and verification of IPS functionality are also covered in the video below.
In the next lesson, we will explore working with users. To ensure you don't miss it, follow updates on the following channels:
Source: habr.com
