

We continue the series of articles on working with the new SMB CheckPoint product line, reminding that in we described the characteristics and capabilities of the new models, management and administration methods. Today we will look at the deployment scenario of the high-end model in the series: CheckPoint 1590 NGFW. Here’s a brief overview of this part:
- Unpacking the equipment (description of components, physical and network connection).
- Initial device setup.
- Initial configuration.
- Functionality assessment.
Unpacking the equipment
Familiarization with the equipment begins with unpacking it from the box, disassembling the components, and installing parts. Click on the spoiler where the process is briefly presented.
NGFW 1590 delivery
Briefly about the components:
- NGFW 1590;
- Power adapter;
- 2 Wi-Fi antennas (2.4 GHz and 5 GHz);
- 2 LTE antennas;
- Documentation booklets (quick guide for initial connection, license agreement, etc.)
Regarding network ports and interfaces, it has all the modern capabilities for traffic transmission and interaction, with a dedicated port for the DMZ zone, USB 3.0 for synchronization with a PC.
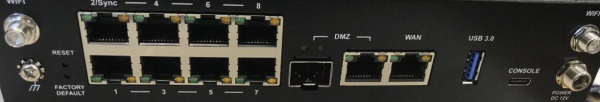
The 1590 version features an updated design, modern wireless options, and memory expansion: 2 slots for working with Micro/Nano SIM in LTE mode (we plan to write in detail about this option in one of the upcoming articles in our series dedicated to wireless connections); a slot for an SD card.
You can read in detail about the capabilities of the 1590 NGFW and other new models in of the series of articles on SMB CheckPoint solutions. We shall proceed with the initial device setup.
Initial setup
Our regular readers should already be aware that the 1500 series in the SMB line uses a new 80.20 Embedded OS, which includes an updated interface and enhanced capabilities.
To begin the initialization of the device, you need to:
- Provide power to the gateway.
- Connect the network cable from your PC to LAN-1 on the gateway.
- Optionally, you can immediately provide the device with Internet access by connecting the interface to the WAN port.
- Go to the Gaia Embedded portal:
If the previously mentioned steps have been completed, upon accessing the Gaia portal page, you will need to confirm the opening of the page with an untrusted certificate, after which the portal setup wizard will start:
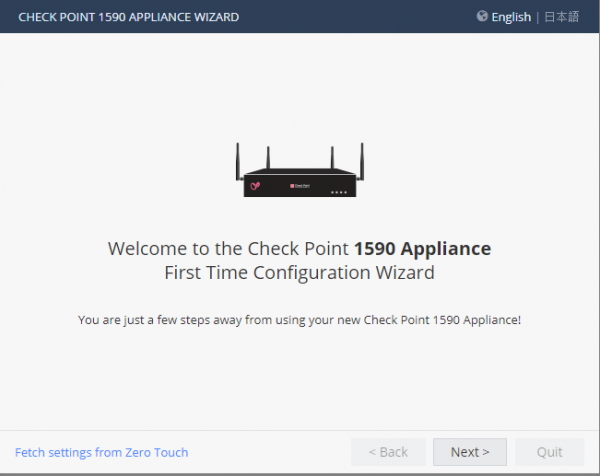
You will be greeted by a page indicating the model of your device, and you need to proceed to the next section:
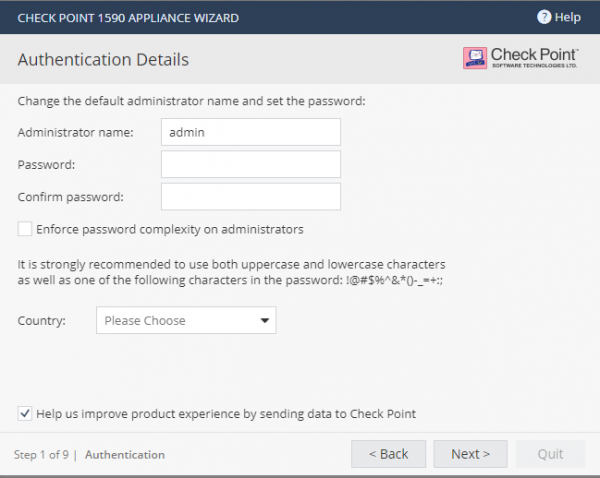
We will be prompted to create an account for authorization, with the option to specify high password requirements for the administrator, indicating the country where the gateway will be used.
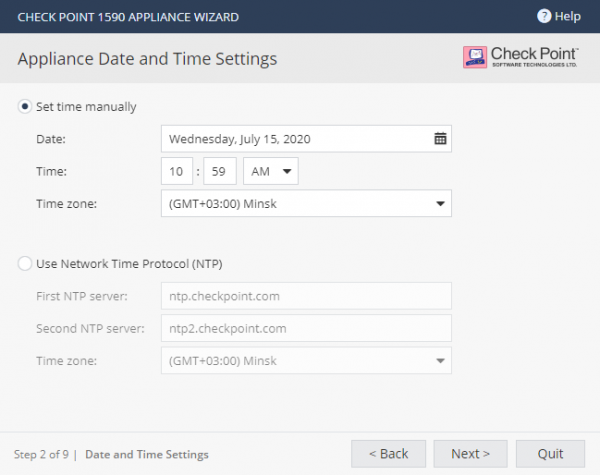
The next window concerns the date and time settings, where you can set them manually or use the company NTP server.
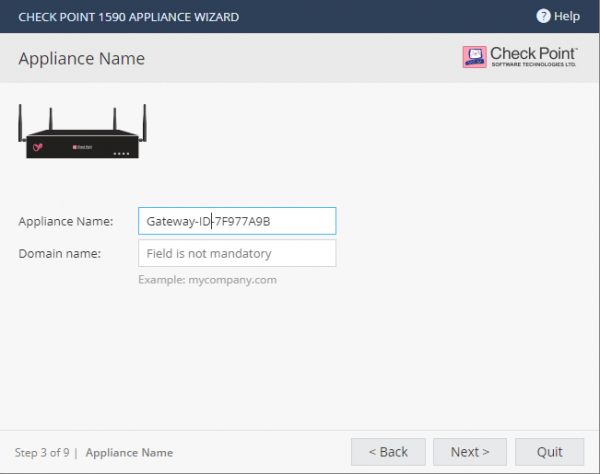
The next step involves setting a name for the device and specifying the company's domain for the correct operation of the gateway services on the Internet.
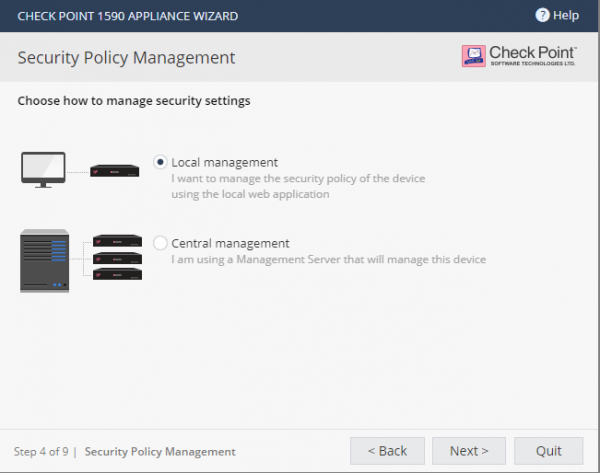
The following step concerns the choice of NGFW management type, where it should be noted:
- Local Management. This available option is for local management of the gateway using the Gaia Portal web page.
- Central Management. This management type includes synchronization with a dedicated CheckPoint Management server, synchronization with Smart1-Cloud, or with SMP (Service Management for SMB).
In this article, we will focus on the Local Management method; you can specify the method that is needed. For familiarization with the synchronization process with a dedicated Management Server, it is suggested from the CheckPoint Getting Started training cycle, prepared by TS Solution.
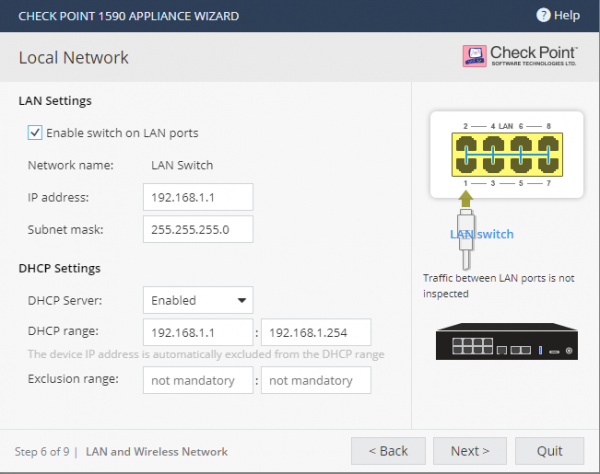
Next, a window will be presented defining the mode of operation for the interfaces on the gateway:
- Switch Mode implies connectivity between subnets from one interface to another interface's subnet.
- The Disable Switch mode, correspondingly, disables the Switch mode; each port routes traffic as a separate network fragment.
You are also prompted to set a pool of DHCP addresses that will be used when connecting to the gateway's local interfaces.
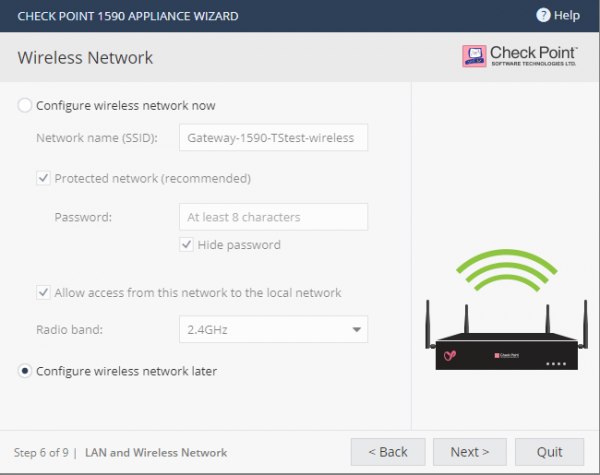
The next step is configuring the gateway to operate in wireless mode; we plan to cover this aspect in more detail in one of the articles in the cycle, so we postponed the configuration settings. However, you can create a new wireless access point, set a password for connecting to it, and define the operating mode of the wireless channel (2.4 GHz or 5 GHz).
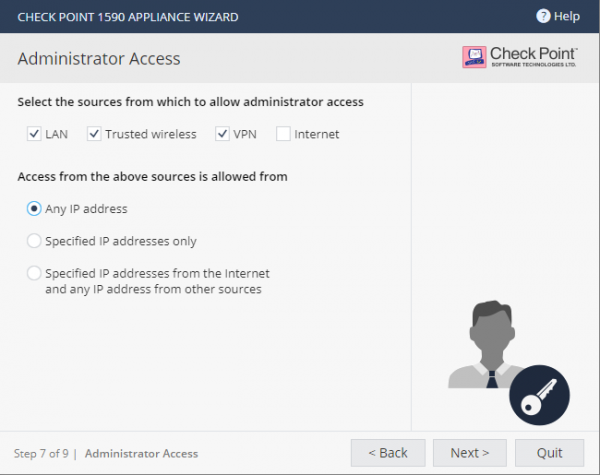
Next, a step will be proposed for setting up access to the gateway for company administrators. By default, access rights are granted if the connection is from:
- The company's internal subnet
- Trusted wireless network
- VPN tunnel
The option to connect to the gateway via the Internet is disabled by default; this poses significant risks and must be justified for enabling. Otherwise, it is recommended to leave it as in our example. There is also an option to specify which specific IP addresses will be permitted to connect to the gateway.
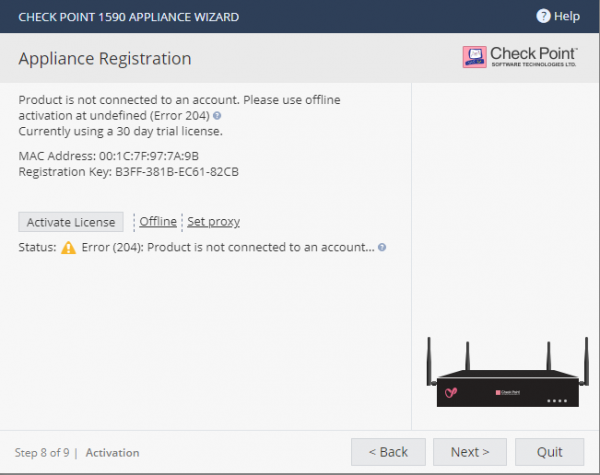
The next window concerns license activation. During the initial device setup, you will be presented with a 30-day trial period. There are two available methods for activation:
- If there is an Internet connection, the license will be activated automatically.
- If you activate the license offline, you need to do the following: download the license from UserCenter, register your device on a special . Next, for both cases, you will need to manually import the downloaded license.
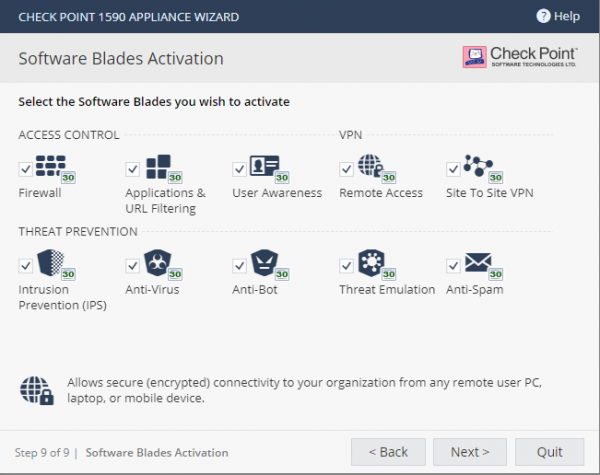
Finally, the last window in the setup wizard offers to select the blades to be enabled. Note that the QOS blade is activated only after the initial setup. As a result, you should see a completion window that summarizes your settings.
Initial Setup
First, we recommend checking the status of the licenses, as this will affect further configuration. Go to the 'HOME' → 'License' tab:
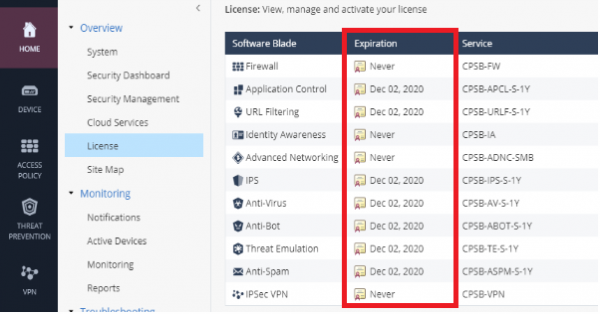
If the licenses are activated, it is advisable to immediately update to the latest firmware version. For this, go to the 'DEVICE' → 'System Operations' tab:
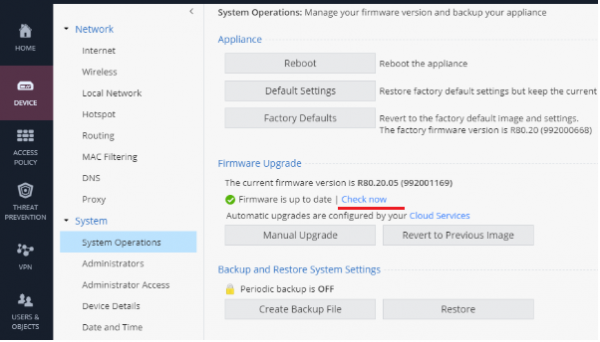
System updates are located under Firmware Upgrade. In our case, the latest and most current version of the firmware is installed.
Next, I will briefly describe the capabilities and settings of the system blades. They can logically be divided into Access level policies (Firewall, Application Control, URL Filtering) and Threat Prevention (IPS, Antivirus, Anti-Bot, Threat Emulation).
Let’s move to the Access Policy → Blade Control tab:
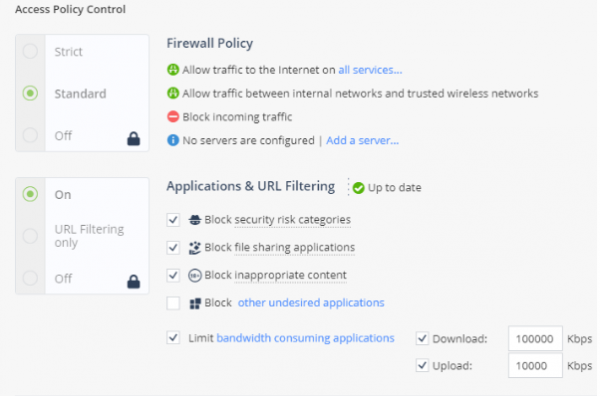
By default, the STANDARD mode is used, which allows: outgoing traffic to the Internet, traffic within the local network, while blocking incoming traffic from the Internet.
Regarding the APPLICATIONS & URL FILTERING blades, high-risk sites are blocked by default, along with the blocking of file-sharing applications (Torrent, File Storage, etc.). Additionally, specific website categories can be manually blocked.
We should note the option for user traffic 'Limit bandwidth consuming applications', allowing for speed limiting of outgoing/incoming traffic for application groups.
Next, we will open the Policy subsection, where rules are generated automatically by default according to previously described settings.
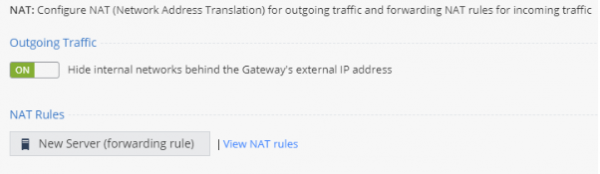
The NAT subsection operates by default in Global Hide Nat Automatic mode, meaning all internal hosts will access the Internet through a public IP address. It is possible to set NAT rules manually to publish your web applications or services.
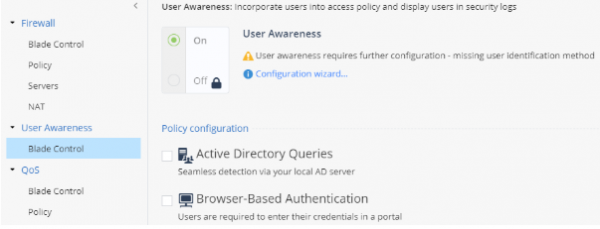
Next is the section concerning user authentication on the network, offering two options: Active Directory Queries (integration with your AD) and Browser-Based Authentication (the user enters domain credentials on the portal).
We should also touch on SSL inspection, as the share of overall HTTPS traffic in the global network is rapidly growing. Let's look at what solutions CheckPoint offers for SMB, for which we need to go to the SSL-Inspection → Policy section:
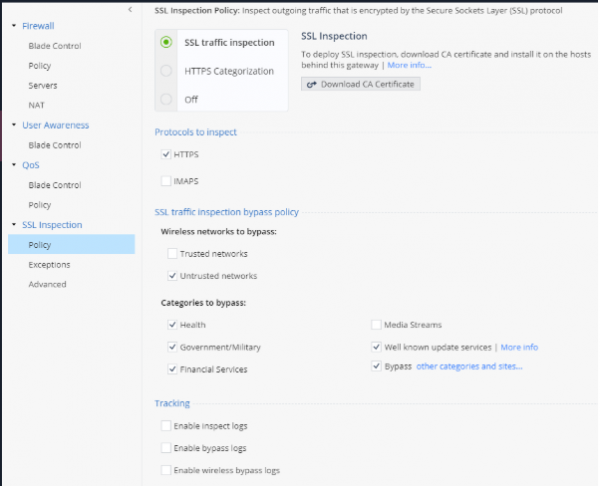
In the settings, there is an option to inspect HTTPS traffic, which will require importing a certificate and installing it in the trusted certificate center on user machines.
We consider the BYPASS mode for pre-set categories a convenient option, as it significantly saves time when enabling inspection.
After setting the rules at the Firewall/Application level, you should move on to tuning security policies (Threat Prevention) by accessing the corresponding section:
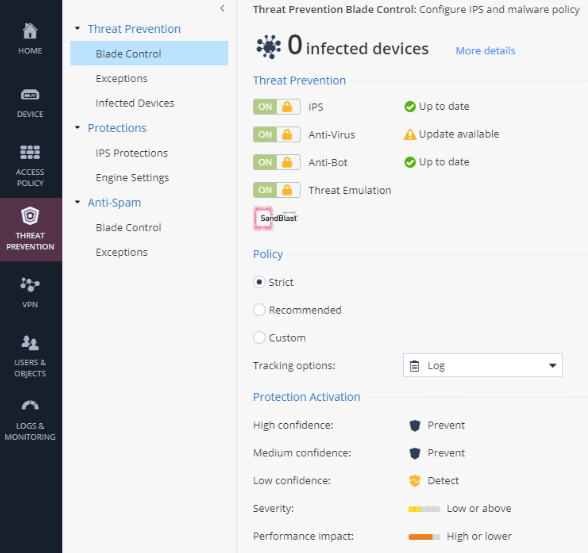
On the opened page, we see the enabled blades, the status of signature and database updates. We are also offered to choose a profile for perimeter network protection, with corresponding settings displayed.
A separate section 'IPS Protections' allows configuring actions for specific security signatures.
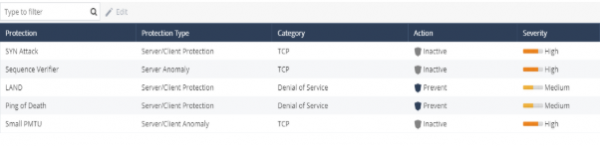
Recently, we wrote in our blog for Windows Server — SigRed. Let's check its presence in Gaia Embedded 80.20 by entering the query 'CVE-2020-1350'.
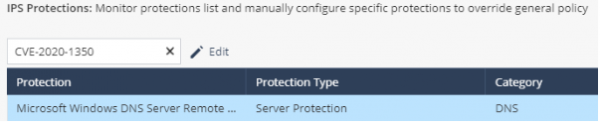
A record has been detected for this signature, to which one of the actions can be applied. (default Prevent for Critical danger level). Accordingly, with an SMB solution, you will not be left wanting in terms of updates and support; it is a complete NGFW solution for branch offices of up to 200 people from CheckPoint.
Performance Assessment
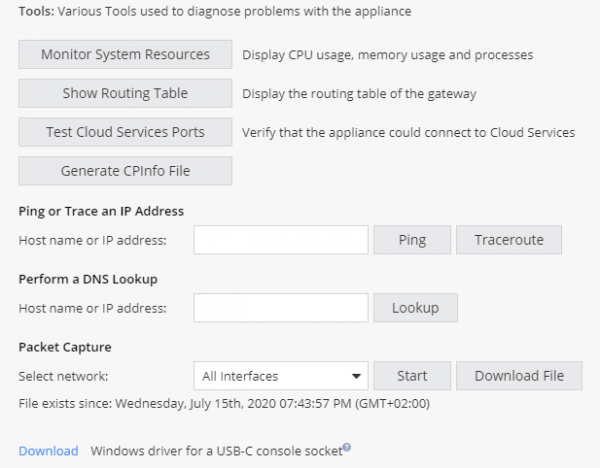
In concluding the article, I would like to highlight the availability of troubleshooting tools after the initial initialization and configuration of the SMB solution. You can navigate to the "HOME" → "Tools" section. Possible options include:
- system resource monitoring;
- routing table;
- availability check of CheckPoint cloud services;
- CPinfo generation;
Also, built-in network commands are available: Ping, Traceroute, Traffic Capture.
Thus, today we have examined and studied the initial connection and configuration of the NGFW 1590; similar actions will be performed for the entire series of the 1500 SMB Checkpoint. The available options have shown us high variability for settings, supporting modern traffic protection methods at the network perimeter.
Today, CheckPoint solutions for protecting small offices and branches (up to 200 people) have a wide range of tools and utilize the latest technologies (cloud management, SIM card support, memory expansion via SD cards, etc.). Stay tuned and read articles from TS Solution; we plan to continue releasing parts about the NGFW CheckPoint SMB family. See you soon!
. Stay tuned for updates (, , , , ).
Source: habr.com
