

The significance of Software Composition Analysis (SCA) in the development process is increasing as annual reports on vulnerabilities in open source libraries are published by companies like Synopsys, Sonatype, Snyk, and White Source. According to the report the number of identified vulnerabilities in open source in 2019 increased by almost 1.5 times compared to the previous year, while components with open source are used in 60% to 80% of projects. According to independent opinion, SCA processes are a separate practice of OWASP SAMM and BSIMM as a maturity indicator, and in the first half of 2020, OWASP released the new OWASP Software Component Verification Standard (SCVS), providing best practices for verifying third-party components in the software supply chain.
One of the most telling cases with Equifax in May 2017. Unknown attackers obtained information about 143 million Americans, including full names, addresses, social security numbers, and driver's license numbers. In 209,000 cases, documents also contained information about the victims' credit cards. This breach occurred due to the exploitation of a critical vulnerability in Apache Struts 2 (CVE-2017-5638), even though a fix had been released back in March 2017. The company had two months to implement the update, but no one addressed this issue.
This article will discuss the selection of a tool for conducting SCA from the perspective of analysis quality. A functional comparison of the tools will also be provided. The process of integration into CI/CD and integration capabilities will be left for future publications. A wide list of tools was presented by OWASP , but in this overview, we will only touch upon the most popular open source tool Dependency Check, the slightly less well-known open source platform Dependency Track, and the enterprise solution Sonatype Nexus IQ. We will also examine how these solutions work and compare the results regarding false positives.
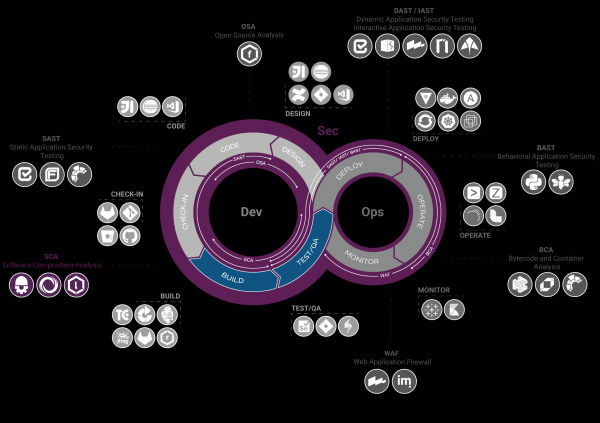
Operating principle
is a utility (CLI, maven, jenkins module, ant) that analyzes project files, gathering pieces of information about dependencies (package name, groupid, specification title, version…), constructs a CPE string (Common Platform Enumeration), Package URL (PURL) and identifies vulnerabilities for CPE/PURL from databases (NVD, Sonatype OSS Index, NPM Audit API…), after which it generates a one-time report in HTML, JSON, XML formats...
Let's see what a CPE looks like:
cpe:2.3:part:vendor:product:version:update:edition:language:sw_edition:target_sw:target_hw:other- Part: Indicates whether the component refers to an application (a), operating system (o), or hardware (h) (Required field)
- Vendor: The name of the product's manufacturer (Required field)
- Product: The name of the product (Required field)
- Version: Component version (Deprecated field)
- Update: Package update
- Edition: Inherited version (Deprecated field)
- Language: Language defined in RFC-5646
- SW Edition: Software version
- Target SW: The software environment in which the product operates
- Target HW: The hardware environment in which the product operates
- Other: Information about the vendor or product
An example of a CPE looks as follows:
cpe:2.3:a:pivotal_software:spring_framework:3.0.0:*:*:*:*:*:*:* This string indicates that CPE version 2.3 describes an application component from the manufacturer pivotal_software with the name spring_framework version 3.0.0. If we look up the vulnerability in the NVD, we can see a reference to this CPE. The primary issue to note immediately is that the CVE in the NVD, according to the CPE, reports an issue with the framework and not with a specific component. That is, if developers are heavily tied to the framework, and the identified vulnerability does not pertain to the modules used by them, the security specialist will have to delve into this CVE and consider an update.
The URL is also used by SCA tools. The format of the package URL is as follows:
scheme:type/namespace/name@version?qualifiers#subpath- Scheme: Will always be 'pkg', indicating that this is a package URL (Required field)
- Type: The 'type' of package or 'protocol' of the package, such as maven, npm, nuget, gem, pypi, etc. (Required field)
- Namespace: Some prefix of the name, such as a Maven group ID, Docker image owner, GitHub user, or organization. Optional and depends on the type.
- Name: Package name (Required field)
- Version: Package version
- Qualifiers: Additional qualification data for the package, such as OS, architecture, distribution, etc. Optional and type-dependent item.
- Subpath: An additional path in the package relative to the package root
For example:
pkg:golang/google.golang.org/genproto#googleapis/api/annotations
pkg:maven/org.apache.commons/io@1.3.4
pkg:pypi/django-package@1.11.1.dev1— an on-premise web platform that accepts ready-made Bill of Materials (BOM) generated and , that is, ready specifications of existing dependencies. This is an XML file describing dependencies — name, hashes, package url, publisher, license. Then Dependency Track parses the BOM, checks the existing CVEs related to the identified dependencies from the vulnerability database (NVD, Sonatype OSS Index …), after which it builds graphs, calculates metrics, regularly updating the vulnerability status of components.
An example of what a BOM can look like in XML format:
Apache
      org.apache.tomcat
      tomcat-catalina
      9.0.14

        3942447fac867ae5cdb3229b658f4d48
        e6b1000b94e835ffd37f4c6dcbdad43f4b48a02a
        f498a8ff2dd007e29c2074f5e4b01a9a01775c3ff3aeaf6906ea503bc5791b7b
        e8f33e424f3f4ed6db76a482fde1a5298970e442c531729119e37991884bdffab4f9426b7ee11fccd074eeda0634d71697d6f88a460dce0ac8d627a29f7d1282


          Apache-2.0


      pkg:maven/org.apache.tomcat/tomcat-catalina@9.0.14
BOM can be used not only as input parameters for Dependency Track but also for inventorying software components in the supply chain, for instance, to provide to the software customer. In 2014, a law was even proposed in the US , which stated that when purchasing software, any government agency must request a BOM to prevent the use of vulnerable components, but for various reasons, the act never came into force.
Returning to SCA, Dependency Track has ready-made integrations with Notification Platforms like Slack and vulnerability management systems like Kenna Security. It is also worth noting that Dependency Track identifies outdated package versions and provides information about licenses (thanks to SPDX support).
When it comes to the quality of SCA, there is a fundamental difference here.
Dependency Track does not accept a project as input, but rather accepts a BOM. This means that if we want to check a project, we first need to generate bom.xml, for example, using CycloneDX. Thus, Dependency Track directly depends on CycloneDX. At the same time, this allows for customization. For instance, the OZON team created for building BOM files for projects in Golang for further scanning via Dependency Track.
is a commercial SCA solution from Sonatype, which is part of the Sonatype ecosystem that also includes Nexus Repository Manager. Nexus IQ can accept both war archives (for Java projects) via web interface or API, and BOM, if your organization hasn't transitioned from CycloneDX to the new solution. Unlike open-source solutions, IQ not only refers to the CP/PURL of the identified component and the corresponding vulnerability in its database but also takes into account proprietary research, such as the name of the vulnerable function or class. The mechanisms of IQ will be explored later when analyzing the results.
Let's summarize some key functional features and also look at the supported languages for analysis:
Language
Nexus IQ
Dependency Check
Dependency Track
Java.
+
+
+
C/C++
+
+
—
C#
+
+
—
.Net
+
+
+
Erlang
—
—
+
JavaScript (NodeJS)
+
+
+
PHP
+
+
+
Python
+
+
+
Ruby
+
+
+
Perl
—
—
—
Scala
+
+
+
Objective C
+
+
—
Swift
+
+
—
R
+
—
—
Go
+
+
+
Functional capabilities
Functional capabilities
Nexus IQ
Dependency Check
Dependency Track
The ability to ensure the verification of components used in source code for license compliance.
+
—
+
The ability to scan and analyze Docker images for vulnerabilities and license compliance.
+ Integration with Clair
—
—
The ability to set security policies for using open source libraries.
+
—
—
The ability to scan open source repositories for vulnerable components.
+ RubyGems, Maven, NPM, Nuget, Pypi, Conan, Bower, Conda, Go, p2, R, Yum, Helm, Docker, CocoaPods, Git LFS
—
+ Hex, RubyGems, Maven, NPM, Nuget, Pypi
The presence of a specialized research group.
+
—
—
Operation in a closed loop.
+
+
+
Use of third-party databases.
+ Sonatype's closed database.
+ Sonatype OSS, NPM Public Advisors.
+ Sonatype OSS, NPM Public Advisors, RetireJS, VulnDB, support for proprietary vulnerability databases.
The ability to filter open source components when attempting to upload them to the development loop according to configured policies.
+
—
—
Recommendations for fixing vulnerabilities, including links to fixes.
+
+- (depends on the description in public databases)
+- (depends on the description in public databases)
Ranking of identified vulnerabilities by criticality
+
+
+
Role-based access model
+
—
+
Support for Command Line Interface (CLI)
+
+
+- (only for CycloneDX)
Sampling / sorting of vulnerabilities by defined criteria
+
—
+
Dashboard for application status
+
—
+
PDF report generation
+
—
—
Report generation in JSONCSV format
+
+
—
Support for the Russian language
—
—
—
Integration capabilities
Integration
Nexus IQ
Dependency Check
Dependency Track
Integration with LDAP / Active Directory
+
—
+
Integration with the continuous integration system (continous integration) Bamboo
+
—
—
Integration with the continuous integration system (continous integration) TeamCity
+
—
—
Integration with the continuous integration system (continous integration) GitLab
+
+- (as a plugin for GitLab)
+
Integration with the continuous integration system (continous integration) Jenkins
+
+
+
Availability of plugins for IDEs
+ IntelliJ, Eclipse, Visual Studio
—
—
Support for customized integration via web-services (API) of the tool
+
—
+
Dependency Check
First launch
Let's run Dependency Check against a deliberately vulnerable application .
For this, we will use :
mvn org.owasp:dependency-check-maven:checkAs a result, the dependency-check-report.html will appear in the target directory.
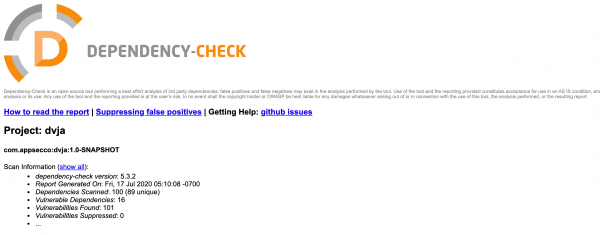
Let's open the file. After the summary information on the total number of vulnerabilities, we can see information on vulnerabilities with high levels of Severity and Confidence with indications of the package, CPE, and the number of CVE.
Next comes more detailed information, including what the decision was based on (evidence), that is, a BOM.
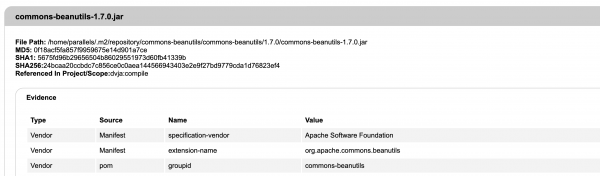
Then comes CPE, PURL, and a description of CVE. Recommendations for remediation are not provided due to their absence in the NVD database.
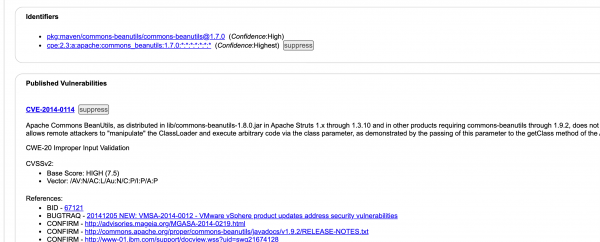
For systematic viewing of scan results, you can configure Nginx with minimal settings, or send the detected defects to a defect management system that supports connectors to Dependency Check. For example, Defect Dojo.
Dependency Track
Installation
Dependency Track, in turn, is a web platform with graph displays, so the acute issue of storing defects in a third-party solution is not present here.
The following installation scenarios are supported: Docker, WAR, Executable WAR.
First launch
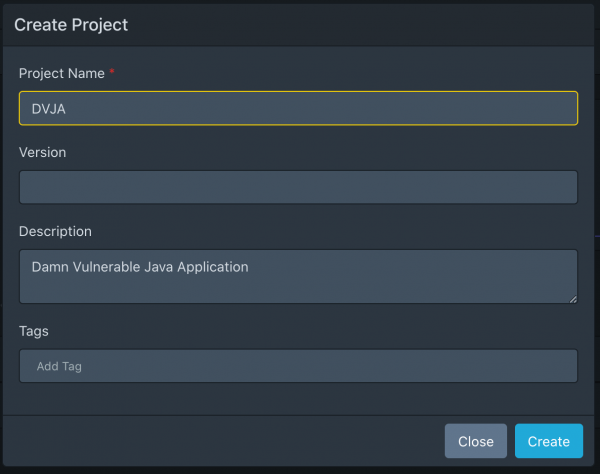
Go to the URL of the launched service. Log in via admin/admin, change the username and password, after which we arrive at the Dashboard. The next thing we will do is create a project for the test application in Java at Home / Projects → Create Project . As an example, we will take DVJA.
Since Dependency Track can only accept BOM as input, we need to obtain this BOM. Let's use :
mvn org.cyclonedx:cyclonedx-maven-plugin:makeAggregateBomWe obtain bom.xml and upload the file in the created project DVJA → Dependencies → Upload BOM.
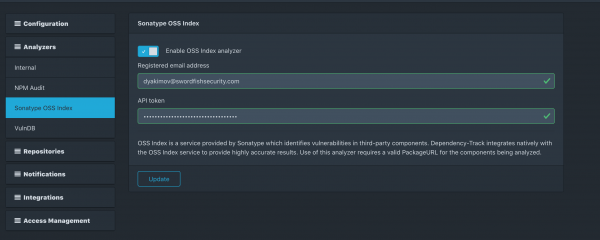
Let's go to Administration → Analyzers. We understand that we only have the Internal Analyzer enabled, which includes NVD. We will also connect Sonatype OSS Index.
Thus, we will get the following picture for our project:
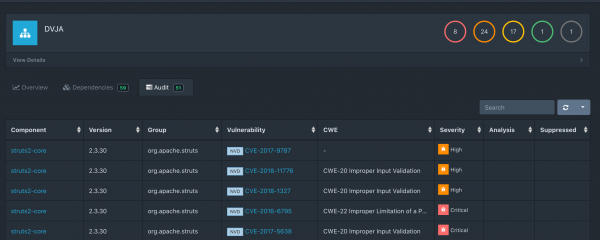
Also, in the list, we can find one vulnerability applicable to Sonatype OSS:
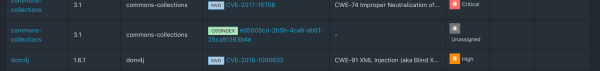
The main disappointment was that Dependency Track no longer accepts Dependency Check XML reports. The last supported versions of the integration with Dependency Check were 1.0.0 — 4.0.2, while I was testing 5.3.2.
Here Volume Provisioning. ), when it was still possible.
Nexus IQ
First launch
Nexus IQ is installed from archives via , but we have built a Docker image for this purpose.
After logging into the console, you need to create an Organization and an Application.
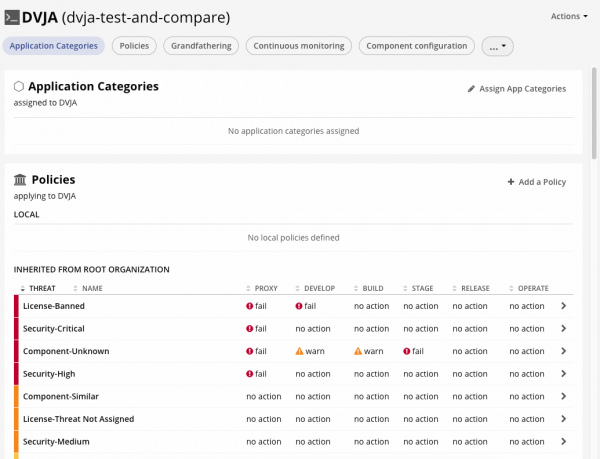
As can be seen, the configuration in the case of IQ is somewhat more complex, as we also need to create policies applicable for different stages (dev, build, stage, release). This is necessary to block vulnerable components as they move further down the pipeline closer to production, or to block them as soon as they enter Nexus Repo when downloaded by developers.
To experience the difference between open source and enterprise, let's perform the same scan through Nexus IQ similar to , first creating a test application in the NexusIQ interface dvja-test-and-compare:
mvn com.sonatype.clm:clm-maven-plugin:evaluate -Dclm.applicationId=dvja-test-and-compare -Dclm.serverUrl= -Dclm.username= -Dclm.password=
Go to the URL for the generated report in the IQ web interface:
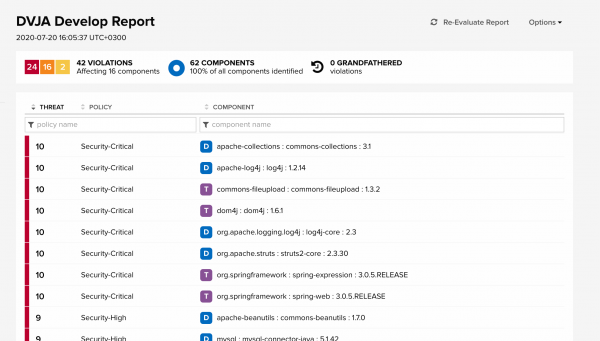
Here you can see all policy violations indicating various levels of significance (from Info to Security Critical). The letter D next to a component means that the component is a Direct Dependency, while the letter T next to a component indicates that the component is a Transitive Dependency.
By the way, the report by Snyk reports that more than 70% of open source vulnerabilities discovered in Node.js, Java, and Ruby are located in transitive dependencies.
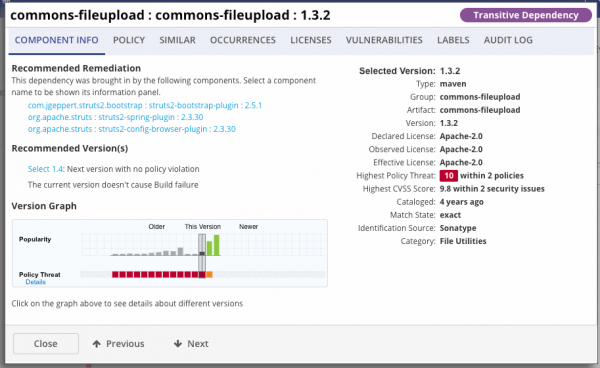
If you open one of the Nexus IQ policy violations, you can see a description of the component, as well as a Version Graph that shows the location of the current version on the timeline graph, as well as when the vulnerability ceases to be vulnerable. The height of the candles on the graph indicates the popularity of the use of this component.
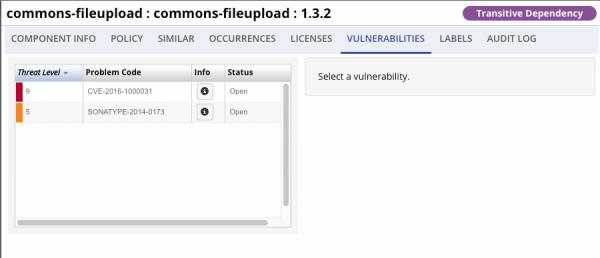
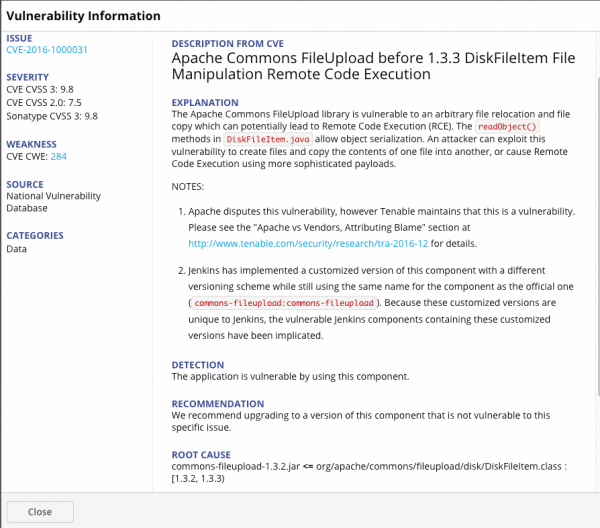
If you go to the vulnerabilities section and expand the CVE, you can read the description of this vulnerability, remediation recommendations, as well as the reason why this component fell under the violation, namely the presence of the class DiskFileitem.class.
Let's summarize only concerning third-party Java components, removing JS components. In parentheses, we will indicate the number of vulnerabilities found outside of the NVD.
Total Nexus IQ:
- Dependencies Scanned: 62
- Vulnerable Dependencies: 16
- Vulnerabilities Found: 42 (8 sonatype db)
Total Dependency Check:
- Dependencies Scanned: 47
- Vulnerable Dependencies: 13
- Vulnerabilities Found: 91 (14 sonatype oss)
Total Dependency Track:
- Dependencies Scanned: 59
- Vulnerable Dependencies: 10
- Vulnerabilities Found: 51 (1 sonatype oss)
The next step is to analyze the results obtained and figure out which of these vulnerabilities is a real defect and which is a false positive.
Disclaimer
This review is not an undisputed truth. The author did not set out to highlight a specific tool against others. The purpose of the review was to show the mechanisms of SCA tools and the ways to verify their results.
Comparison of results
Conditions:
A false positive concerning the vulnerabilities of third-party components is:
- Mismatch of CVE to the identified component
- For example, if a vulnerability is identified in the Struts2 framework, and the tool points to a component of the Struts-tiles framework, to which this vulnerability does not apply, then this is a false positive.
- Mismatch of CVE to the identified version of the component
- For example, the vulnerability is tied to version python > 3.5 and the tool flags version 2.7 as vulnerable — this is a false positive, as the vulnerability actually only applies to the 3.x product branch.
- Duplicate CVE
- For example, if SCA indicated a CVE that allows for RCE, after which SCA points for this same component to a CVE applicable to Cisco products susceptible to this RCE. In this case, it will be a false positive.
- For example, a CVE was found in the spring-web component, after which SCA points to the same CVE in other components of the Spring Framework, while the CVE has no relation to other components. In this case, it will be a false positive.
The research object is the Open Source project DVJA. The study involved only Java components (without JS).
Summary of Results
Let's move directly to the results of the manual review of the identified vulnerabilities. A complete report for each CVE can be found in the Appendix.
Summary of results for all vulnerabilities:
Parameter
Nexus IQ
Dependency Check
Dependency Track
Total vulnerabilities identified
42
91
51
Incorrectly identified vulnerabilities (false positive)
2(4.76%)
62(68,13%)
29(56.86%)
No relevant vulnerabilities detected (false negative)
10
20
27
Summary of results by components:
Parameter
Nexus IQ
Dependency Check
Dependency Track
Total components identified
62
47
59
Total vulnerable components
16
13
10
Incorrectly identified vulnerable components (false positive)
1
5
0
Incorrectly identified vulnerable components (false positive)
0
6
6
We will build visual graphs to assess the ratio of false positives and false negatives to the total number of vulnerabilities. Components are marked horizontally, and vulnerabilities identified in them are marked vertically.
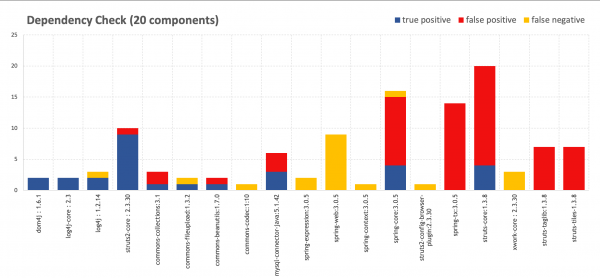
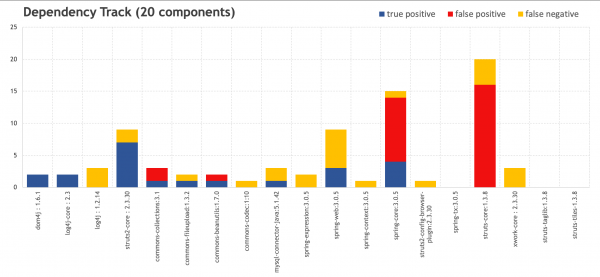
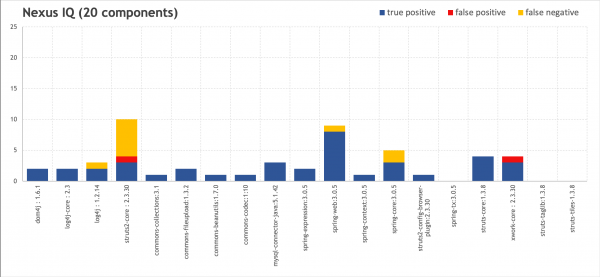
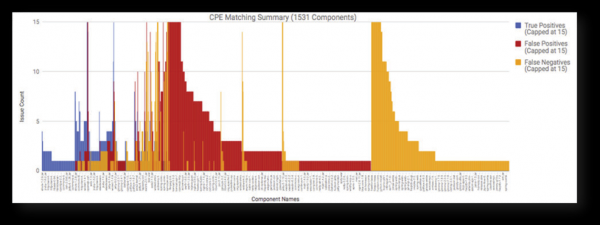
For comparison, a similar study was conducted by the Sonatype team testing a project of 1531 components using OWASP Dependency Check. As we can see, the noise-to-true positive ratio is comparable to our results.
Source:
Let's consider some CVEs from the results of our scan to understand the reasons for these results.
Learn more
№1
First, let’s analyze some interesting points from Sonatype Nexus IQ.
Nexus IQ points to a deserialization issue with the possibility of executing RCE in the Spring Framework several times. CVE-2016-1000027 in spring-web:3.0.5 for the first time, and CVE-2011-2894 in spring-context:3.0.5 and spring-core:3.0.5. At first glance, it seems that there is a duplication of vulnerability across several CVEs. Because, if you look at CVE-2016-1000027 and CVE-2011-2894 in the NVD database, it seems all too obvious.
Component
The vulnerability
spring-web:3.0.5
CVE-2016-1000027
spring-context:3.0.5
CVE-2011-2894
spring-core:3.0.5
CVE-2011-2894
Description from NVD:
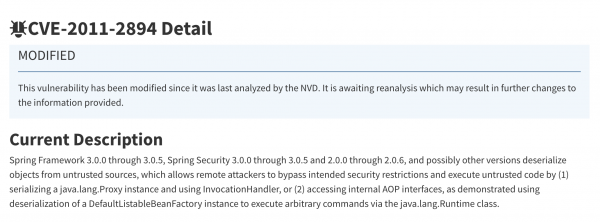
Description from NVD:
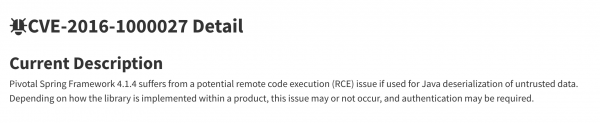
CVE-2011-2894 itself is quite well known. In the report this CVE was recognized as one of the most frequently encountered. The descriptions for CVE-2016-100027 are somewhat minimal in NVD, and they seem to apply only for Spring Framework 4.1.4. Let's take a look at and here it becomes more or less clear. From we understand that in addition to the vulnerability in RemoteInvocationSerializingExporter in CVE-2011-2894, a vulnerability is observed in HttpInvokerServiceExporter. This is what Nexus IQ tells us:
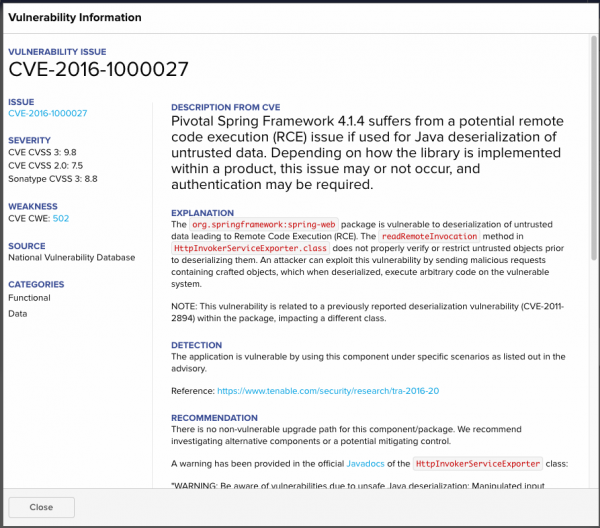
However, there is nothing like this in the NVD, which causes Dependency Check and Dependency Track to receive false negatives.
Additionally, from the description of CVE-2011-2894, we can understand that the vulnerability is indeed present in spring-context:3.0.5 and spring-core:3.0.5. Confirmation of this can be found in an article by the researcher who discovered the vulnerability.
№2
Component
The vulnerability
Result
struts2-core:2.3.30
CVE-2016-4003
FALSE
If we examine the vulnerability CVE-2016-4003, we will see that it was fixed back in version 2.3.28, yet Nexus IQ still reports it. The description of the vulnerability includes a note:
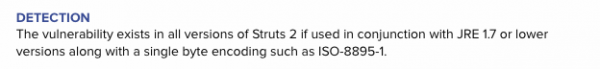
This means that the vulnerability exists only in conjunction with an outdated version of the JRE, which we were warned about. Nevertheless, we consider this a False Positive, although not the most serious one.
№ 3
Component
The vulnerability
Result
xwork-core:2.3.30
CVE-2017-9804
TRUE
xwork-core:2.3.30
CVE-2017-7672
FALSE
If we look at the description of CVE-2017-9804 and CVE-2017-7672, we will understand that the problem lies in the URLValidator class, with CVE-2017-9804 stemming from CVE-2017-7672. The presence of the second vulnerability does not provide any useful information other than raising its severity to High, so it can be considered unnecessary noise.
Overall, no other false positives were found for Nexus IQ.
№4
There are several aspects that distinguish IQ from other solutions.
Component
The vulnerability
Result
spring-web:3.0.5
CVE-2020-5398
TRUE
The CVE in the NVD reports that it applies only to versions 5.2.x up to 5.2.3, 5.1.x up to 5.1.13, and versions 5.0.x up to 5.0.16; however, if we look at the description of the CVE in Nexus IQ, we will see the following:
Advisory Deviation Notice: The Sonatype security research team discovered that this vulnerability was introduced in version 3.0.2.RELEASE and not 5.0.x as stated in the advisory.
Following this, a PoC for this vulnerability indicates that it is present in version 3.0.5.
False negatives are sent to Dependency Check and Dependency Track.
№5
Let’s take a look at false positives for Dependency Check and Dependency Track.
Dependency Check is uniquely highlighted as it reflects those CVEs that relate to the entire framework in the NVD, in components to which these CVEs do not apply. This concerns CVE-2012-0394, CVE-2013-2115, CVE-2014-0114, CVE-2015-0899, CVE-2015-2992, CVE-2016-1181, CVE-2016-1182, which Dependency Check has attached to struts-taglib:1.3.8 and struts-tiles-1.3.8. These components have nothing to do with what is described in the CVE — request handling, page validation, and so on. This is because the only commonality between these CVEs and the components is the framework, which is why Dependency Check counted it as a vulnerability.
The same situation applies to spring-tx:3.0.5, and a similar situation exists with struts-core:1.3.8. For struts-core, Dependency Check and Dependency Track found many vulnerabilities that actually apply to struts2-core, which is essentially a separate framework. In this case, Nexus IQ correctly understood the picture and indicated in the CVEs it provided that struts-core reached its end of life and it's necessary to transition to struts2-core.
No.6
In some situations, interpreting explicit errors from Dependency Check and Dependency Track is unfair. Specifically, CVE-2013-4152, CVE-2013-6429, CVE-2013-6430, CVE-2013-7315, CVE-2014-0054, and CVE-2014-0225, which were attributed by Dependency Check and Dependency Track to spring-core:3.0.5, actually refer to spring-web:3.0.5. While some of these CVEs were also found by Nexus IQ, IQ correctly identified them with a different component. The absence of these vulnerabilities in spring-core does not mean they are non-existent in the framework itself, and the open-source tools justly pointed out these vulnerabilities (they simply missed slightly).
Conclusions
As we can see, the assessment of the validity of identified vulnerabilities through manual review does not yield definitive results, leading to contentious points. The outcomes indicate that the Nexus IQ solution has the lowest false positive rate and the highest accuracy.
Firstly, this is due to the Sonatype team expanding the description for each CVE vulnerability from the NVD in their databases, specifying with precision the class or function of the vulnerability for each version of the component, conducting additional research (for example, verifying vulnerabilities in older software versions).
The vulnerabilities that did not make it to the NVD but are nonetheless present in the Sonatype database with a SONATYPE tag also significantly influence the results. According to the report about 45% of the open-source vulnerabilities found are not reported in the NVD. According to the WhiteSource database, only 29% of all open-source vulnerabilities registered outside of the NVD ultimately get published there, which is why it's so important to seek vulnerabilities in other sources as well.
As a result, Dependency Check generates a lot of noise, missing some vulnerable components. Dependency Track generates less noise and identifies a large number of components, which visually doesn’t strain the eyes in the web interface.
Nevertheless, practice shows that open source should be the first step towards a mature DevSecOps. The first thing to consider when integrating SCA into development is the processes, specifically the discussions with management and related departments about what ideal processes should look like in your organization. It may turn out that for your organization, Dependency Check or Dependency Track will meet all the business needs initially, while enterprise solutions will logically follow as application complexity grows.
Appendix A. Results related to components
Legend:
- High — vulnerabilities of high and critical level in the component
- Medium — vulnerabilities of medium criticality level in the component
- TRUE — correctly identified vulnerability (True positive issue)
- FALSE — false alarm (False positive issue)
Component
Nexus IQ
Dependency Check
Dependency Track
Result
dom4j: 1.6.1
High
High
High
TRUE
log4j-core: 2.3
High
High
High
TRUE
log4j: 1.2.14
High
High
—
TRUE
commons-collections:3.1
High
High
High
TRUE
commons-fileupload:1.3.2
High
High
High
TRUE
commons-beanutils:1.7.0
High
High
High
TRUE
commons-codec:1:10
Medium
—
—
TRUE
mysql-connector-java:5.1.42
High
High
High
TRUE
spring-expression:3.0.5
High
component not found
TRUE
spring-web:3.0.5
High
component not found
High
TRUE
spring-context:3.0.5
Medium
component not found
—
TRUE
spring-core:3.0.5
Medium
High
High
TRUE
struts2-config-browser-plugin:2.3.30
Medium
—
—
TRUE
spring-tx:3.0.5
—
High
—
FALSE
struts-core:1.3.8
High
High
High
TRUE
xwork-core: 2.3.30
High
—
—
TRUE
struts2-core: 2.3.30
High
High
High
TRUE
struts-taglib:1.3.8
—
High
—
FALSE
struts-tiles-1.3.8
—
High
—
FALSE
Appendix B. Results related to vulnerabilities
Legend:
- High — vulnerabilities of high and critical level in the component
- Medium — vulnerabilities of medium criticality level in the component
- TRUE — correctly identified vulnerability (True positive issue)
- FALSE — false alarm (False positive issue)
Component
Nexus IQ
Dependency Check
Dependency Track
Severity
Result
Comment
dom4j: 1.6.1
CVE-2018-1000632
CVE-2018-1000632
CVE-2018-1000632
High
TRUE
CVE-2020-10683
CVE-2020-10683
CVE-2020-10683
High
TRUE
log4j-core: 2.3
CVE-2017-5645
CVE-2017-5645
CVE-2017-5645
High
TRUE
CVE-2020-9488
CVE-2020-9488
CVE-2020-9488
Low
TRUE
log4j: 1.2.14
CVE-2019-17571
CVE-2019-17571
—
High
TRUE
—
CVE-2020-9488
—
Low
TRUE
SONATYPE-2010-0053
—
—
High
TRUE
commons-collections:3.1
—
CVE-2015-6420
CVE-2015-6420
High
FALSE
Duplicates RCE(OSSINDEX)
—
CVE-2017-15708
CVE-2017-15708
High
FALSE
Duplicates RCE(OSSINDEX)
SONATYPE-2015-0002
RCE (OSSINDEX)
RCE(OSSINDEX)
High
TRUE
commons-fileupload:1.3.2
CVE-2016-1000031
CVE-2016-1000031
CVE-2016-1000031
High
TRUE
SONATYPE-2014-0173
—
—
Medium
TRUE
commons-beanutils:1.7.0
CVE-2014-0114
CVE-2014-0114
CVE-2014-0114
High
TRUE
—
CVE-2019-10086
CVE-2019-10086
High
FALSE
The vulnerability applies only to versions 1.9.2+
commons-codec:1:10
SONATYPE-2012-0050
—
—
Medium
TRUE
mysql-connector-java:5.1.42
CVE-2018-3258
CVE-2018-3258
CVE-2018-3258
High
TRUE
CVE-2019-2692
CVE-2019-2692
—
Medium
TRUE
—
CVE-2020-2875
—
Medium
FALSE
The same vulnerability as CVE-2019-2692, but with the note ‘attacks may significantly impact additional products’
—
CVE-2017-15945
—
High
FALSE
Not applicable to mysql-connector-java
—
CVE-2020-2933
—
Low
FALSE
Duplicate of CVE-2020-2934
CVE-2020-2934
CVE-2020-2934
—
Medium
TRUE
spring-expression:3.0.5
CVE-2018-1270
component not found
—
High
TRUE
CVE-2018-1257
—
—
Medium
TRUE
spring-web:3.0.5
CVE-2016-1000027
component not found
—
High
TRUE
CVE-2014-0225
—
CVE-2014-0225
High
TRUE
CVE-2011-2730
—
—
High
TRUE
—
—
CVE-2013-4152
Medium
TRUE
CVE-2018-1272
—
—
High
TRUE
CVE-2020-5398
—
—
High
TRUE
Strong example in favor of IQ: 'The Sonatype security research team discovered that this vulnerability was introduced in version 3.0.2.RELEASE and not 5.0.x as stated in the advisory.'
CVE-2013-6429
—
—
Medium
TRUE
CVE-2014-0054
—
CVE-2014-0054
Medium
TRUE
CVE-2013-6430
—
—
Medium
TRUE
spring-context:3.0.5
CVE-2011-2894
component not found
—
Medium
TRUE
spring-core:3.0.5
—
CVE-2011-2730
CVE-2011-2730
High
TRUE
CVE-2011-2894
CVE-2011-2894
CVE-2011-2894
Medium
TRUE
—
—
CVE-2013-4152
Medium
FALSE
Duplicate of the same vulnerability in spring-web
—
CVE-2013-4152
—
Medium
FALSE
The vulnerability pertains to the spring-web component
—
CVE-2013-6429
CVE-2013-6429
Medium
FALSE
The vulnerability pertains to the spring-web component
—
CVE-2013-6430
—
Medium
FALSE
The vulnerability pertains to the spring-web component
—
CVE-2013-7315
CVE-2013-7315
Medium
FALSE
SPLIT from CVE-2013-4152. + The vulnerability pertains to the spring-web component
—
CVE-2014-0054
CVE-2014-0054
Medium
FALSE
The vulnerability pertains to the spring-web component
—
CVE-2014-0225
—
High
FALSE
The vulnerability pertains to the spring-web component
—
—
CVE-2014-0225
High
FALSE
Duplicate of the same vulnerability in spring-web
—
CVE-2014-1904
CVE-2014-1904
Medium
FALSE
The vulnerability pertains to the spring-web-mvc component
—
CVE-2014-3625
CVE-2014-3625
Medium
FALSE
The vulnerability pertains to the spring-web-mvc component
—
CVE-2016-9878
CVE-2016-9878
High
FALSE
The vulnerability pertains to the spring-web-mvc component
—
CVE-2018-1270
CVE-2018-1270
High
FALSE
For spring-expression / spring-messages
—
CVE-2018-1271
CVE-2018-1271
Medium
FALSE
The vulnerability pertains to the spring-web-mvc component
—
CVE-2018-1272
CVE-2018-1272
High
TRUE
CVE-2014-3578
CVE-2014-3578 (OSSINDEX)
CVE-2014-3578
Medium
TRUE
SONATYPE-2015-0327
—
—
Low
TRUE
struts2-config-browser-plugin:2.3.30
SONATYPE-2016-0104
—
—
Medium
TRUE
spring-tx:3.0.5
—
CVE-2011-2730
—
High
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2011-2894
—
High
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2013-4152
—
Medium
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2013-6429
—
Medium
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2013-6430
—
Medium
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2013-7315
—
Medium
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2014-0054
—
Medium
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2014-0225
—
High
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2014-1904
—
Medium
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2014-3625
—
Medium
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2016-9878
—
High
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2018-1270
—
High
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2018-1271
—
Medium
FALSE
The vulnerability does not pertain to spring-tx
—
CVE-2018-1272
—
Medium
FALSE
The vulnerability does not pertain to spring-tx
struts-core:1.3.8
—
CVE-2011-5057 (OSSINDEX)
Medium
FALSE
Vulnerability for Struts 2
—
CVE-2012-0391 (OSSINDEX)
CVE-2012-0391
High
FALSE
Vulnerability for Struts 2
—
CVE-2014-0094 (OSSINDEX)
CVE-2014-0094
Medium
FALSE
Vulnerability for Struts 2
—
CVE-2014-0113 (OSSINDEX)
CVE-2014-0113
High
FALSE
Vulnerability for Struts 2
CVE-2016-1182
3VE-2016-1182
—
High
TRUE
—
—
CVE-2011-5057
Medium
FALSE
Vulnerability for Struts 2
—
CVE-2012-0392 (OSSINDEX)
CVE-2012-0392
High
FALSE
Vulnerability for Struts 2
—
CVE-2012-0393 (OSSINDEX)
CVE-2012-0393
Medium
FALSE
Vulnerability for Struts 2
CVE-2015-0899
CVE-2015-0899
—
High
TRUE
—
CVE-2012-0394
CVE-2012-0394
Medium
FALSE
Vulnerability for Struts 2
—
CVE-2012-0838 (OSSINDEX)
CVE-2012-0838
High
FALSE
Vulnerability for Struts 2
—
CVE-2013-1965 (OSSINDEX)
CVE-2013-1965
High
FALSE
Vulnerability for Struts 2
—
CVE-2013-1966 (OSSINDEX)
CVE-2013-1966
High
FALSE
Vulnerability for Struts 2
—
CVE-2013-2115
CVE-2013-2115
High
FALSE
Vulnerability for Struts 2
—
CVE-2013-2134 (OSSINDEX)
CVE-2013-2134
High
FALSE
Vulnerability for Struts 2
—
CVE-2013-2135 (OSSINDEX)
CVE-2013-2135
High
FALSE
Vulnerability for Struts 2
CVE-2014-0114
CVE-2014-0114
—
High
TRUE
—
CVE-2015-2992
CVE-2015-2992
Medium
FALSE
Vulnerability for Struts 2
—
CVE-2016-0785 (OSSINDEX)
CVE-2016-0785
High
FALSE
Vulnerability for Struts 2
CVE-2016-1181
CVE-2016-1181
—
High
TRUE
—
CVE-2016-4003 (OSSINDEX)
CVE-2016-4003
High
FALSE
Vulnerability for Struts 2
xwork-core:2.3.30
CVE-2017-9804
—
—
High
TRUE
SONATYPE-2017-0173
—
—
High
TRUE
CVE-2017-7672
—
—
High
FALSE
Duplicate of CVE-2017-9804
SONATYPE-2016-0127
—
—
High
TRUE
struts2-core:2.3.30
—
CVE-2016-6795
CVE-2016-6795
High
TRUE
—
CVE-2017-9787
CVE-2017-9787
High
TRUE
—
CVE-2017-9791
CVE-2017-9791
High
TRUE
—
CVE-2017-9793
—
High
FALSE
Duplicate of CVE-2018-1327
—
CVE-2017-9804
—
High
TRUE
—
CVE-2017-9805
CVE-2017-9805
High
TRUE
CVE-2016-4003
—
—
Medium
FALSE
Applicable to Apache Struts 2.x up to 2.3.28, while this is version 2.3.30. However, based on the description, CVE applies to all Struts 2 versions when using JRE 1.7 and below. It seems like they decided to play it safe, but it looks more like a FALSE.
—
CVE-2018-1327
CVE-2018-1327
High
TRUE
CVE-2017-5638
CVE-2017-5638
CVE-2017-5638
High
TRUE
The very vulnerability exploited by attackers in Equifax in 2017.
CVE-2017-12611
CVE-2017-12611
—
High
TRUE
CVE-2018-11776
CVE-2018-11776
CVE-2018-11776
High
TRUE
struts-taglib:1.3.8
—
CVE-2012-0394
—
Medium
FALSE
For struts2-core.
—
CVE-2013-2115
—
High
FALSE
For struts2-core.
—
CVE-2014-0114
—
High
FALSE
For commons-beanutils.
—
CVE-2015-0899
—
High
FALSE
Not applicable to taglib.
—
CVE-2015-2992
—
Medium
FALSE
Applicable to struts2-core.
—
CVE-2016-1181
—
High
FALSE
Not applicable to taglib.
—
CVE-2016-1182
—
High
FALSE
Not applicable to taglib.
struts-tiles-1.3.8
—
CVE-2012-0394
—
Medium
FALSE
For struts2-core.
—
CVE-2013-2115
—
High
FALSE
For struts2-core.
—
CVE-2014-0114
—
High
FALSE
Under commons-beanutils.
—
CVE-2015-0899
—
High
FALSE
Not applicable to tiles.
—
CVE-2015-2992
—
Medium
FALSE
For struts2-core.
—
CVE-2016-1181
—
High
FALSE
Not applicable to taglib.
—
CVE-2016-1182
—
High
FALSE
Not applicable to taglib.
Source: habr.com
