

In this post, we will discuss how the OceanLotus cyber group (APT32 and APT-C-00) recently exploited one of the publicly available exploits for , a vulnerability related to memory corruption in Microsoft Office, and how the group's malware maintains persistence on compromised systems, leaving no traces. We will also describe how the group has used self-extracting archives to execute code since early 2019.
OceanLotus specializes in cyber espionage, with primary targets being Southeast Asian countries. The attackers forge documents that attract the attention of potential victims to convince them to execute the backdoor, while also working on developing their toolkit. The techniques used to create bait vary in different attacks—from files with 'double extensions', self-extracting archives, macro-enabled documents to known exploits.
Exploitation in Microsoft Equation Editor
In mid-2018, OceanLotus conducted a campaign that leveraged the CVE-2017-11882 vulnerability. One of the group's malicious documents was analyzed by experts at the 360 Threat Intelligence Center (), providing a detailed description of the exploit. Below is an overview of a similar malicious document.
First Stage
Document FW Report on demonstration of former CNRP in Republic of Korea.doc (SHA-1: D1357B284C951470066AAA7A8228190B88A5C7C3) is similar to the one mentioned in the research above. It is noteworthy because it targets users interested in Cambodian politics (CNRP - Cambodian National Rescue Party, dissolved at the end of 2017). Despite the .doc extension, the document is actually in RTF format (see the figure below), contains junk code, and is also distorted.
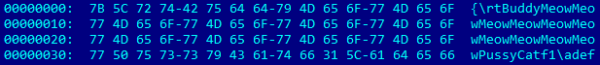
Figure 1. 'Junk' in RTF
Despite the presence of distorted elements, Word successfully opens this RTF file. As shown in Figure 2, the structure EQNOLEFILEHDR is followed by a header MTEF, and then an MTEF entry (Figure 3) for the font.
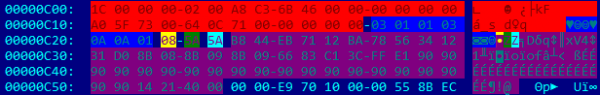
Figure 2. FONT entry values
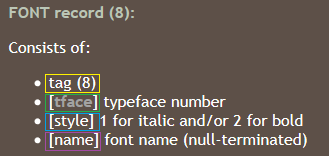
Figure 3.
Possible overflow in the field name, as its size is not checked before copying. An excessively long name triggers the vulnerability. As can be seen from the content of the RTF file (offset 0xC26 in Figure 2), the buffer is filled with shell code, followed by a dummy command (0x90) and return address. 0x402114. The address is a dialog element in EQNEDT32.exe, indicating an instruction RET. This causes the EIP to point to the beginning of the field name, containing shellcode.
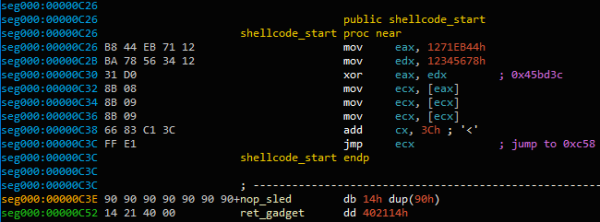
Figure 4. The beginning of the shellcode exploit
Address 0x45BD3C stores a variable that is dereferenced until it reaches the pointer to the current loaded structure MTEFData. Here resides the remainder of the shellcode.
The purpose of the shellcode is to execute the second fragment of shellcode embedded in the open document. Initially, the original shellcode attempts to find the file handle of the open document by iterating through all the handles in the system (NtQuerySystemInformation with the argument SystemExtendedHandleInformation) and checking if the PID of the handle and PID the process WinWord was the document opened with the access mask - 0x12019F.
To confirm the detection of the correct handle (and not one from another open document), the file's content is mapped using the function CreateFileMapping, and the shellcode checks if the last four bytes of the document are 'yyyy' (Egg Hunting method). Once a match is found, the document is copied to a temporary folder (GetTempPath) as ole.dll. It then reads the last 12 bytes of the document.

Figure 5. Document end markers
A 32-bit value between the markers AABBCCDD and yyyy is the offset to the next shellcode. It is invoked using the function CreateThread. The same shellcode used by the OceanLotus group earlier has been extracted. , which we released in March 2018, still works for dumping the second stage.
Second stage
Extracting components
File names and directories are chosen dynamically. The code randomly selects an executable or DLL file name in C:Windowssystem32. It then queries its resources and extracts the FileDescription for use as the folder name. If that fails, the code randomly selects a folder name from directories %ProgramFiles% or C:Windows (from GetWindowsDirectoryW). It avoids using a name that could conflict with existing files and ensures it does not contain the following words: windows, by Microsoft, desktop, system, system32 or syswow64. If the directory already exists, the name is appended with 'NLS_{6 characters}'.
The resource 0x102 is analyzed and files are dumped into %ProgramFiles% or %AppData%, in a randomly selected folder. The creation time has been changed to match that of kernel32.dll.
For example, here is a folder and a list of files created by selecting an executable file C:Windowssystem32TCPSVCS.exe as the data source.
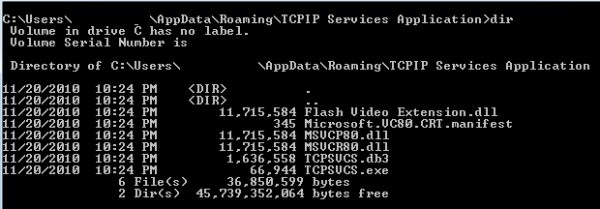
Figure 6. Extraction of various components
Resource structure 0x102 in the dropper is quite complex. In short, it contains:
— File names
— Size and contents of files
— Compression format (COMPRESSION_FORMAT_LZNT1, used by the function RtlDecompressBuffer)
The first file is dumped as TCPSVCS.exe, which is legitimate AcroTranscoder.exe (according to FileDescription, SHA-1: 2896738693A8F36CC7AD83EF1FA46F82F32BE5A3).
You may have noticed that the size of some DLL files exceeds 11 MB. This is because a large contiguous buffer of random data is embedded within the executable file. It's possible that this is a way to avoid detection by some security products.
Ensuring persistence
The resource 0x101 in the dropper contains two 32-bit integers that define how persistence should be maintained. The first value indicates how the malware will maintain persistence without administrator rights.
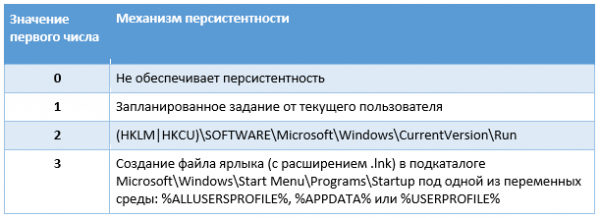
Table 1. Mechanism of persistence without administrator rights
The second integer value indicates how the malware should maintain persistence when operating with administrator rights.
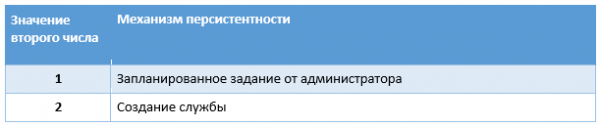
Table 2. Mechanism of persistence with administrator rights
The service name is the file name without the extension; the display name is the folder name, but if it already exists, a string 'Revision 1' is added (the number increases until an unused name is found). The operators ensured that persistence via the service is stable – in case of failure, the service should restart within 1 second. Then the value of WOW64 the new service registry key is set to 4, indicating that it is a 32-bit service.
The scheduled task is created through several COM interfaces: ITaskScheduler, ITask, ITaskTrigger, IPersistFile and ITaskScheduler. Essentially, the malware creates a hidden task, sets account information along with the current user or administrator info, and then sets the trigger.
This is a daily task with a duration of 24 hours and intervals of 10 minutes between two executions, meaning it will run continuously.
Malicious bit
In our example, the executable file TCPSVCS.exe (AcroTranscoder.exe) is legitimate software that loads DLLs that are dropped alongside it. In this case, it is of interest Flash Video Extension.dll.
Its function DLLMain simply calls another function. There are some ambiguous predicates present:
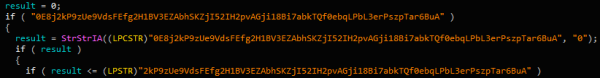
Figure 7. Ambiguous predicates
After these misleading checks, the code receives the section .text file TCPSVCS.exe, changes its protection to PAGE_EXECUTE_READWRITE and rewrites it, adding dummy instructions:
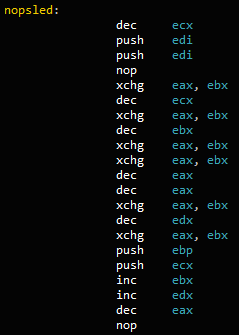
Figure 8. Sequence of instructions
At the end, an instruction is added to the function's address FLVCore::Uninitialize(void), exported Flash Video Extension.dll, adding the instruction CALL. This means that after loading the malicious DLL, when the runtime calls WinMain downward API support (simultaneously with this in TCPSVCS.exe, the instruction pointer will point to NOP, thus executing FLVCore::Uninitialize(void), the next stage.
The function simply creates a mutex starting with {181C8480-A975-411C-AB0A-630DB8B0A221}, followed by the current username. It then reads the dropped file with the *.db3 extension that contains position-independent code and uses CreateThread to execute the content.
The content of the *.db3 file is shellcode typically used by the OceanLotus group. We successfully unpacked its payload again using an emulator script that we published. .
The script extracts the final stage. This component is a backdoor that we have already analyzed in . This can be identified by the GUID {A96B020F-0000-466F-A96D-A91BBF8EAC96} of the binary file. The malware's configuration is still encrypted in the PE resource. It has roughly the same configuration, but the C&C servers differ from the previous ones:
- andreagahuvrauvin[.]com
 - byronorenstein[.]com
 - stienollmache[.]xyz
The OceanLotus group once again demonstrates a combination of different techniques to avoid detection. They have returned with an 'updated' infection process scheme. By selecting random names and filling executables with random data, they reduce the number of reliable IoCs (based on hashes and file names). Moreover, by using third-party DLL loading, the attackers only need to remove the legitimate binary AcroTranscoder.
Self-extracting archives
After RTF files, the group switched to self-extracting (SFX) archives with common document icons to further confuse the user. This was reported by Threatbook (). Upon launch, self-extracting RAR files are dropped, and DLLs with the .ocx extension are executed, the final payload of which had previously been documented {A96B020F-0000-466F-A96D-A91BBF8EAC96}.dll. Since mid-January 2019, OceanLotus has been reusing this technique but has gradually altered some configurations. In this section, we will discuss the technique and changes.
Creating a decoy
Document THICH-THONG-LAC-HANH-THAP-THIEN-VIET-NAM (1).EXE (SHA-1: AC10F5B1D5ECAB22B7B418D6E98FA18E32BBDEAB) first found in 2018. This SFX file is cleverly made – the description (Version Info) states that this is a JPEG image. The SFX script looks as follows:
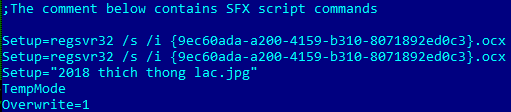
Figure 9. SFX Commands
The malware drops {9ec60ada-a200-4159-b310-8071892ed0c3}.ocx (SHA-1: EFAC23B0E6395B1178BCF7086F72344B24C04DCC), as well as an image 2018 thich thong lac.jpg.
The decoy image appears as follows:
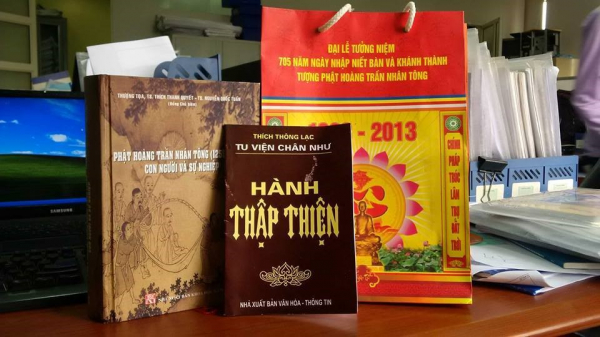
Figure 10. Decoy Image
You may have noticed that the first two lines in the SFX script call the OCX file twice, but this is not an error.
{9ec60ada-a200-4159-b310-8071892ed0c3}.ocx (ShLd.dll)
The control flow of the OCX file is very similar to other OceanLotus components – numerous command sequences JZ/JNZ and PUSH/RET, alternating with junk code.
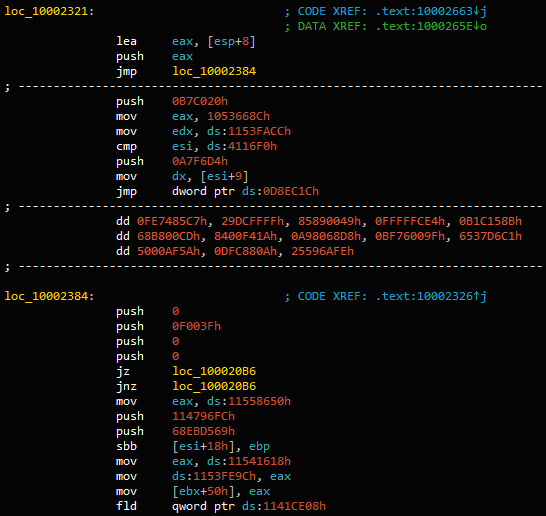
Figure 11. Obfuscated Code
After filtering the junk code, the export DllRegisterServer, called by regsvr32.exe, looks as follows:
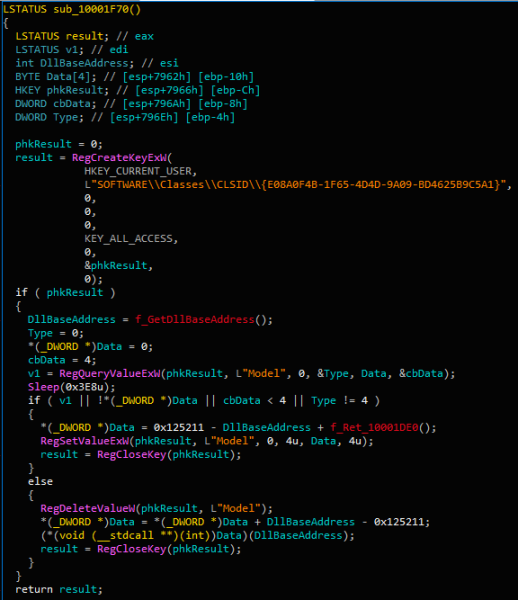
Figure 12. Main Installer Code
Essentially, on the first call, the export sets the registry value DllRegisterServer HKCUSOFTWAREClassesCLSID{E08A0F4B-1F65-4D4D-9A09-BD4625B9C5A1}Model to the encrypted offset in the DLL ( 0x10001DE0When the function is called a second time, it reads the same value and executes at that address. From there, resources are read and executed in memory.).
The shellcode is the same PE loader used in previous OceanLotus campaigns. It can be emulated using
our script db293b825dcc419ba7dc2c49fa2757ee.dll , loads it into memory, and executesDllEntry The DLL extracts the content of its resource, decrypts (AES-256-CBC), and decompresses (LZMA) it. The resource has a specific format that is easy to decompile..
Figure 13. Installer Configuration Structure (KaitaiStruct Visualizer)
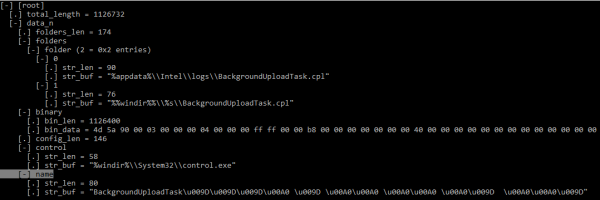
Figure 13. Installer Configuration Structure (KaitaiStruct Visualizer)
The configuration is explicitly defined – depending on the privilege level, the binary data will be written to %appdata%IntellogsBackgroundUploadTask.cpl or %windir%System32BackgroundUploadTask.cpl (or SysWOW64 for 64-bit systems).
Furthermore, persistence is ensured by creating a task named BackgroundUploadTask[junk].job, where [junk] represents a byte array 0x9D and 0xA0.
Task application name %windir%System32control.exe, and the parameter value is the path to the uploaded binary file. The hidden task is triggered every day.
Constructively, the CPL file is a DLL with the internal name ac8e06de0a6c4483af9837d96504127e.dll, which exports the function CPlApplet. This file decrypts its single resource {A96B020F-0000-466F-A96D-A91BBF8EAC96}.dll, then loads this DLL and calls its single export The DLL extracts the content of its resource, decrypts (AES-256-CBC), and decompresses (LZMA) it. The resource has a specific format that is easy to decompile..
Backdoor configuration file
The backdoor configuration is encrypted and embedded in its resources. The structure of the configuration file is very similar to the previous one.
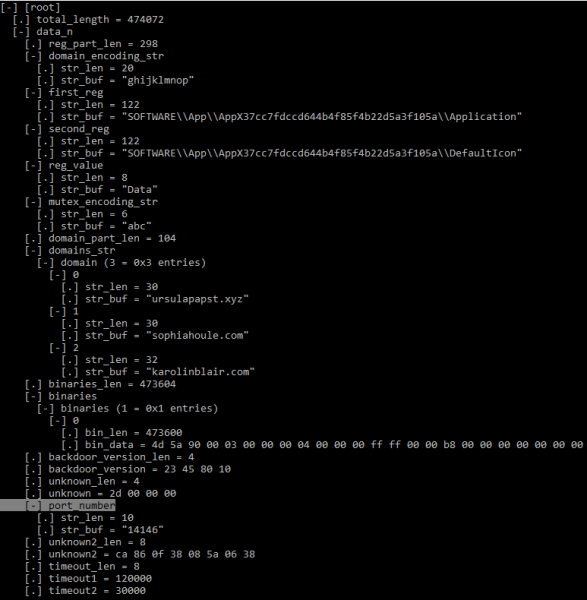
Figure 14. Backdoor configuration structure (KaitaiStruct Visualizer)
Despite the similar structure, many field values have been updated compared to the data provided in .
The first element of the binary array contains the DLL (HttpProv.dll MD5: 2559738D1BD4A999126F900C7357B759), . But since the export name was removed from the binary file, the hashes do not match.
Further investigations
While collecting samples, we noticed some characteristics. The just described sample appeared around July 2018, while others similar to it appeared recently, in mid-January to early February 2019. An SFX archive was used as a vector of infection, dropping a legitimate lure document and a malicious OSH file.
Although OceanLotus uses fake timestamps, we noticed that the timestamps of SFX and OCX files are always the same (0x57B0C36A (08/14/2016 @ 7:15pm UTC) and 0x498BE80F (02/06/2009 @ 7:34am UTC) respectively). This likely indicates that the authors have some sort of 'builder' that uses the same templates and simply changes some characteristics.
Among the documents we examined since early 2018, various titles indicate interests of the attacking countries:
— The New Contact Information Of Cambodia Media(New).xls.exe
— 李建香 (个人简历).exe (fake pdf document of a CV)
— feedback, Rally in USA from July 28-29, 2018.exe
Since the discovery of the backdoor {A96B020F-0000-466F-A96D-A91BBF8EAC96}.dll After the publication of its analysis by several researchers, we observed some changes in the configuration data of the malware.
Firstly, the authors started removing names from auxiliary DLLs (DNSprov.dll and two versions HttpProv.dll). Then, the operators stopped packing the third DLL (the second version HttpProv.dll), opting to embed only one.
Secondly, many fields in the backdoor configuration have been altered, likely to avoid detection, as many IoCs became available. Among the important fields changed by the authors are the following:
- the AppX registry section (see IoCs)
- the mutex encoding string ("def", "abc", "ghi")
- the port number
Finally, all newly analyzed versions feature new C&C, listed in the IoCs section.
Conclusions
OceanLotus continues to evolve. The cyber group is focused on refining and expanding its toolkit and lures. The authors disguise malicious payloads with attention-grabbing documents, with themes relevant to the intended victims. They are developing new schemes and also utilizing publicly available tools, such as the Equation Editor exploit. Moreover, they are improving tools to reduce the number of artifacts left on victims' machines, thereby lowering the chances of detection by antivirus software.
Indicators of Compromise
Indicators of Compromise, as well as MITRE ATT&CK attributes, are available and .
Source: habr.com
