

Several previous articles on our blog have focused on the security of personal information transmitted through messengers and social networks. Now it's time to discuss precautions regarding physical access to devices.
How to Quickly Destroy Information on a Flash Drive, HDD, or SSD
Often, it's easiest to destroy information when it’s physically present. This concerns the destruction of data from storage devices—USB flash drives, SSDs, and HDDs. You can destroy a drive in a specialized shredder or simply use something heavy, but we'll discuss more elegant solutions.
Various companies produce information carriers that come with self-destruction features right out of the box. There are numerous solutions available.
One of the simplest and most illustrative examples is the Data Killer USB flash drive and similar devices. This device looks no different from other flash drives, but inside it contains a battery. When the button is pressed, the battery destroys data on the chip through intense heating. After this, the flash drive is unrecognized upon connection, thereby destroying the chip itself. Unfortunately, detailed studies on whether it can be recovered have not been conducted.
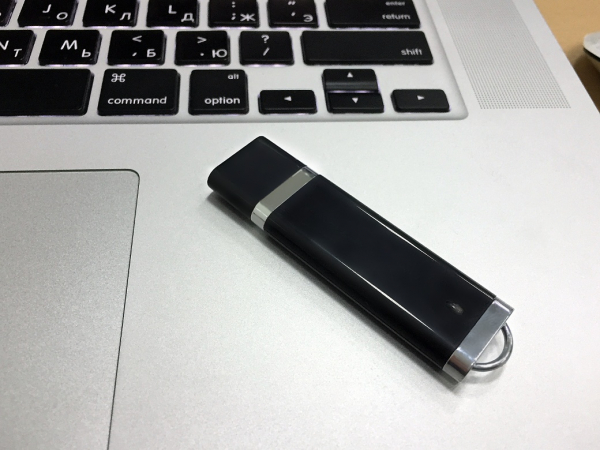
Image source:
There are flash drives that store no information but can destroy a computer or laptop. If such a 'flash drive' is placed near a laptop, and someone wishes to quickly check what's on it, it will destroy both itself and the laptop. Here is one of the .
For reliably destroying data stored on a hard drive within a PC, there are interesting systems.
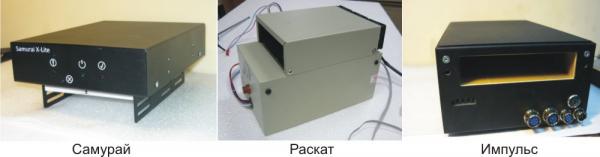
They were , but it's important to mention them. These systems are equipped with autonomous power (meaning that a power outage in the building won't help stop data destruction). There's also a timer for power disconnection, which is useful if the computer is seized in the user's absence. Even radio and GSM channels are available, allowing information destruction to be initiated remotely. The information is destroyed by the device generating a magnetic field of 450 kA/m.
This won't work for SSDs, and a thermal destruction option was once suggested for them. .
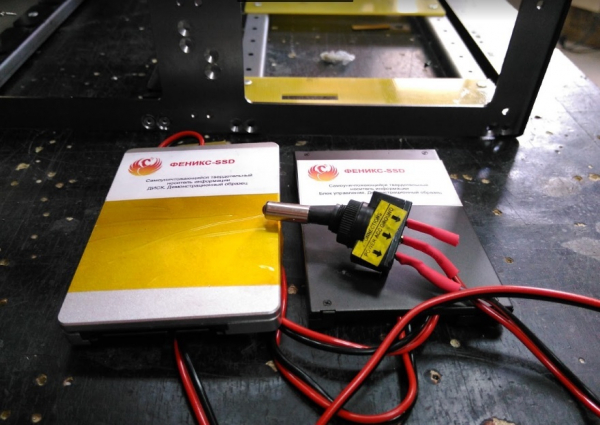
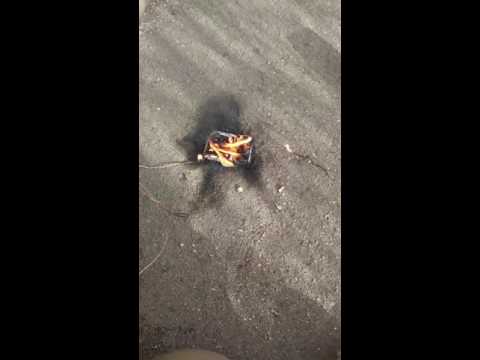
The above is a homemade method that is unreliable and dangerous. SSDs use different types of devices, such as the Impulse-SSD, which destroys the drive with a voltage of 20,000 V.

Information is erased, chips crack, and the drive becomes completely unusable. There are options for remote destruction as well (via GSM).
Mechanical HDD destroyers are also available. For instance, LG produces a device called CrushBox.
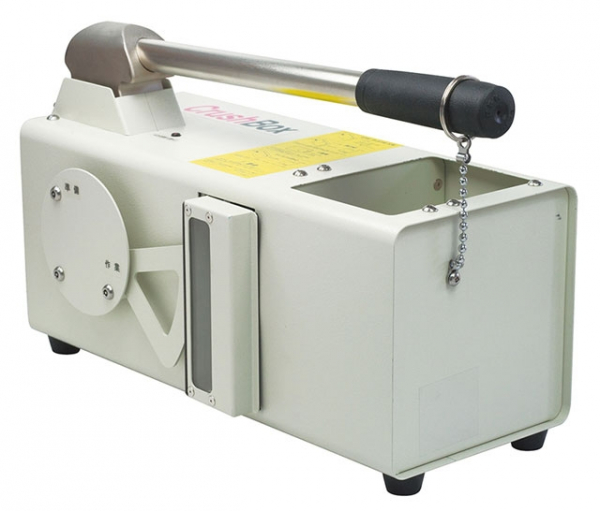
There are many gadgets for destroying HDDs and SSDs: they are produced both in Russia and abroad. We invite you to discuss such devices in the comments—many readers might have their own examples.
How to protect your PC or laptop
As with HDDs and SSDs, there are many varieties of laptop protection systems. One of the most reliable is full encryption, ensuring that data is destroyed after several unauthorized access attempts.
One of the most well-known protection systems for PCs and laptops was developed by Intel. The technology is called Anti-Theft. However, its support was discontinued several years ago, so it cannot be considered a new solution, but it serves as a good example of protection. Anti-Theft allowed users to locate a stolen or lost laptop and lock it. Intel's website stated that the system protects confidential information, blocks access to encrypted data, and prevents the OS from booting in the event of unauthorized attempts to turn on the device.
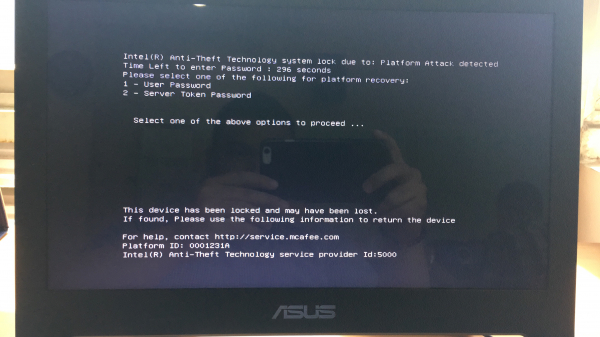
This system and similar ones check for signs of unauthorized access, such as an excessive number of login attempts, failures when trying to access previously designated servers, and locking the laptop via the internet.
Anti-Theft blocks access to the Intel system logic chip set, making it impossible to log into laptop services, run software, or boot the OS even if the HDD or SSD is replaced or reformatted. It also removes essential cryptographic files needed to access the data.
If the laptop is returned to its owner, they can quickly restore its functionality.
There is an option to use smart cards or hardware tokens — in this case, you cannot access the system without such devices. However, in our case (if there is already a knock on the door), it is necessary to install a PIN as well, so that when the key is connected, the PC prompts for an additional password. Until such a blocker is connected to the system, it is nearly impossible to start it.
A working option available now is a Python script called USBKill. It allows you to render your laptop or PC inoperable if certain boot parameters change unexpectedly. It was created by developer Hephaest0s, who published the script on GitHub.
The only requirement for USBKill to work is the necessity to encrypt the system drive of the laptop or PC, using tools such as Windows BitLocker, Apple FileVault, or Linux LUKS. There are several methods to activate USBKill, including connecting or disconnecting a flash drive.
Another option is laptops with an integrated self-destruction system. One such example was introduced in 2017 by the Russian military. To destroy the data along with the storage device, you simply need to press a button. In principle, a similar makeshift system can be created by yourself or purchased online — there are quite a few.
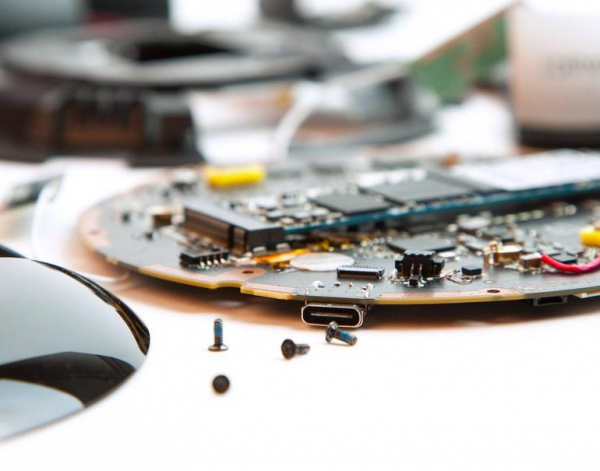
One example is , which can run various operating systems and self-destructs upon detecting an attack. However, the price is steep — $1699.
We block and encrypt data on smartphones
On iOS smartphones, there is an option to erase data in case of multiple failed authorization attempts. This feature is standard and can be enabled in the settings.
One of our employees discovered an interesting feature of iOS devices: if you need to quickly lock the iPhone, just press the power button five times in quick succession. In this case, emergency call mode is activated, and the user cannot access the device via Touch or Face ID — only with the passcode.
Android also offers various built-in personal data protection features (encryption, multi-factor authentication for different services, graphical passwords, FRP, and so on).
Among the simple hacks for blocking a phone, one suggestion is to use a fingerprint, like that of the ring finger or pinky. If someone forces the user to place their thumb on the sensor, after several attempts, the phone will be locked.
However, for iPhone and Android devices, there are software-hardware complexes that can bypass almost any protection. Apple has provided the option to disable the Lightning connector when the user is inactive for a certain period, but whether this helps against phone hacking using the mentioned complexes is unclear.
Some manufacturers produce phones that are secure against eavesdropping and hacking, but they cannot be called 100% reliable. The creator of Android, Andy Rubin, released the , which was dubbed by developers as 'the most secure.' However, it never became popular and was almost impossible to repair: if the phone broke, it was essentially deemed irreparable.
Secure phones have also been released by companies like Sirin Labs and Silent Circle. The devices were named Solarin and Blackphone. Boeing created Boeing Black — a device recommended for employees of defense agencies. This gadget has a self-destruct mode that activates in case of a breach.
Nevertheless, regarding smartphones, the situation in terms of protection against unauthorized access is somewhat worse than with information carriers or laptops. The only recommendation is not to use smartphones for exchanging or storing sensitive information.
What about in public places?
Up to now, we have discussed how to quickly destroy information if someone knocks at the door and you weren’t expecting guests. But there are also public places — cafes, fast-food restaurants, the street. If someone approaches from behind and takes your laptop, data destruction systems won't help. No matter how many secret buttons there are, you won't be able to press them with your hands tied.
The simplest solution is to avoid taking devices with critical information outside at all. If you must bring them, do not unlock the device in crowded places unless absolutely necessary. At that moment, a gadget can easily be intercepted while you're in a crowd.
The more devices you have, the easier it is to intercept something. Therefore, instead of the combination of 'smartphone + laptop + tablet', it’s better to use only a netbook, for example, with Linux on board. You can make calls with it, and securing information on one device is easier than on three.
In public places like a café, choose a spot with a wide field of view and ideally sit with your back to the wall. This way, you can see everyone approaching. In a suspicious situation, lock your laptop or phone and wait to see what happens.
You can set up lock functions for different operating systems, and it's easiest to do it by pressing a specific key combination (for Windows, it's the Windows key + L, which you can press in a fraction of a second). For macOS, it's Command + Control + Q. It’s also quick to press, especially if you practice.
Of course, in unforeseen situations, you might miss it, so another option is to lock the device by pressing any several keys at the same time (like hitting the keyboard with your fist, for example). If you know of an application that does this for macOS, Windows, or Linux—please share the link.
The MacBook also has a gyroscope. You can consider a scenario where the laptop locks when it is lifted, or when there is a sudden quick change in its position, as detected by the built-in gyroscopic sensor.
We haven’t found a suitable utility, but if someone knows about such applications, please share them in the comments. If there aren’t any, we suggest writing a utility, and we will reward the author with a multi-year to our VPN (depending on its complexity and functionality) and assist in the distribution of the utility.
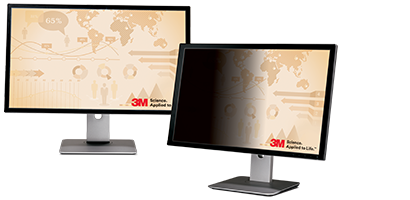
Another option is to shield your screen (laptop, phone, tablet) from prying eyes. Privacy filters—special films that darken the display when the viewing angle changes—are perfect for this. You can only see what the user is doing from behind.
By the way, here's a simple life hack for the current situation: if you're at home and someone is knocking or ringing the bell (like a courier delivering pizza, for example), it's better to block the gadgets. Just in case.
You can protect yourself from 'Major Friend', meaning an unexpected attempt by an external party to access personal data, but it’s complex. If you have your own cases to share, we’re looking forward to examples in the comments.
Source: habr.com
