

In 2019, the consulting company Miercom conducted an independent technology assessment of the Cisco Catalyst 9800 Series Wi-Fi 6 controllers. A testbed was assembled from controllers and Wi-Fi 6 access points from Cisco for this study, and the technical solution was evaluated in the following categories:
- Availability;
- Security;
- Automation.
The results of the study are presented below. Since 2019, the functionality of the Cisco Catalyst 9800 Series controllers has been significantly improved—these points are also reflected in this article.
You can read about other advantages of the Wi-Fi 6 technology, implementation examples, and application areas.
Solution Overview
Cisco Catalyst 9800 Series Wi-Fi 6 Controllers
The Cisco Catalyst 9800 Series wireless controllers, based on the IOS-XE operating system (which is also used for Cisco switches and routers), are offered in various options.
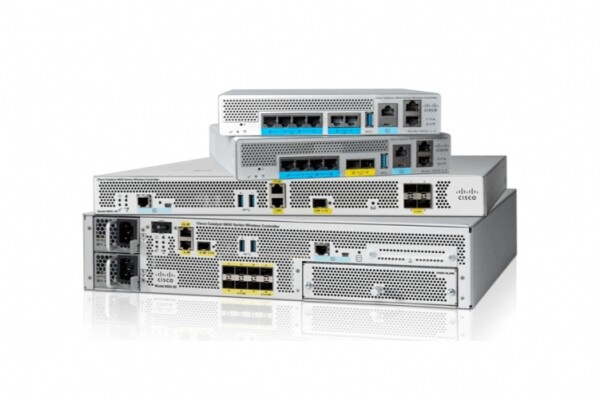
The high-end model 9800-80 supports wireless network throughput of up to 80 Gbps. One 9800-80 controller supports up to 6000 access points and up to 64,000 wireless clients.
The mid-range model—the 9800-40 controller—supports throughput of up to 40 Gbps, up to 2000 access points, and up to 32,000 wireless clients.
In addition to these models, the wireless controller 9800-CL (CL stands for Cloud) was also included in the competitive analysis. The 9800-CL model operates in virtual environments on VMWare ESXI and KVM hypervisors, and its specifications depend on the allocated hardware resources for the controller's virtual machine. In the maximum configuration, the Cisco 9800-CL controller, like the high-end model 9800-80, supports scalability for up to 6000 access points and up to 64,000 wireless clients.
During the study, Cisco Aironet AP 4800 Series access points were used with support for operation at 2.4 and 5 GHz frequencies, with the ability to dynamically switch to dual 5-GHz mode.
Test Stand
The test setup consisted of two Cisco Catalyst 9800-CL wireless controllers operating in a cluster, along with Cisco Aironet AP 4800 Series access points.
Client devices included laptops from Dell and Apple, as well as an Apple iPhone smartphone.
Availability testing
Availability is defined as the ability of users to access a system or service and utilize them. High availability implies continuous access to a system or service, regardless of specific events.
High availability has been tested in four scenarios, the first three scenarios being predictable or planned events that can occur during operational or non-operational hours. The fifth scenario is a classic failure, which is an unpredictable event.
Description of scenarios:
- Bug fix – a micro-update of the system (bugfix or security patch) that allows correcting a specific error or vulnerability without a complete system software update;
- Functional update – adding or extending current functionality of the system by installing functional updates;
- Full update – updating the controller's software image;
- Adding an access point – introducing a new model of access point into the wireless network without the need to reconfigure or update the wireless controller software;
- Failure – a malfunction of the wireless controller.
Bug fixes and vulnerabilities
Often in many competitive solutions, installing patches requires a complete update of the wireless controller system software, which can lead to unplanned downtimes. In the case of Cisco solutions, patches can be applied without interrupting productivity. Patches can be installed on any of the components while the wireless infrastructure continues to operate.
The procedure itself is quite simple. The patch file is copied to the boot folder on one of the Cisco wireless controllers, and then the operation is confirmed through the graphical interface or command line. Additionally, the patch can also be undone and removed through the graphical interface or command line, again without interrupting system operation.
Functional update
Functional software updates are applied to activate new features. One such enhancement is the update of application signature databases. This package was installed on Cisco controllers as a test. Similar to fixes, feature updates can be applied, installed, or removed without downtime or interruption of system operations.
Full Update
Currently, a full update of the controller's software image is performed just like a functional update, that is, without downtime. However, this capability is only available in a clustered configuration, where there is more than one controller. The full update is carried out sequentially: first on one controller, then on the second.
Adding a New Access Point Model
Connecting new access points that have not previously been used with the software image of the controller to the wireless network is a fairly common operation, especially in large networks (airports, hotels, manufacturing). Quite often, in competitors' solutions, this operation requires a firmware update or a reboot of the controllers.
When connecting new Wi-Fi 6 access points to the Cisco Catalyst 9800 series controller cluster, such problems are not observed. Connecting new access points to the controller is done without upgrading the controller's software, and this process does not require a reboot, thus not affecting the wireless network in any way.
Controller Failure
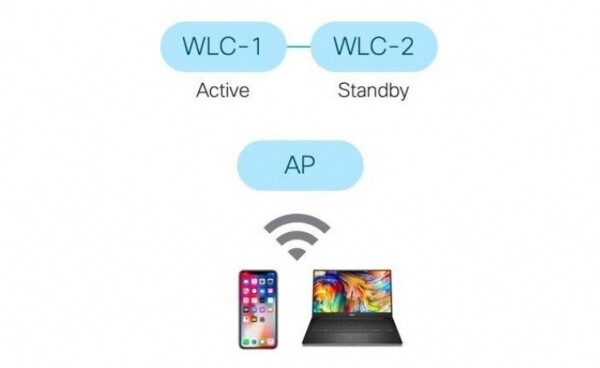
In the testing environment, there are two controllers (Active / Standby) for Wi-Fi 6, and the access point has a direct connection to both controllers.
One wireless controller is active, while the other is, accordingly, standby. In the event of an active controller failure, control is taken over by the standby controller, and its status changes to active. This procedure occurs without interruption for the access point and Wi-Fi for clients.
Security
This section discusses aspects of security, which is an extremely relevant task in wireless networks. The solution's security is evaluated based on the following characteristics:
- Application recognition;
- Traffic flow tracking;
- Encrypted traffic analysis;
- Intrusion detection and prevention;
- Authentication methods;
- Client device protection.
Application recognition
Among the variety of products in the corporate and industrial Wi-Fi market, there are differences in how well products identify traffic by applications. Products from different manufacturers may identify a different number of applications. Moreover, many of the applications listed by competing solutions as identifiable are essentially websites rather than unique applications.
There is another interesting feature of application recognition: solutions vary significantly in identification accuracy.
Considering all the tests conducted, it can be confidently stated that Cisco's Wi-Fi 6 application recognition performs exceptionally well: Jabber, Netflix, Dropbox, YouTube, and other popular applications, as well as web services, were accurately identified. Cisco solutions can also dive deeper into data packets using DPI (Deep Packet Inspection).
Traffic flow tracking
Another test was conducted to determine if the system could accurately track and report on data flows (e.g., the movement of large files). To check this, a file of 6.5 megabytes was sent over the network using the File Transfer Protocol (FTP).
Cisco's solution fully accomplished the task and was able to track this traffic thanks to NetFlow and its hardware capabilities. The traffic was detected and identified immediately with the exact volume of data transmitted.
Analysis of encrypted traffic
User data traffic is increasingly being encrypted. This is done to protect it from tracking or interception by malicious actors. However, at the same time, hackers are increasingly using encryption to hide their malicious software and conduct other dubious operations, such as Man-in-the-Middle (MiTM) attacks or keylogging attacks.
Most enterprises inspect a portion of encrypted traffic, first decrypting it using firewalls or intrusion prevention systems. However, this process is time-consuming and does not benefit overall network performance. Additionally, once decrypted, this data becomes vulnerable to prying eyes.
Cisco Catalyst 9800 series controllers effectively tackle the challenge of analyzing encrypted traffic by other means. This solution is called Encrypted Traffic Analytics (ETA). ETA is a technology unparalleled by competing solutions currently available, which detects malware in encrypted traffic without the need for decryption. ETA is a core function of IOS-XE, incorporating Enhanced NetFlow and utilizing advanced behavioral algorithms to identify malicious traffic patterns hidden within encrypted data.
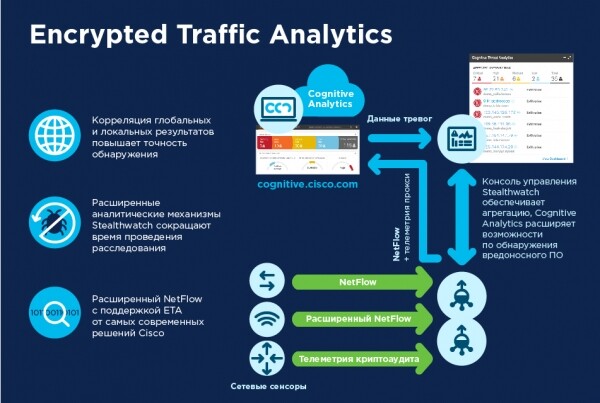
ETA does not decrypt messages but gathers metadata profiles of encrypted traffic streams—packet sizes, time intervals between packets, and much more. This metadata is then exported in NetFlow v9 records to Cisco Stealthwatch.
A key feature of Stealthwatch is the continuous monitoring of traffic, as well as the establishment of baseline metrics for normal network activity. Using the metadata from the encrypted flow sent to it by ETA, Stealthwatch employs multi-layered machine learning to detect behavioral anomalies that may indicate suspicious events.
Last year, Cisco engaged Miercom for an independent evaluation of the Cisco Encrypted Traffic Analytics solution. During this assessment, Miercom separately sent known and unknown threats (viruses, trojans, ransomware) in both encrypted and unencrypted traffic through large ETA and non-ETA networks to identify threats.
Malicious code was executed for testing in both networks. In both cases, suspicious activity was progressively detected. In the ETA network, threats were identified 36% faster in the initial stages than in the non-ETA network. Moreover, as the process continued, the detection productivity in the ETA network increased. Ultimately, after several hours of operation in the ETA network, two-thirds of active threats were successfully detected, which is twice the figure in the non-ETA network.
The functionality of ETA integrates well with Stealthwatch. Threats are ranked by severity, displayed with detailed information, as well as remediation options after confirmation. The conclusion is—ETA works!
Intrusion detection and prevention
Cisco now has another effective tool for enhancing security — Cisco Advanced Wireless Intrusion Prevention System (aWIPS): a mechanism for detecting and preventing threats to wireless networks. The aWIPS solution operates at the level of controllers, access points, and the Cisco DNA Center management software. The process of threat detection, alerting, and prevention combines network traffic analysis, information about network devices and topology, signature-based methods, and anomaly detection, which ultimately ensures high accuracy and prevention of wireless network threats.
The full integration of aWIPS into the network infrastructure allows for continuous monitoring of wireless traffic in both wired and wireless networks and utilizes it for automatic analysis of potential attacks from various sources to comprehensively identify and prevent possible attacks.
Authentication methods
Currently, in addition to classical authentication methods, Cisco Catalyst series 9800 solutions support WPA3. WPA3 is the latest version of WPA, comprising a set of protocols and technologies that provide authentication and encryption for Wi-Fi networks.
WPA3 uses the Simultaneous Authentication of Equals (SAE) method to provide the most reliable protection for users against password-guessing attempts by third parties. When a client connects to an access point, they perform an SAE exchange. If successful, each will generate a cryptographically secure key, from which a session key will be derived, after which they enter a confirmation state. After this, the client and access point can enter confirmation states whenever a session key needs to be generated. The method uses forward secrecy, where an attacker can compromise one key but not all others.
This means that SAE is constructed in such a way that an attacker intercepting the traffic has only one chance to guess the password before the captured data becomes useless. To organize prolonged password guessing, physical access to the access point would be required.
Client device protection methods
The primary means of protecting clients in Cisco Catalyst 9800 series wireless solutions is currently Cisco Umbrella WLAN — a cloud-based network security service operating at the DNS level with automatic detection of both known and new threats.
Cisco Umbrella WLAN provides client devices with secure internet connectivity. This is achieved through content filtering, which blocks access to resources on the internet in accordance with enterprise policies. Consequently, this protects client devices online from malware, ransomware, and phishing. The application of policies is based on 60 continuously updated content categories.
Automation
Modern wireless networks are much more flexible and complex, which makes traditional methods of configuring and retrieving information from wireless controllers insufficient. Network administrators and information security specialists require automation and analytics tools, prompting wireless network solution providers to offer such tools.
To address these challenges, Cisco Catalyst 9800 series wireless controllers support RESTCONF / NETCONF network configuration protocol alongside traditional APIs, utilizing the YANG (Yet Another Next Generation) data modeling language.
NETCONF is an XML-based protocol that applications can use to request information and change the configuration of network devices such as wireless controllers.
In addition to these methods, Cisco Catalyst 9800 series controllers have implemented the capability to obtain, sample, and analyze data about information flow using the NetFlow and sFlow protocols.
To ensure security and to model traffic, the ability to track specific streams is a valuable tool. To address this task, the sFlow protocol has been implemented, which allows capturing two packets out of every hundred. However, this may sometimes be insufficient for analysis and adequate study and evaluation of the flow. Therefore, an alternative is NetFlow, developed by Cisco, which allows 100% collection and export of all packets in a given flow for subsequent analysis.
Another feature, though only available in the hardware implementation of controllers, that automates the operation of the wireless network in Cisco Catalyst 9800 series controllers is the built-in support for Python as an extension for using scripts directly on the wireless controller.
Finally, for monitoring and management operations in the Cisco Catalyst 9800 series controllers, the time-tested SNMP protocol versions 1, 2, and 3 is supported.
Thus, in terms of automation, the Cisco Catalyst 9800 series solutions fully meet modern business requirements, offering both new and unique as well as proven tools for automated operations and analytics in wireless networks of any size and complexity.
Conclusion
In the solutions based on Cisco Catalyst 9800 series controllers, Cisco has demonstrated outstanding results in categories: high availability, security, and automation.
The solution fully meets all high availability requirements, such as failover in less than a second during unplanned events and zero downtime for planned events.
The Cisco Catalyst 9800 series controllers implement comprehensive security, providing deep packet inspection for application recognition and management, total visibility of data streams, and threat identification hidden in encrypted traffic, as well as advanced mechanisms for client device authentication and protection.
To automate operations and analytics, Cisco Catalyst 9800 series solutions have extensive capabilities, utilizing popular standard models: YANG, NETCONF, RESTCONF, traditional APIs, and built-in Python scripts.
Thus, Cisco once again reaffirms its status as a leading global provider of networking solutions, keeping pace with the times and addressing all the challenges of modern business.
You can learn more about the Catalyst switch family information at Cisco.
Source: habr.com
