

Welcome! Today we will discuss how to perform the initial setup of the mail gateway. – solutions from Fortinet for email protection. In this article, we will examine the layout we will be working with, and perform the configuration. , necessary for receiving and checking emails, and we will also test its functionality. Based on our experience, we can confidently say that the process is very simple, and even after minimal configuration, results can be observed.
Let's start with the current layout. It is presented in the figure below.
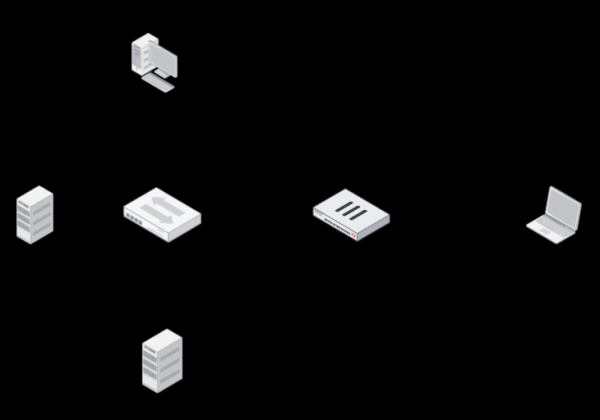
On the right, we see the computer of an external user from whom we will send mail to a user in the internal network. In the internal network, there is a user computer, a domain controller running a DNS server, and a mail server. At the network boundary is the firewall – FortiGate, whose main feature is the configuration of SMTP and DNS traffic forwarding.
We will pay special attention to DNS.
Two DNS records are used for routing emails on the Internet – an A record and an MX record. Usually, these DNS records are configured on a public DNS server, but due to layout constraints, we simply forward DNS through the firewall (that is, for the external user, the DNS server address is set to 10.10.30.210).
An MX record is a record that contains the name of the mail server servicing the domain and the priority of this mail server. In our case, it looks like this: test.local -> mail.test.local 10.
An A record is a record that translates a domain name into an IP address; in our case, it is: mail.test.local -> 10.10.30.210.
When our external user tries to send an email to the address an@test.local, they will request the MX record of the domain test.local from their DNS server. Our DNS server will respond with the name of the mail server – mail.test.local. Now the user needs to obtain the IP address of this server, so they again query DNS for the A record and receive the IP address 10.10.30.210 (yes, again this one :) ). They can send the email. Thus, they attempt to establish a connection to the obtained IP address on port 25. Through the rules on the firewall, this connection is forwarded to the mail server.
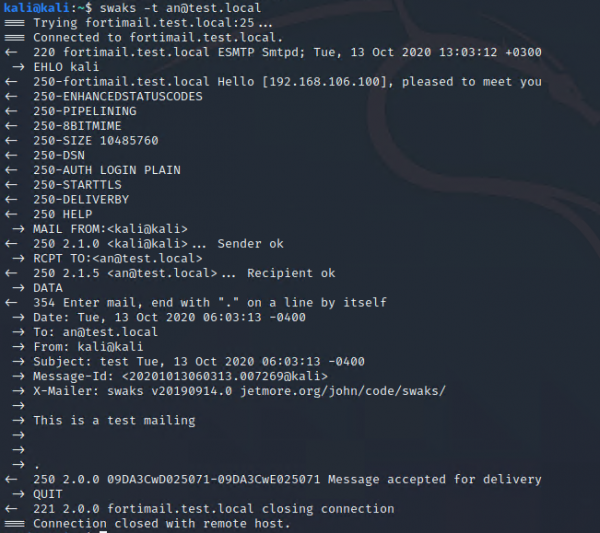
Let's check the functionality of the mail in its current layout state. For this, we will use the swaks utility on an external user's computer. This tool allows us to test SMTP functionality by sending a message to a recipient with a set of various parameters. Previously, a user with the mailbox an@test.local has already been set up on the mail server. Let's try sending him an email:
Now let's move to the internal user's machine and confirm that the email has arrived:
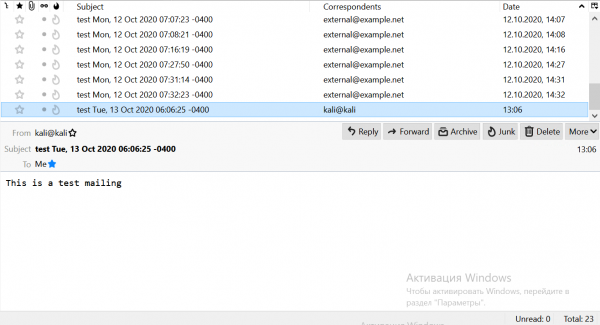
The email has indeed arrived (it's highlighted in the list). This means that the layout is functioning correctly. It's time to turn to FortiMail. Let's add to our layout:
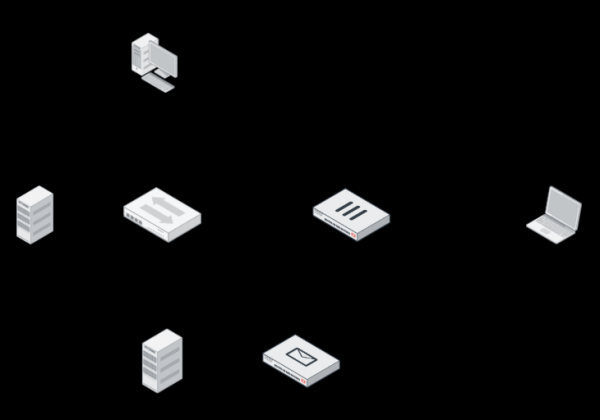
FortiMail can be deployed in three modes:
- Gateway — acts as a full MTA: it receives all mail, checks it, and then forwards it to the mail server;
- Transparent — or, in other words, transparent mode. It is installed in front of the server and checks incoming and outgoing mail. After that, it forwards it to the server. It does not require any changes to the network configuration.
- Server — in this case, FortiMail serves as a full mail server with the ability to create mailboxes, receive and send mail, as well as other functionalities.
We will deploy FortiMail in Gateway mode. Let's access the virtual machine settings. Login is admin, and there is no password set. Upon first login, you need to set a new password.
Now let's configure the virtual machine for access to the web interface. The machine also needs to have internet access. Let's set up the interface. We only need port1 for this. This will be used to connect to the web interface, and it will also be used for internet access. Internet access is required for updating services (such as antivirus signatures, etc.). For the configuration, enter the following commands:
config system interface
edit port 1
set ip 192.168.1.40 255.255.255.0
set allowaccess https http ssh ping
end
Now let's set up routing. For this, you need to enter the following commands:
config system route
edit 1
set gateway 192.168.1.1
set interface port1
end
While entering commands, you can use the tab key to avoid typing them fully. Also, if you forget what command should come next, you can use the "?" key.
Now let's check the internet connection. To do this, we'll ping Google's DNS:
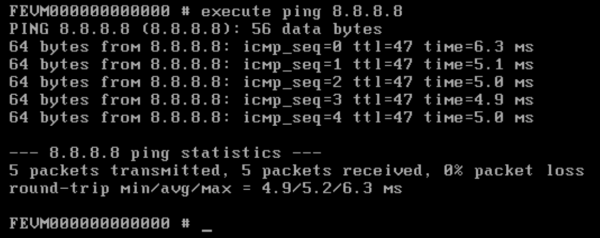
As we can see, the Internet is now available. The initial settings typical for all Fortinet devices have been completed, and we can now proceed to configuration through the web interface. To do this, we will open the management page:
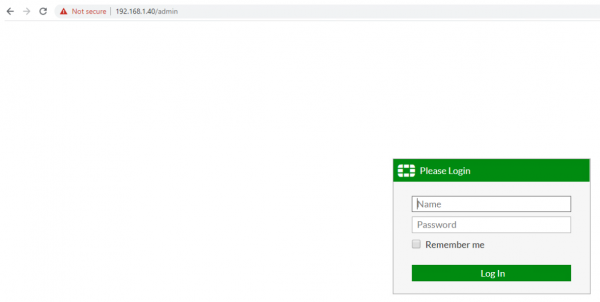
Note that you need to go to the link in the format /admin. Otherwise, you won't be able to access the management page. By default, the page is in standard configuration mode. For settings, we will need Advanced mode. Let's go to the menu admin->View and switch the mode to Advanced:
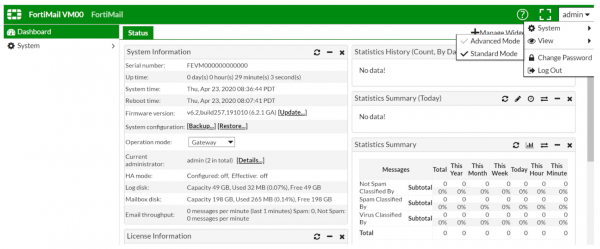
Now we need to upload a trial license. This can be done in the menu License Information → VM → Update:
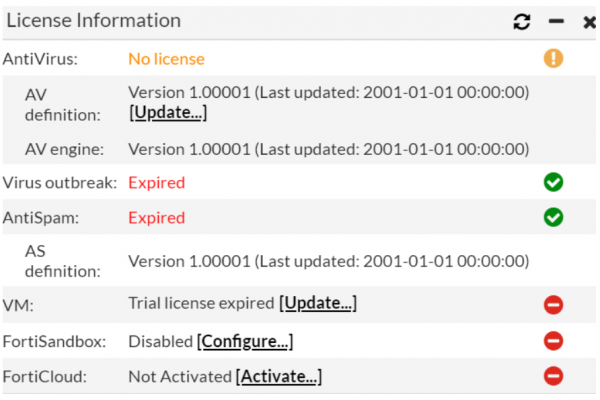
If you don't have a trial license, you can request one by contacting .
After entering the license, the device should reboot. Subsequently, it will start pulling updates for its databases from the servers. If this does not happen automatically, you can go to the menu System → FortiGuard and in the Antivirus and Antispam tabs, click the Update Now button.
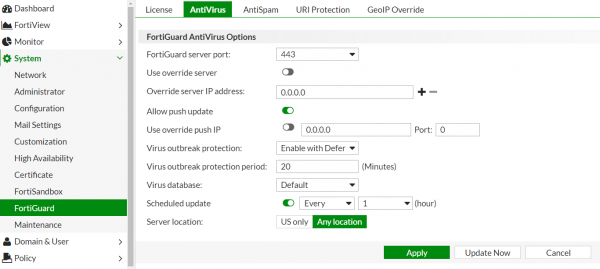
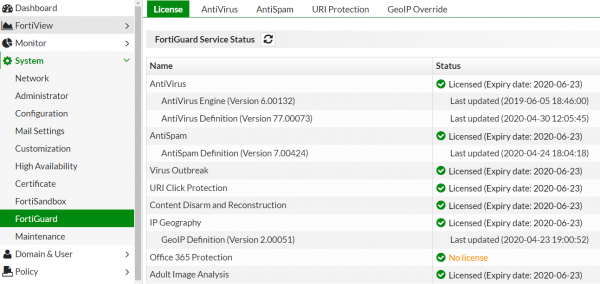
If this doesn't help, you can change the ports used for updates. Usually, after this, all licenses will appear. In the end, it should look like this:
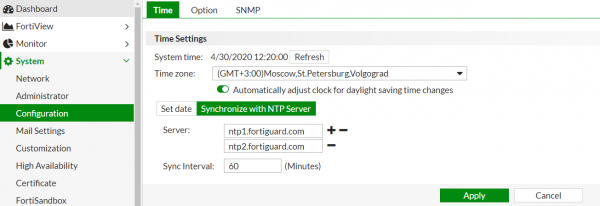
Let's configure the correct time zone, which will be useful when examining the logs. For this, we will go to the menu System → Configuration:
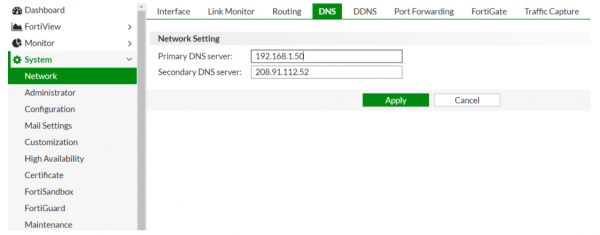
We will also configure the DNS. We will set up an internal DNS server as the primary DNS server, and we will leave the Fortinet-provided DNS server as the backup.
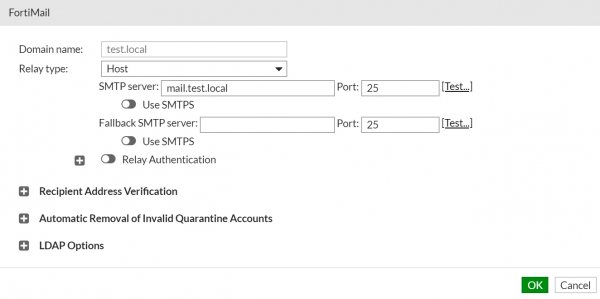
Now let's move on to the most interesting part. As you may have noticed, the device is set to Gateway mode by default. Therefore, we don't need to change it. We'll go to the Domain & User → Domain field. We'll create a new domain that needs protection. Here, we need to specify only the domain name and the mail server address (you can also specify its domain name; in our case, it's mail.test.local):
Now we need to specify a name for our mail gateway. This will be used in the MX and A records that we will need to change later:
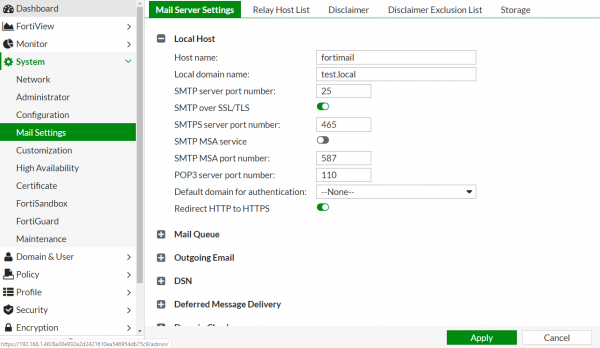
The Host Name and Local Domain Name segments combine to form the FQDN, which is used in DNS records. In our case, the FQDN = fortimail.test.local.
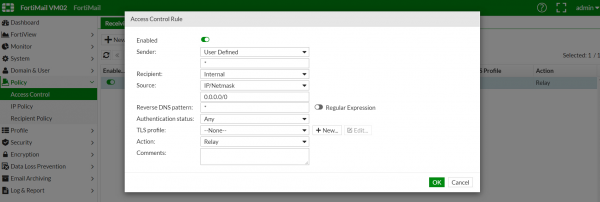
Now let's configure the receiving rule. We need all emails coming from outside and assigned to a user in the domain to be forwarded to the mail server. To do this, we will go to the Policy → Access Control menu. An example of the setup is shown below:
Let's take a look at the Recipient Policy tab. Here you can set specific rules for verifying emails: if mail comes from the domain example1.com, it needs to be verified using mechanisms specifically configured for that domain. There is already a default rule set for all mail, and at this moment it suits our needs. You can see this rule in the image below:
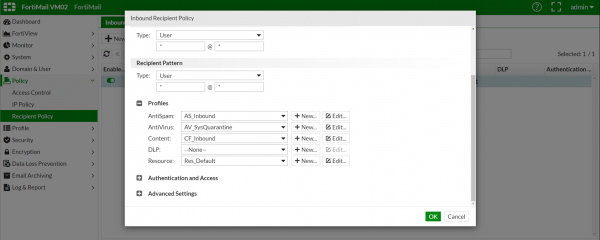
With this, the configuration on FortiMail can be considered complete. In fact, there are many more parameters, but if we start discussing them all, we could write a book :) Our goal is to launch FortiMail in test mode with minimal effort.
There are two things left — to change the MX and A records, as well as modify the port forwarding rules on the firewall.
The MX record test.local -> mail.test.local 10 needs to be changed to test.local -> fortimail.test.local 10. However, usually during pilots, a second MX record with a higher priority is added. For example:
test.local -> mail.test.local 10
test.local -> fortimail.test.local 5
I remind you that the lower the preference number of the mail server in the MX record, the higher its priority.
The A record cannot be changed, so we will simply create a new one: fortimail.test.local -> 10.10.30.210. The external user will access the address 10.10.30.210 on port 25, and the firewall will forward the connection to FortiMail.
To change the forwarding rule on FortiGate, you need to modify the address in the corresponding Virtual IP object:
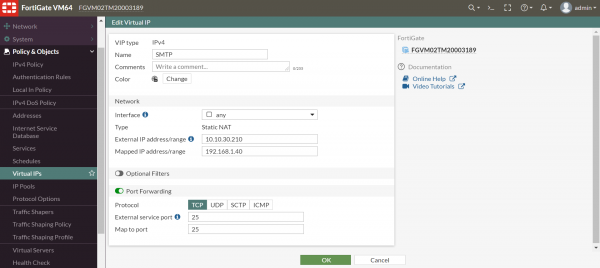
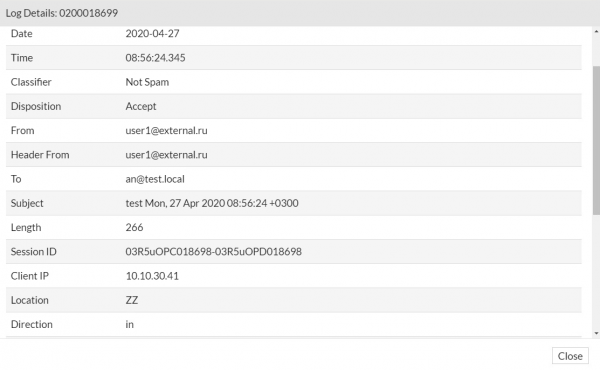
Everything is ready. Let's check. We will again send an email from the external user's computer. Now let's go to FortiMail in the Monitor → Logs menu. In the History field, you can see an entry indicating that the email was received. For additional information, you can right-click on the entry and select Details:
To complete the picture, let's check if FortiMail in its current configuration can block emails containing spam and viruses. To do this, we will send a test virus eicar and a test email found in one of the spam email databases (http://untroubled.org/spam/). After that, we will go back to the log viewing menu:

As we can see, both spam and virus-laden emails were successfully identified.
This configuration is sufficient to provide basic protection against viruses and spam. However, FortiMail's functionality does not stop there. For more effective protection, it is necessary to examine the available mechanisms and tailor them to your needs. In the future, we plan to cover other, more advanced features of this email gateway.
If you have encountered difficulties or have questions about the solution, please write them in the comments, and we will try to respond promptly.
You can submit a request for a trial license to test the solution .
Author: Alexey Nikulin. Information Security Engineer at Fortiservice.
Source: habr.com
