

And no one pours young wine into old skins; otherwise, the young wine will burst the skins, and the wine will be spilled, and the skins will be destroyed; but new wine must be poured into new skins; then both are preserved. Luke 5:37,38
In April of this year, the administration of the largest DC hub in the world announced the start of support for secure connections. Let's see what came of it.
Freedom of conscience
Since everything I thought about this has already been said , this part of the article shouldn't even exist.
If you need security, choose a modern client and . Point.
But what if we use an NMDC hub, that is, a regular? В этом случае придётся столкнуться с несовместимостью старых, очень старых, новых или просто ненастроенных DC клиентов. Но – это было сделано, и проблемы не заставили себя ждать.
Mafia
First, secure 'client-client' connections are established regardless of the presence of 'client-hub' encryption.
Second, it is impossible to visually determine a hub that does or does not relay requests for secure connections.
Third, to date, nearly all DC clients have connection encryption enabled by default.
Remember? Now let's the TLS settings on the user side, connect to the hub, and carefully try to connect clients to each other.
NMDCs hub
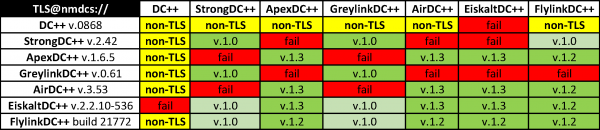
DC++ categorically rejects secure connections on NMDC hubs, but fully approves of regular ones. The reason has been stated by the developers multiple times – there’s no need to keep walking on old rakes!
StrongDC++ only supports TLS v.1.0, and modern clients do not connect to it at all. GreylinkDC++ is even worse.
FlylinkDC++ willingly falls into compatibility mode with older clients. But for how long and is it even necessary?..
EiskaltDC++ does the same, but less willingly, only for its own needs.
ADC hub(s)
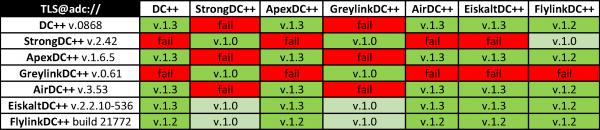
It's exactly the same, but DC++ is actively getting involved.
EiskaltDC++ seems to make no distinction between NMDC and ADC hubs, strict with both.
And what if we filter out outdated clients by requiring TLS v.1.2 support at the entrance?..
ADC hub(s)

Magnificent, isn’t it?
Conclusions
The reader may think that it’s best to use FlylinkDC++ and have no problems, but what you forget is that this client in itself. One of the latest incidents I'm aware of – the inability to set the checkbox for supporting secure connections for many users via remote config, and the actual absence of it in all earlier versions.
Therefore, due to numerous historical and political reasons, using NMDC hubs as a basis for secure interclient connections is complicated or even impossible. By using an NMDC hub, you are guaranteed to lose the ability to connect with a portion of users, while gaining security – but without guarantees.
Recommendations
Start using ADC hubs, even if only as a trial. Discard outdated clients, and if you are an admin of a DC hub, ban Strong and Gray on your server. For behold,
Every kingdom divided against itself will be brought to desolation, and every city or house divided against itself will not stand. Matt. 12:25
Source: habr.com
