

Graudit supports multiple programming languages and allows integrating security testing of the codebase directly into the development process.
Source: (Markus Spiske)
Testing is an essential part of the software development lifecycle. There are many types of testing, each addressing its specific task. Today, I want to talk about identifying security issues in code.
It is evident that in today's software development landscape, ensuring the security of processes is crucial. At one time, a specific term, DevSecOps, was even introduced. This term refers to a set of procedures aimed at detecting and mitigating vulnerabilities in applications. There are specialized open-source solutions for checking vulnerabilities in accordance with the OWASP standards. , which describe various types and behaviors of vulnerabilities in source code.
There are different approaches to solving security issues, such as Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), Interactive Application Security Testing (IAST), Software Composition Analysis, and so on.
Static Application Security Testing identifies errors in the already written code. This approach does not require the application to be running, which is why it is called static analysis.
I will focus on static code analysis and use a simple open-source tool to demonstrate everything practically.
Why I Chose an Open Source Tool for Static Security Code Analysis
There are several reasons for this: firstly, it is free, as you are using a tool developed by a community of like-minded individuals who want to assist other developers. If you have a small team or a startup, you have an excellent opportunity to save money by using open-source software to check the security of your codebase. Secondly, it frees you from the need to hire a separate DevSecOps team, further reducing your expenses.
Good open source tools are always created with heightened flexibility in mind. As a result, they can be used in virtually any environment, covering a wide range of tasks. Developers find it much easier to integrate such tools with the system they have already built while working on their projects.
However, there may be situations where you require a feature that is not available in your chosen tool. In this case, you have the option to fork its code and develop your own tool based on it with the functionality you need.
Since the development of open source software is heavily influenced by the community in most cases, decisions about making changes are usually made quickly and effectively: developers of the open source project rely on feedback and suggestions from users, as well as their reports of found bugs and other issues.
Using Graudit to analyze code security
For static code analysis, various open source tools can be utilized, but there is no universal tool for all programming languages. Developers of some of them follow OWASP guidelines and strive to encompass as many languages as possible.
Here we will be using , a simple command-line utility that allows us to find vulnerabilities in our codebase. It supports various languages, although the range is still limited. Graudit is based on the command-line utility grep, which was originally released under the GNU license.
There are similar tools for static code analysis — Rough Auditing Tool for Security (RATS), Securitycompass Web Application Analysis Tool (SWAAT), flawfinder, and others. However, Graudit is highly flexible and has minimal technical requirements. Nonetheless, you may encounter tasks that Graudit is unable to handle. In that case, you can look for other options here .
We can integrate this tool into a specific project or make it available to a selected user, or use it simultaneously across all our projects. This also demonstrates the flexibility of Graudit. So, let's first clone the repository:
$ git clone https://github.com/wireghoul/grauditNow let's create a symbolic link for Graudit to use it in command format.
$ cd ~/bin && mkdir graudit
$ ln --symbolic ~/graudit/graudit ~/bin/graudit
Let's add an alias to .bashrc (or another configuration file you use):
#------ .bashrc ------
alias graudit="~/bin/graudit"
Reloading:
$ source ~/.bashrc # OR
$ exec $SHELL
Let's check if the installation was successful:
$ graudit -hIf you see something like this, everything is good.
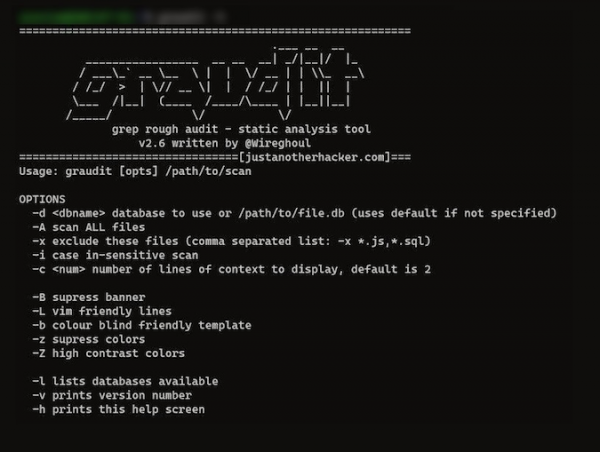
I will test one of my existing projects. Before running the tool, it needs to be provided with a database corresponding to the language in which my project is written. The databases are located in the ~/gradit/signatures folder:
$ graudit -d ~/gradit/signatures/js.dbSo, I tested two JS files from my project, and Graudit printed information about vulnerabilities in my code to the console:
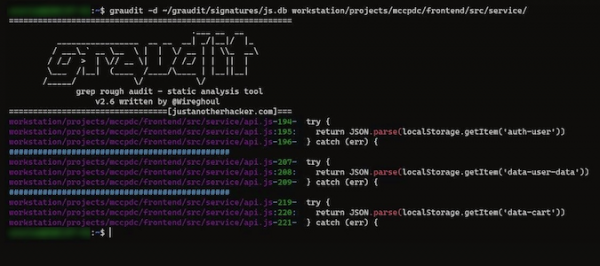
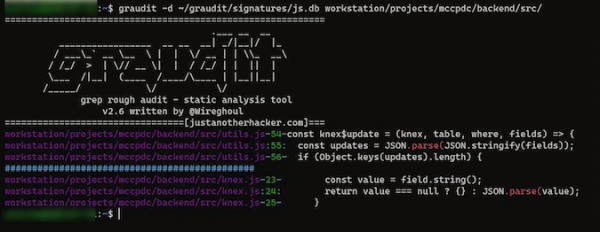
You can try testing your projects in the same way. You can view the list of databases for different programming languages. .
Advantages and Disadvantages of Graudit
Graudit supports many programming languages. Therefore, it is suitable for a wide range of users. It can compete well with any free or paid analogues. Importantly, the project is still being updated, and the community not only assists developers but also helps other users who are trying to understand the tool.
It's a convenient tool, but it doesn't always accurately pinpoint the problem related to suspicious sections of code. Developers continue to improve Graudit.
Nonetheless, it is useful to pay attention to potential security issues in the code by using similar tools.
Getting Started...
In this article, I covered just one of many ways to find vulnerabilities—static application security testing. Conducting static code analysis is easy, but it's just the beginning. To learn more about the security of your codebase, other types of testing need to be integrated into the software development lifecycle.
Advertising
and the right choice of plan will allow you to focus less on distracting problems—everything will run smoothly with very high uptime!
Source: habr.com
