

According to Russian laws, any company that handles the personal data of its users in Russia automatically becomes a data operator, whether it wants to or not. This imposes a number of formal and procedural obligations that not every business can or wants to bear independently.
As practice shows, it is completely reasonable not to want to, because this area of knowledge is still so new and untested in practice that difficulties and questions arise even among professionals. Today we will talk about how we implemented a project for storing personal data for our client and the non-obvious challenges we faced.
How we helped protect data under 152-FZ
In early 2019, we were approached by Smart-Service LLC, a developer of a platform for managing service maintenance. and an application for exchanging contacts. .
The first solution automates the equipment maintenance process in a variety of fields—from configuring coffee machines and air conditioners in office spaces to repairing gas turbines. The second is an online builder for creating electronic business cards based on QR codes.
Online business card myQRcards.
Both systems store and process user data that falls under the classification of 'personal' according to 152-FZ. In this case, the law dictates a number of restrictions on the storage systems of such personal data to ensure the required level of protection and to eliminate the risk of unauthorized access for theft or improper use.
The law must be complied with, but Smart-Service did not plan to develop internal competencies for protecting personal data. Therefore, the services and data shared by their users 'moved' to Linxdatacenter. Smart-Service migrated the server capacities of its working environment to a separate secure network zone of our data center, certified in accordance with the requirements set forth in 152-FZ—commonly referred to as the 'Protected Cloud.'
HOW THE PROTECTED CLOUD IS ORGANIZED
Any information system that processes personal data must meet three main requirements:
- Access to data storage and processing servers must be conducted through a VPN channel with encryption according to GOST standards;
- Data storage and processing servers must be under constant antivirus monitoring for vulnerabilities;
- The storage system must be located in isolated networks.
We host the client's server capacities in separate zones that meet the requirements of Federal Law 152-FZ and assist in obtaining compliance certificates.
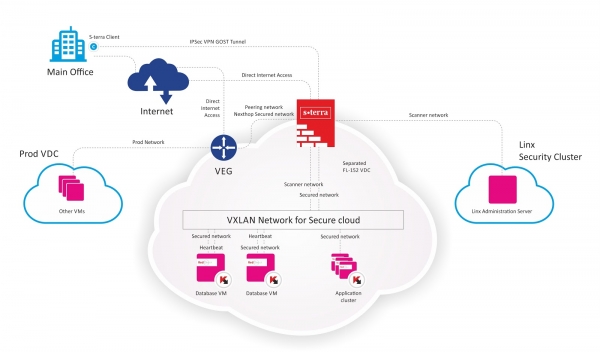
Architecture of the secure virtual infrastructure for LLC 'Smart Service'.
Work Progress
The initial agreement on the work was made in June 2019, which can be considered the project's start date. All work must be carried out in a 'live' environment with thousands of requests per day. Naturally, the project needed to be completed without interrupting the normal operation of both systems.
Therefore, a clear action plan was developed and agreed upon, divided into four phases:
- preparation,
- migration,
- testing and verification under real conditions,
- including the implementation of monitoring systems and access restrictions.
Just in case, we provided for a recovery procedure in unforeseen situations (DRP). According to the initial plan, the work did not take much time and resources and was to be completed by July 2019. Each phase included complete testing of network availability and system functionality at the end.
The most challenging phase, in which 'something could go wrong', was migration. Initially, we planned to carry out migration by transferring virtual machines entirely. This seemed the most logical option since it did not require additional resources for reconfiguration. What could be simpler than vMotion?
Unexpectedly,
however, as is often the case in projects in relatively new fields, the unexpected happened.
Since each virtual machine occupies 500 — 1,000 GB, copying such volumes even within a single data center took about 3-4 hours for each machine. As a result, we did not make it within the allocated time window. This was due to the physical limitations of the disk subsystem when transferring data to vCloud.
The bug in the used version of vCloud prevented the organization of Storage vMotion for virtual machines with different types of disks, so the disks had to be changed. As a result, it was possible to move the virtual machines, but it took longer than planned.
The second aspect we did not foresee was the limitations on moving the database cluster (Failover Cluster MS SQL Server). As a result, we had to switch the cluster to operate with a single node and keep it outside the protected zone.
Notably, for still unknown reasons, during the transfer of virtual machines, the application cluster fell apart, and it had to be rebuilt.
As a result of the first attempt, we found the systems in an unsatisfactory state and had to start over with planning and exploring options.
Attempt #2
After analyzing the mistakes, the team realized that it would be better to duplicate the infrastructure in the protected zone and only copy the data files. It was decided not to charge the client for the additional server capacity that had to be deployed to complete the migration.
As a result, when the clusters in the protected zone were completely duplicated, the migration went smoothly.
Next, it was only necessary to separate the networks of the protected and unprotected zones. This was accomplished with only a few minor interruptions in service. The testing phase of the entire system in the protected zone without any protection was successfully launched. After gathering positive statistics on the system's operation in this mode, we moved on to the final stage: launching protection systems and restricting access.
A successful outcome and a valuable lesson
In the end, through joint efforts with the client, significant changes were made to the existing server infrastructure, which increased the reliability and security of personal data storage, substantially reduced the risks of unauthorized access to them, and achieved certification of compliance with storage requirements — an achievement that not all developers of similar software have yet reached.
In summary, the work on the project looked like this:
- A dedicated subnet was organized;
- A total of two clusters have been migrated, consisting of five virtual machines: a Failover database cluster (two virtual machines) and a Service Fabric application cluster (three virtual machines);
- Security and data encryption systems have been configured.
It all seems clear and logical. However, in practice, things turn out to be a bit more complicated. We have once again confirmed that working on each individual task of this nature requires the highest level of attention to the 'details', which, upon closer inspection, turn out to be crucial factors for the success of the entire project.
Source: habr.com
