

Today, the issue of information security (hereinafter - IS) for companies is one of the most pressing concerns globally. This is not surprising, as many countries are tightening regulations on organizations that store and process personal data. Currently, Russian legislation requires a significant portion of paperwork to be maintained in physical form. At the same time, there is a noticeable trend toward digitalization: many companies already store a large amount of confidential information in both digital and paper formats.
According to the results of the Anti-Malware analytical center, 86% of respondents reported that over the past year, they had to resolve incidents due to cyberattacks or breaches of established regulations at least once. As a result, prioritizing attention to information security in business has become a necessity.
Currently, corporate information security involves not only a set of technical means, such as antivirus software or firewalls, but also a comprehensive approach to managing the company's assets as a whole and information in particular. Companies take different approaches to solving these issues. Today, we would like to discuss the introduction of the international standard ISO 27001 as a solution to such a problem. For companies in the Russian market, having such a certificate simplifies interaction with foreign clients and partners who have high requirements in this regard. ISO 27001 is widely used in the West and covers the information security requirements that must be met by the technical solutions employed, as well as facilitate the establishment of business processes. Thus, this standard can serve as your competitive advantage and a point of contact with foreign companies.
This Information Security Management System (ISMS) certification has incorporated best practices for designing an ISMS and, importantly, has provided options for control measures to ensure the system's functionality, requirements for technological security provisions, and even for the personnel management process within the company. It is essential to understand that technical failures are only part of the issue. In information security matters, the human factor plays a significant role, and excluding or minimizing it is considerably more complex.
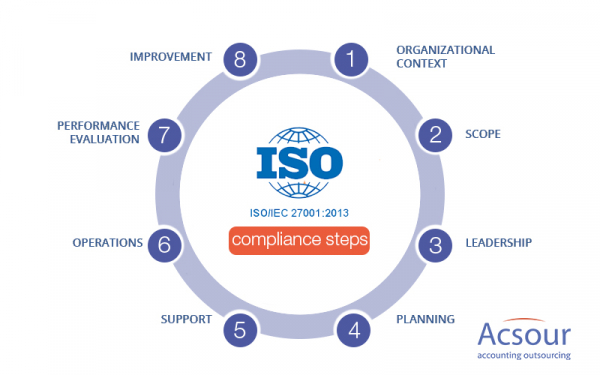
If your company intends to undergo certification according to ISO 27001, you may have already tried to find an easy way to achieve this. We must disappoint you: there are no easy paths here. However, there are specific steps that can help prepare the organization for international information security requirements:
1. Gain support from management
You may consider this obvious, but in practice, this point is often overlooked. Moreover, it is one of the primary reasons why ISO 27001 implementation projects frequently fail. Without understanding the significance of the standard implementation project, management will not allocate sufficient human resources or an adequate budget for certification.
2. Develop a certification preparation plan
Preparing for ISO 27001 certification is a comprehensive task that involves various types of work, requires the engagement of many people, and can last for many months (or even years). Therefore, it is crucial to create a detailed project plan: allocate resources, time, and personnel engagement to strictly defined tasks and monitor deadline compliance—otherwise, you may never complete the work.
3. Define the certification scope
If you have a large organization with diversified activities, it may make sense to certify only a part of the company's business according to ISO 27001, which significantly reduces your project's risks, as well as its duration and cost.
4. Develop an information security policy
One of the most important documents is the company's Information Security Policy. It should reflect your company's goals in the field of information security and the main principles of information security management that must be followed by all employees. The purpose of this document is to define what the company's management intends to achieve in the field of information security, as well as how this will be implemented and monitored.
5. Define the risk assessment methodology
One of the most challenging tasks is to establish the rules for risk assessment and management. It is important to understand which risks the company can consider acceptable, and which require immediate action to mitigate. Without these rules, the ISMS will not function.
At the same time, it is important to remember the adequacy of the measures taken to reduce risks. However, one should not get too carried away with the optimization process, as it can entail significant time and financial costs or may simply be unfeasible. We recommend that when developing risk mitigation measures, you adhere to the principle of 'minimum sufficiency.'
6. Manage risks according to the approved methodology
The next step is the consistent application of the risk management methodology, that is, assessing and processing them. This process should be carried out regularly with great diligence. By maintaining the information security risk register up to date, you will be able to effectively allocate the company's resources and prevent serious incidents.
7. Plan risk treatment
Risks that exceed the acceptable level for your company must be included in the risk treatment plan. It should document actions aimed at reducing risks, as well as the responsible individuals and deadlines.
8. Complete the Statement of Applicability
This is a key document that will be reviewed by specialists from the certification body during the audit. It should describe which information security control mechanisms are applicable to your company's activities.
9. Determine how the effectiveness of information security management controls will be measured
Any action must lead to a result that achieves the established objectives. Therefore, it is important to clearly define the parameters by which the achievement of goals will be measured for the entire information security management system, as well as for each selected control mechanism from the Appendix on applicability.
10. Implement information security controls
Only after executing all previous steps should you begin implementing applicable information security controls from the Appendix on applicability. The greatest challenge here will undoubtedly be the introduction of a completely new way of operating across many processes in your organization. People generally resist new policies and procedures, so pay attention to the next point.
11. Implement training programs for employees
All the points mentioned above will be meaningless if your employees do not understand the importance of the project and do not act in accordance with information security policies. If you want your staff to comply with all the new rules, you must first explain to them why these rules are necessary and then conduct training on the ISMS, highlighting all the important policies that employees should consider in their daily work. A lack of staff training is a common reason for the failure of an ISO 27001 project.
12. Maintain ISMS processes
At this stage, ISO 27001 becomes a daily routine in your organization. To confirm the implementation of information security controls in accordance with the standard, auditors will need to provide records – evidence of the real functioning of control mechanisms. But first and foremost, the records should help you track whether your employees (and suppliers) are fulfilling their tasks in accordance with the established rules.
13. Monitor the ISMS
What is happening with your ISMS? How many incidents do you have, and what type are they? Are all procedures being properly followed? With these questions, you should check whether the company is achieving its information security goals. If not, you need to develop a corrective action plan.
14. Conduct internal ISMS audits
The goal of an internal audit is to identify discrepancies between the actual processes in the company and the approved policies in the field of information security. Primarily, this is an examination of how well your employees adhere to the rules. This is a very important point, as failure to monitor your staff's performance can result in harm to the organization (whether intentional or unintentional). However, the aim here is not to find fault and impose disciplinary sanctions for policy violations, but rather to correct the situation and prevent future problems.
15. Organize an analysis by management
Management should not configure your firewall, but it must be aware of what is happening in the information security management system (ISMS): for instance, whether all duties are being fulfilled and whether the ISMS is achieving its targets. Based on this, management should make key decisions regarding the improvement of the ISMS and internal business processes.
16. Implement a corrective and preventive action system
Just as any ISO 27001 standard requires 'continuous improvement': systematic correction and prevention of nonconformities in the information security management system. Through corrective and preventive actions, it is possible to address nonconformities and prevent their recurrence in the future.
In conclusion, it is worth mentioning that obtaining certification is actually much more challenging than described in various sources. The fact that currently in Russia only have passed certification for compliance is evidence of this. Meanwhile, abroad, it is one of the most popular standards, meeting the growing demands of businesses in the field of information security. This high demand for implementation is driven not only by the increase and complexity of threat types but also by legal requirements, as well as by clients who need full confidentiality of their data.
Despite the fact that ISMS certification is a complex task, the mere fact of meeting the requirements of the international standard ISO/IEC 27001 can provide a significant competitive advantage in the global market. We hope that our article provided an initial understanding of the key steps in preparing a company for certification.
Source: habr.com
