

The ecosystem of containerization technologies is evolving rapidly, lacking good working practices in this area. Despite this, Kubernetes and containers are increasingly used—for modernizing legacy applications and developing modern cloud applications.
The command gathered forecasts, advice, and best practices for market leaders from Gartner, 451 Research, StacxRoх, and others. They will help ensure and accelerate the deployment of containers in production environments.
How to determine if your company is ready to deploy containers in a production environment
, in 2022 over 75% of organizations will use containerized applications in production. This is significantly more than the current situation, where less than 30% of companies use such applications.
According to , projects the market for container technology application in 2022 to be $4.3 billion. This is more than double the amounts projected in 2019, with a market growth rate of 30%.
In 87% of respondents stated that they currently use container technologies. In comparison, in 2017, only 55% of respondents did.
Despite the growing interest and adoption of containers, deploying them in production requires training due to technological immaturity and a lack of know-how. Organizations need to realistically assess the business processes that require application containerization. IT leaders should evaluate whether they have the skill set necessary to move forward, keeping in mind the need for rapid training.
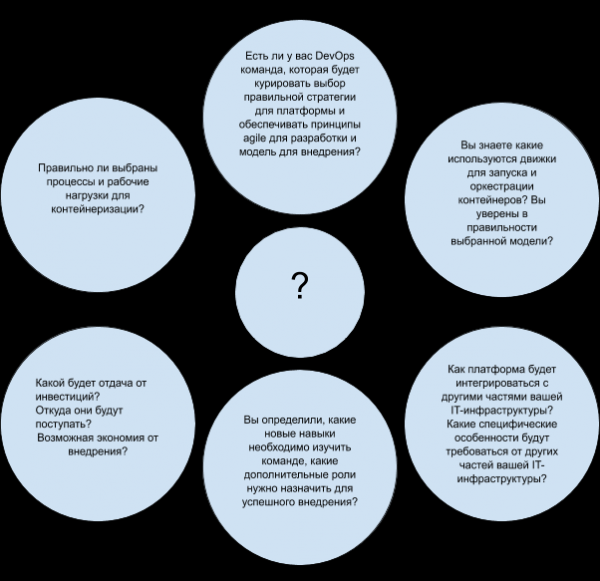
believe that the questions shown in the diagram below will help you understand if you are ready to deploy containers in production:
Most common mistakes when using containers in production
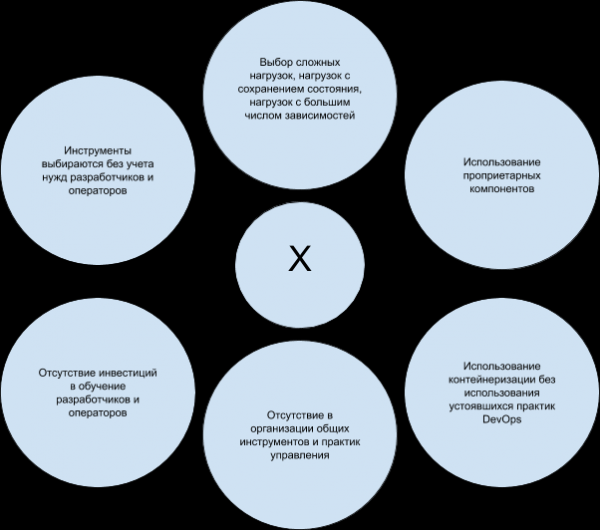
Organizations often underestimate the efforts required to operate containers in production. a number of common mistakes in client scenarios when using containers in production environments:
How to ensure container security
Security cannot be an afterthought. It must be integrated into the DevOps process, which is why the term DevSecOps has emerged. Organizations need to plan throughout the entire software development lifecycle, which includes the building and development process, deployment, and application launch.
:
- Integrate the process of scanning application images for vulnerabilities into the continuous integration/continuous delivery (CI/CD) pipeline. Applications are scanned at the stages of software build and launch. Emphasize the necessity of scanning and identifying components with open source, libraries, and frameworks. The use of outdated vulnerable versions by developers is one of the primary causes of container vulnerabilities.
- Enhance configuration using tests from the Center for Internet Security (), which are available for both Docker and Kubernetes.
- Be sure to apply access control, ensure segregation of duties, and implement a secrets management policy. Sensitive information, such as Secure Sockets Layer (SSL) keys or database credentials, is encrypted by the orchestrator or third-party management services and provided at runtime.
- Avoid containers with elevated privileges using security policy management, which will reduce potential hacking risks.
- Use security tools that provide whitelists, behavioral monitoring, and anomaly detection to prevent malicious actions.
:
- Utilize the built-in features of Kubernetes. Configure access for users using roles. Ensure that you do not grant unnecessary permissions to individual entities, even if it may take some time to consider the minimally required permissions. It may seem tempting to give the cluster administrator broad privileges, as this saves time during the initial setup. However, any compromises or errors in account handling can lead to devastating consequences later on.
- Avoid duplicating access permissions. Sometimes it can be helpful to have different roles overlap, but this can lead to operational issues and create 'dead zones' when removing permissions. Additionally, it is important to remove unused and inactive roles.
- Set network policies: isolate modules to restrict access; explicitly allow internet access for those modules that require it using tags; explicitly allow communication between those modules that need to interact with each other.
How to organize monitoring of containers and services within them
Security and monitoring — when deploying Kubernetes clusters. Developers tend to focus more on the application features they are developing than on the aspects .
:
- Try to monitor the state of containers or services within them together with the monitoring of the host systems.
- Prefer vendors and tools with deep integration into container orchestration, especially Kubernetes.
- Choose tools that provide detailed logging, automatic service discovery, and real-time recommendations using analytics and/or machine learning.
:
- to use tools for automatic discovery and tracking of container metrics, correlating performance metrics such as CPU, memory, and uptime.
- Ensure optimal capacity planning by forecasting capacity exhaustion timelines based on container monitoring metrics.
- Organize monitoring of applications hosted in containers based on availability and performance parameters, which is useful for both capacity planning and troubleshooting performance issues.
- Automate workflows by providing support for managing and scaling containers and their hosting environments.
- Automate access control by tracking the user database, disabling outdated and guest accounts, and removing excess privileges.
- Ensure that your toolset can track these containers and applications across various environments (cloud, on-premises, or hybrid) for visualization and performance mapping in infrastructure, networks, systems, and applications.
How to store data and secure it
With the increase in the number of stateful container workloads, customers need to consider data residing outside the host, as well as the need to protect this data.
According to data , data security tops the list of security concerns noted by most respondents (61%).
Data encryption is a primary security strategy (64%), however respondents also utilize runtime monitoring
(49%), vulnerability scanning in registries (49%), vulnerability scanning in CI/CD pipelines (49%), and anomaly blocking through runtime protection (48%).
:
- Choose data storage solutions built on the principles of . It’s better to opt for those that meet data storage requirements for container services, are hardware agnostic, API-managed, have a distributed architecture, support on-premises deployment, and deployment in public cloud.
- Avoid proprietary plugins and interfaces. Choose vendors that provide integration with Kubernetes and support standard interfaces such as CSI (Container Storage Interfaces).
How to work with networks
The traditional model of enterprise networking, where IT specialists create development, testing, quality assurance, and production network environments for each project, doesn’t always align well with continuous development workflows. Additionally, container networks span multiple layers.
In high-level rules that the implementation of a cluster-network solution should adhere to:
- Pods scheduled on the same node should be able to communicate with other modules without using NAT (Network Address Translation).
- All system demons (background processes such as kubelet) running on a specific node can interact with pods running on the same node.
- Pods using must be able to communicate with all other pods on all other nodes without using NAT. Note that the host network is supported only on Linux hosts.
Networking solutions should be closely integrated with Kubernetes primitives and policies. IT leaders should strive for a high degree of network automation, providing developers with appropriate tools and sufficient flexibility.
:
- Determine whether your CaaS (Container as a Service) or your SDN (Software Defined Network) supports Kubernetes networking. If not or if support is inadequate, use a CNI (Container Network Interface) for your containers that supports the necessary functionality and policies.
- Ensure that your CaaS or PaaS (Platform as a Service) supports the creation of ingress controllers and/or load balancers that distribute incoming traffic across cluster nodes. If this capability is lacking, consider using third-party proxies or service mesh mechanisms.
- Train your network engineers to work with Linux networks and network automation tools to bridge the skill gap and enhance flexibility.
How to manage application lifecycle
For automated and seamless application delivery, it is essential to complement container orchestration with other automation tools, such as Infrastructure as Code (IaC) products. These include Chef, Puppet, Ansible, and Terraform.
Build and deployment automation tools are also needed (see ""). Containers also provide scaling capabilities similar to those available when deploying virtual machines (VMs). Thus, IT leaders must have .
:
- Establish standards for base container images considering size, licensing, and flexibility for developers to add components.
- Use configuration management systems to manage the lifecycle of containers that host configurations in layers based on base images located in public or private repositories.
- Integrate the CaaS platform with automation tools to automate the entire application workflow.
How to Manage Containers with Orchestrators
Core functionalities for deploying containers are provided at the orchestration and scheduling levels. During scheduling, containers are placed on the most optimal hosts in the cluster as dictated by orchestration level requirements.
Kubernetes has de facto become the standard for container orchestration, supported by an active community and most leading commercial providers.
:
- Identify basic requirements for security control elements, monitoring, policy management, data retention, network management, and the container lifecycle.
- Based on these requirements, select a tool that best fits your needs and use cases.
- Use Gartner research (see ""), to understand the advantages and disadvantages of different Kubernetes deployment models and choose the one that best suits your task.
- Choose a provider that can deliver hybrid orchestration for running containers across multiple environments with tight integration with backends, shared management plans, and consistent pricing models.
How to Leverage Cloud Provider Capabilities
, that interest in deploying containers in public cloud IaaS is growing due to the availability of ready-made CaaS offerings and the close integration of these offerings with other products provided by cloud providers.
IaaS clouds offer on-demand resource consumption, rapid scalability, and , which helps avoid the need for deep knowledge about infrastructure and its maintenance. Most cloud providers offer container management service, while some provide multiple orchestration options.
Key managed service cloud providers are represented in the table:
Cloud Provider
Service Type
Product/Service
Alibaba
Native Cloud Service
Alibaba Cloud Container Service, Alibaba Cloud Container Service for Kubernetes
Amazon Web Services (AWS)
Native Cloud Service
Amazon Elastic Container Services (ECS), Amazon ECS for Kubernetes (EKS), AWS Fargate
Giant Swarm
MSP
Giant Swarm Managed Kubernetes Infrastructure
Google
Native Cloud Service
Google Container Engine (GKE)
IBM
Native Cloud Service
IBM Cloud Kubernetes Service
by Microsoft
Native Cloud Service
Azure Kubernetes Service, Azure Service Fabric
Oracle
Native Cloud Service
OCI Container Engine for Kubernetes
Platform9
MSP
Managed Kubernetes
Red Hat
Hosted Service
OpenShift Dedicated & Online
VMware
Hosted Service
Cloud PKS (Beta)
Mail.ru Cloud Solutions*
Native Cloud Service
Mail.ru Cloud Containers
* Let's be honest, we added ourselves during the translation 🙂
Public cloud providers are also adding new features and launching localized products. In the near future, cloud providers will enhance support for hybrid clouds and multi-cloud environments.
:
- Objectively assess your organization's capabilities to deploy and manage relevant tools, and consider alternative cloud container management services.
- Carefully select software, using open source where possible.
- Choose providers with unified operational models in hybrid environments that offer management of integrated clusters from a single panel, as well as providers that simplify the self-service use of IaaS.
:
- Look for distributions that support high availability out of the box. This includes support for multiple core architectures, highly available etcd components, as well as backup and recovery.
- To ensure the portability of Kubernetes environments, it's better to choose cloud providers that support a wide range of deployment models: from on-premises to hybrid and multi-cloud.
- Providers' offerings should also be evaluated based on the ease of configuration, installation, and cluster creation, as well as updates, monitoring, and troubleshooting. A basic requirement is support for fully automated cluster updates with zero downtime. The chosen solution should also allow for manual update execution.
- Identity and access management is important both from a security and management perspective. Ensure that the selected Kubernetes distribution supports integration with the authentication and authorization tools used within the company. RBAC and detailed access control are also important feature sets.
- The selected distribution must either have its own networking solution determined by the software, covering a wide range of requirements imposed by various applications or infrastructure, or support one of the popular CNI-based network implementations, including Flannel, Calico, kube-router, or OVN.
The deployment of containers into production is becoming a key trend, as evidenced by the results of a survey conducted at on infrastructure, operations, and cloud strategies (IOCS) in December 2018:
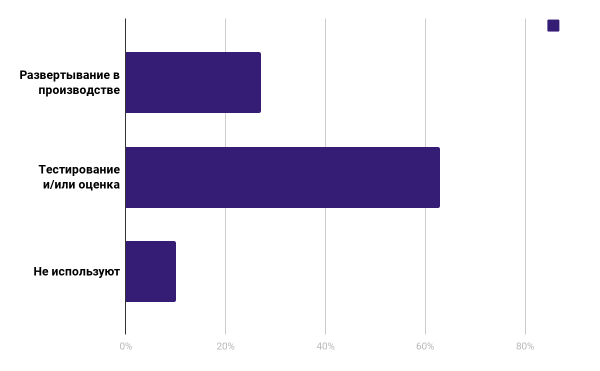
As we can see, 27% of respondents are already using containers in their work, while 63% plan to do so.
In 24% of respondents reported investing more than half a million dollars a year in container technologies, while 17% of respondents spend over a million dollars a year on them.
This article was prepared by the cloud platform team .
What else to read on the topic:
- .
- .
- .
Source: habr.com
