

Alongside email encryption and the use of digital signatures, one of the most effective and cost-efficient ways to protect email from hacking is a well-defined password security policy. Passwords written on paper, stored in public files, or simply insufficiently complex pose a significant vulnerability to a company's information security and can lead to serious incidents with noticeable business consequences. Therefore, a strict password security policy must exist in any organization.
However, any security professional knows that a password policy will only be effective if it is not only in place but also strictly adhered to by everyone, or at least by key employees of the organization. Achieving this is more complicated than it seems. Overworked employees frequently forget the need to change passwords or take the path of least resistance, making passwords simpler and simpler, thus nullifying the entire effect. This is why the issue of compliance with password policies in organizations is usually addressed through various technical means.
To monitor compliance with the password policy in Zimbra, no third-party applications are required. This can be achieved with built-in tools.
First, let's understand how password management works in Zimbra. When a new account is created, the administrator assigns a temporary password to it. After that, the user can log into the account and change the password. All passwords are stored in encrypted form on server Zimbra, making them inaccessible even to the server administrator. This is why, if a user forgets their password, they will have to create a new one. Notably, until recently, creating a new password required the administrator's involvement, but the latest version of Zimbra Creative Suite 8.8.9 introduced the ability for users to set a new password themselves.
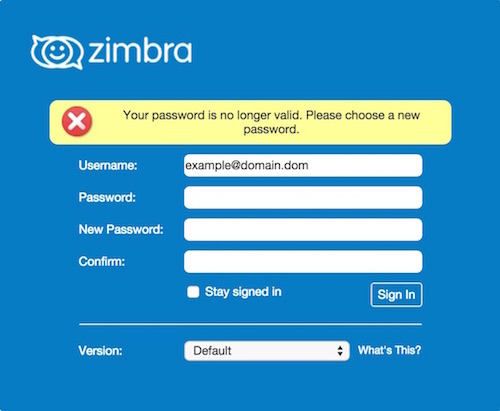
Password policy settings can be found in the settings of individual users and user groups. You can configure:
- Password length — allows you to set the minimum and maximum password length. By default, the minimum password length is 6 characters and the maximum is 64.
- Password aging — allows you to set the time after which a password becomes invalid. Users do not have to wait for the password to expire and can change it before it expires.
- Minimum upper case characters — allows you to set the minimum number of uppercase letters that must be used in the password.
- Minimum lower case characters — allows you to set the minimum number of lowercase letters that must be used in the password.
- Minimum numeric characters — allows you to set the minimum number of digits from 0 to 9 that must be used in the password.
- Minimum punctuation symbols — allows you to set the minimum number of punctuation marks and special characters that must be used in the password.
- Enforce password history — allows you to set the number of remembered passwords so that the user does not periodically use repeating passwords.
- Password locked — this option allows you to prohibit the user from changing their password.
- Enable failed log in lockout — this option allows you to configure the system's response to incorrect password entries.
As you can see, the password settings in Zimbra are quite flexible and can adapt to the password policy of nearly any organization. Additionally, using a simple script, you can set up reminders for users that their password will soon expire. This reminder allows employees to change their passwords in a calm environment, while a missed password change could negatively impact the efficiency of an employee whose mail isn’t opening in the morning.
To make this script work, it should be copied into a file and made executable. It is recommended to automate the execution of this script using Cron, so that it alerts users who have not updated their password in a long time that it will soon stop working. Additionally, in the script, replace zimbra.server.com with your own server name. domain.
#!/bin/bash
# Задаем ряд переменных:
# Сперва количество дней для первого напоминания, затем для последнего:
FIRST="3"
LAST="1"
# Задаем адрес отправителя:
FROM="admin@zimbra.server.com"
# Задаем адрес получателя, который будет получать письмо со списком аккаунтов с истекшими паролями
ADMIN_RECIPIENT="admin@zimbra.server.com"
# Указываем путь к исполняемому файлу Sendmail
SENDMAIL=$(ionice -c3 find /opt/zimbra/common/sbin/sendmail* -type f -iname sendmail)
# Получаем список всех пользователей.
USERS=$(ionice -c3 /opt/zimbra/bin/zmprov -l gaa $DOMAIN)
# Указываем дату с точностью до секунды:
DATE=$(date +%s)
# Проверяем каждого из них:
for USER in $USERS
 do
# Узнаем, когда был установлен пароль
USERINFO=$(ionice -c3 /opt/zimbra/bin/zmprov ga "$USER")
PASS_SET_DATE=$(echo "$USERINFO" | grep zimbraPasswordModifiedTime: | cut -d " " -f 2 | cut -c 1-8)
PASS_MAX_AGE=$(echo "$USERINFO" | grep "zimbraPasswordMaxAge:" | cut -d " " -f 2)
NAME=$(echo "$USERINFO" | grep givenName | cut -d " " -f 2)
# Проверяем, нет ли среди пользователей тех, у кого срок действия пароля уже истек.
if [[ "$PASS_MAX_AGE" -eq "0" ]]
then
  continue
fi
# Высчитываем дату окончания действия паролей
EXPIRES=$(date -d  "$PASS_SET_DATE $PASS_MAX_AGE days" +%s)
# Считаем, сколько дней осталось до окончания срока действия пароля
DEADLINE=$(( (($DATE - $EXPIRES)) / -86400 ))
# Отправляем письмо пользователям
SUBJECT="$NAME - Ваш пароль станет недействительным через $DEADLINE дней"
BODY="
Здравствуйте, $NAME,
Пароль вашего аккаунта станет недействительным через $DEADLINE дней, Пожалуйста, создайте новый как можно скорее.
Вы можете также создать напоминание о смене пароля в календаре Zimbra.
Заранее спасибо.
С уважением, IT-отдел
"
# Первое предупреждение
if [[ "$DEADLINE" -eq "$FIRST" ]]
then
	echo "Subject: $SUBJECT" "$BODY" | $SENDMAIL -f "$FROM" "$USER"
	echo "Reminder email sent to: $USER - $DEADLINE days left"
# Последнее предупреждение
elif [[ "$DEADLINE" -eq "$LAST" ]]
then
	echo "Subject: $SUBJECT" "$BODY" | $SENDMAIL -f "$FROM" "$USER"
	echo "Reminder email sent to: $USER - $DEADLINE days left"
# Final
elif [[ "$DEADLINE" -eq "1" ]]
then
    echo "Subject: $SUBJECT" "$BODY" | $SENDMAIL -f "$FROM" "$USER"
	echo "Last chance for: $USER - $DEADLINE days left"
fi
done
Thus, it can be said that the Zimbra Collaboration Suite is suitable even for those enterprises with strict password policies. Thanks to its built-in features, ensuring compliance from employees will be quite simple.
For all inquiries related to Zextras Suite, you can contact the company's representative, Katerina Triandafili, at katerina@zextras.com.
Source: habr.com
