

The new hacking method overcomes the problem of 'network jitter', which can affect the success of attacks through side channels.
The new technique, developed by researchers from KU Leuven (Belgium) and New York University in Abu Dhabi, showed that attackers can exploit characteristics of network protocols to leak confidential information.
This method, called , demonstrated this year at the Usenix conference, utilizes the peculiarities of network protocols for concurrently executed requests to eliminate one of the issues with remote time-based attacks via side channels.
Remote time-based attack issues
In executing time-based attacks, attackers measure the differences in execution time for various commands in an attempt to bypass encryption protections and obtain data about confidential information, such as encryption keys, private correspondence, and user behavior while web surfing.
However, for a time-based attack to be successful, the attacker needs precise knowledge of the time it takes for the attacked application to process a request.
This becomes a challenge when targeting remote systems like web servers, as network latency (jitter) leads to variation in response times, complicating the calculation of processing time.
In the process of remote time-based attacks, attackers typically send each command multiple times and perform statistical analysis of response times to mitigate the influence of network jitter. However, this approach is only beneficial to a certain extent.
"The smaller the time difference, the more requests are needed, and at a certain point, the calculation becomes impossible," explains Tom Van Goethem, a researcher in data protection systems and the lead author of the paper on the new type of attack.
"Timeless" time-based attack
The method developed by Goethem and his colleagues executes remote time-based attacks in such a way that it nullifies the impact of network jitter.
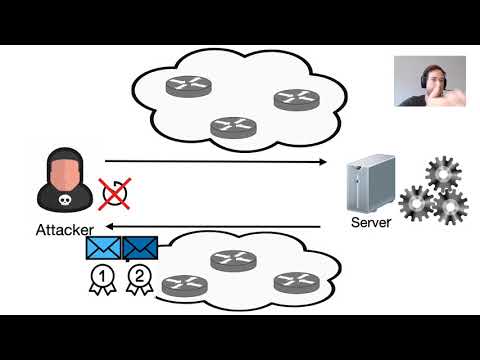
The principle behind the timeless time-based attack is simple: requests must reach the server at exactly the same time, rather than being sent sequentially.
Concurrency ensures that all requests operate under the same network conditions, and that the path between the attacker and the server does not affect their processing. The order in which responses are received provides the attacker with all the information necessary to compare execution times.
"The main advantage of timeless timing attacks lies in their much higher precision, which requires fewer requests. This allows the attacker to detect differences in execution time down to 100 ns," says Van Goetem.
The minimum time difference observed by researchers during a traditional timing attack over the Internet was 10 µs, which is 100 times greater than that of an attack using concurrent requests.
How Concurrency is Ensured
"We ensure concurrency by placing both requests in a single network packet," explains Van Goetem. "In practice, the implementation mainly depends on the network protocol."
To send concurrent requests, researchers utilize the capabilities of different network protocols.
For example, HTTP/2, which is quickly becoming the de facto standard for web servers, supports "request multiplexing" — a feature that allows the client to send multiple requests in parallel over a single TCP connection.
"In the case of HTTP/2, we just need to ensure that both requests are placed in one packet (for instance, by writing both to the socket simultaneously)." However, this method has its nuances. For example, in most content delivery networks like Cloudflare, which serves a large portion of the web, the connection between edge servers and the site is made over HTTP/1.1, which does not support request multiplexing.
Although this reduces the effectiveness of the timeless attack, they remain more precise than classic remote timing attacks because they eliminate jitter between the attacker and the edge CDN server.
In the case of protocols that do not support request multiplexing, attackers may use an intermediary network protocol that encapsulates the requests.
Researchers have demonstrated how a timeless timing attack works on the Tor network. In this case, the attacker encapsulates multiple requests in a Tor cell — an encrypted packet transmitted between Tor nodes in single TCP packets.
"Because the Tor chain for onion services makes the entire journey to the server, we can ensure that the requests arrive simultaneously," says Van Goetem.
Timeless attacks in practice
In their article, the researchers examined timeless attacks in three different situations.
Upon direct timing attacks the attacker directly connects to the server and attempts to leak confidential information related to the application.
"Since most web applications do not take into account that timing attacks can be very practical and precise, we believe that many websites are vulnerable to such attacks," explains Van Goeten.
Upon cross-site timing attacks the attacker makes requests to other websites from the victim's browser and makes assumptions about the contents of confidential information by observing the sequence of responses.
Attackers used this scheme to exploit a vulnerability in the HackerOne bug bounty program and extracted information such as keywords used in confidential reports of unpatched vulnerabilities.
"I was looking for cases where a timing attack had been previously documented but was not considered effective. The HackerOne bug had been reported at least three times (bug IDs: , and ), but it was not fixed because it was believed that this attack could not be exploited. At that point, I created a simple internal research project with timeless timing attacks.
At that time, it was still very unoptimized because we were continuing to work through the details of the attack, but nonetheless, it turned out to be quite accurate (on my home WiFi connection, I was able to achieve very precise results)."
Researchers also attempted to conduct timeless attacks on the WPA3 WiFi protocol..
One of the co-authors, Matti Vanhoef, had previously identified . But the time was either too short for use on high-performance devices or could not be used against servers.
“With a new type of timeless timing attacks, we have demonstrated that it is indeed possible to use the authentication handshake (EAP-pwd) against servers, even if they are equipped with powerful hardware,” explains Van Goetem.
The Perfect Moment
In their article, the researchers provided recommendations for protecting servers against timeless attacks, such as limiting execution time to constant time and adding random delays. Further research is needed to implement practical defenses against direct time attacks that minimally impact network performance.
“We believe that this area of research is still in its early stages and requires much deeper exploration,” says Van Goetem.
Future studies could explore other techniques that attackers might use to perform simultaneous timing attacks, other protocols, and intermediary layers that could be targeted, as well as assess the vulnerability of popular websites that allow for such research under bug bounty programs.
The term “timeless” was chosen, “because in these attacks we did not use any (absolute) timing information,” explains Van Goetem.
“Moreover, they can be deemed ‘timeless’ because (remote) timing attacks have been used for a long time, and based on our research, the situation is only getting worse.”
The full text of the report with Usenix is available .
Advertising
with DDoS attack protection and the latest hardware. This is all about our epic servers. The maximum configuration includes 128 CPU cores, 512 GB RAM, 4000 GB NVMe.
Source: habr.com
