

SMS messages are the most popular method of two-factor authentication (2FA). They are used by banks, electronic and crypto wallets, email services, and various other services; .
This situation angers me because this method is unsafe. Numbers have been reallocated from one SIM card to another since the early days of mobile phones — this is how numbers are restored when a SIM card is lost. "Digital money thieves" have realized that the 'SIM card rewriting' option can be used in fraudulent schemes. After all, whoever controls the SIM card can manage someone else's online banking, electronic wallets, and even cryptocurrency. A number can be obtained through bribing a telecom employee, deception, or fake documents.
Thousands of episodes of SIM swapping have been uncovered — this is what they call this fraud scheme. The scale of the disaster indicates that the world will soon abandon 2FA via SMS. But this is not happening — in they say that the 2FA method is chosen not by users, but by service owners.
We offer to use a safe 2FA method with one-time codes delivered via blockchain, and we will explain how a service owner can connect it.
The stakes are high
In 2019, SIM swapping fraud increased by 63% according to London police, with the 'average take' for fraudsters being 4,000 GBP. I couldn't find statistics in Russia, but I suspect they are even worse.
SIM swapping is used to steal popular accounts on Twitter, Instagram, Facebook, VK, bank accounts, and recently it has reached cryptocurrency — according to bitcoin entrepreneur Joby Wicks. High-profile cases of cryptocurrency theft through SIM swapping have been appearing in the press since 2016; 2019 saw a real peak.
In May, the U.S. Attorney's Office for the Eastern District of Michigan against nine young people aged 19 to 26: they are believed to be part of a hacking gang called 'The Community'. The gang is charged with seven swapping attacks, resulting in hackers stealing cryptocurrency worth over $2.4 million. In April, a student from California, Joel Ortiz, received 10 years in prison for SIM swapping; his bounty amounted to $7.5 million in cryptocurrencies.
Photo of Joel Ortiz at a press conference at the university. Two years later, he will be arrested for cyber fraud.
How SIM swapping works
"Swapping" means exchanging. In all such schemes, criminals take over the victim's phone number, usually by reissuing the SIM card, and use it to reset the password. A typical SIM swapping scenario looks like this:
- Intelligence. The fraudsters gather personal data about the victim: name and phone number. This information can be found in open sources (social media, friends) or obtained from an accomplice — an employee of the cellular provider.
- Blocking. The victim’s SIM card is deactivated; this is done by simply calling the provider's technical support, stating the number, and saying that the phone has been lost.
- Taking over, transferring the number to their own SIM card. This is usually also done through an accomplice in the telecom company or using forged documents.
In real life, it's even harsher. The perpetrators choose a victim and then track the phone's location daily — one query for information about the subscriber roaming costs 1-2 cents. As soon as the SIM card owner travels abroad, they negotiate with a manager at the retail store to issue a new SIM card. This costs about $50 (I found information ranging from $20 to $100 in different countries and with different providers), with the manager, in the worst case, being fired — there’s no liability for that.
Now all SMS messages will be received by the criminals, and the phone owner won't be able to do anything about it — they are abroad. Subsequently, the villains gain access to all the victim's accounts and can change passwords if they wish.
Chances of recovering stolen funds
Banks sometimes help victims and reverse transfers from their accounts. Therefore, it is possible to recover fiat money, even if the criminal is not found. However, it is more complicated with cryptocurrency wallets — both technicallyand legally. So far, no exchange or wallet has compensated victims of swapping.
If the victims want to defend their money in court, they accuse the operator: they created the conditions for money theft from the account. This is exactly what did, losing $224 million due to swapping. He is currently suing the telecommunications company AT&T.
Currently, no government has effective schemes to legally protect cryptocurrency owners. Insuring your capital or receiving compensation for its loss is impossible. Therefore, preventing a SIM swapping attack is easier than dealing with its consequences. The most obvious way is to use a more reliable 'second factor' for 2FA.
SIM swapping is not the only problem with 2FA through SMS.
Confirmation codes sent via SMS are insecure from a technical standpoint. Messages can be intercepted due to inherent vulnerabilities in the Signaling System 7 (SS7). 2FA via SMS has officially been recognized as insecure (The National Institute of Standards and Technology of the USA states this in their ).
Moreover, having 2FA often gives users a false sense of security, causing them to choose simpler passwords. As a result, such authentication does not hinder but facilitates an attacker’s access to the account.
Additionally, SMS messages often arrive with significant delays or may not arrive at all.
Other 2FA Methods
Of course, smartphones and SMS are not the only options available. There are other methods for 2FA. For example, one-time TAN codes are a primitive but functional approach still used by some banks. There are systems that leverage biometric data, such as fingerprint scans and retina scans. Another option that seems like a reasonable compromise between convenience, reliability, and price is special 2FA applications: RSA Token, Google Authenticator. Physical keys and other methods also exist.
In theory, everything appears logical and secure. However, in practice, modern 2FA solutions have issues, and as a result, reality differs from expectations.
According to , the use of 2FA is inherently inconvenient, and the popularity of SMS 2FA is explained by 'less inconvenience compared to other methods' — users find it straightforward to receive one-time codes.
Many users associate 2FA methods with the fear of losing access. A physical key or list of TAN codes can be lost or stolen. Personally, I have had a negative experience using Google Authenticator. My first smartphone with that app broke—consider my efforts to recover access to my accounts. Another issue is switching to a new device. Google Authenticator does not allow for exporting due to security concerns (if keys can be exported, what is the security?). One time, I transferred the keys manually, but later decided it was easier to keep my old smartphone in a box on the shelf.
The 2FA method should be:
- Secure—only you should have access to your account, not attackers
- Reliable—you can access your account whenever you need to
- Convenient and accessible—using 2FA is straightforward and takes minimal time
- Inexpensive
We believe that blockchain is a suitable solution.
Use 2FA on the blockchain
For the user, 2FA on the blockchain appears just like receiving one-time codes via SMS. The only difference is the delivery channel. The method of obtaining the 2FA code depends on what the blockchain offers. In our project (information is in my profile), it is a Web application, Tor, iOS, Android, Linux, Windows, MacOS.
The service generates a one-time code and sends it to a messenger on the blockchain. Then, classically: the user enters the received code into the service interface and authenticates.
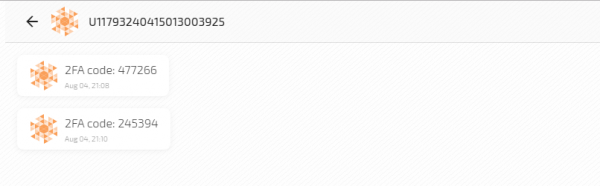
In this article I stated that blockchain ensures the security and privacy of message transmission. Regarding the sending of 2FA codes, I would highlight:
- One click to create an account—no phone numbers or emails required.
- All messages with 2FA codes are encrypted End-to-End using curve25519xsalsa20poly1305.
- MITM attacks are excluded—each message with a 2FA code is a transaction on the blockchain and is signed with Ed25519 EdDSA.
- Messages with 2FA codes go into their own block. The sequence and timestamp of blocks cannot be altered, therefore the order of messages remains unchanged.
- There is no central structure to verify the 'authenticity' of messages. This is managed by the distributed node system based on consensus, which belongs to the users.
- Impossibility of disabling—accounts cannot be blocked and messages cannot be deleted.
- Access to 2FA codes from any device at any time.
- Delivery confirmation of the message with the 2FA code. The service sending the one-time password knows for sure that it has been delivered. No 'Resend' buttons.
To compare with some other 2FA methods, I have created a table:
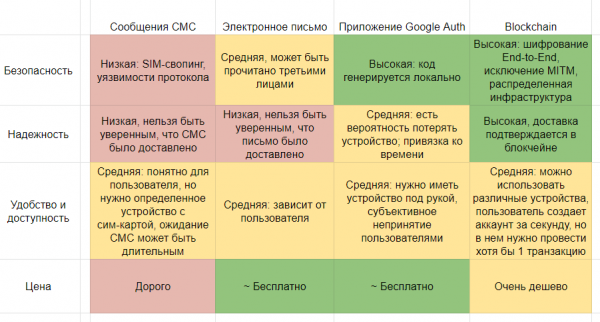
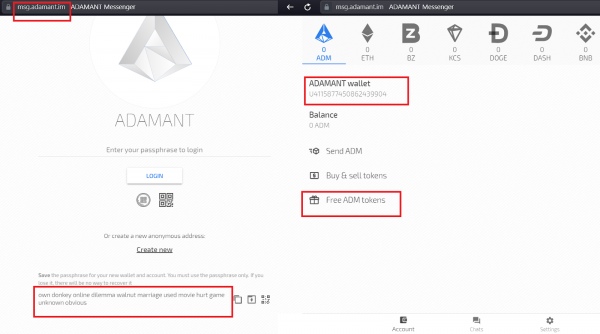
The account in the blockchain messenger for receiving codes is obtained in a second — only the passphrase is used for login. Therefore, the use cases can vary: one can use one account to receive codes for all services, or create a separate account for each service.
There is also an inconvenience — the account must have at least one transaction. For the user to receive an encrypted message with the code, they need to know the public key, which only appears on the blockchain with the first transaction. We have found a workaround: we provided the opportunity to get free tokens in the wallet. However, a more correct solution would be to name the account with the public key. (For comparison, our account number U1467838112172792705 is derived from the public key cc1ca549413b942029c4742a6e6ed69767c325f8d989f7e4b71ad82a164c2ada. For the messenger, this is more convenient and readable, but it's a limitation for the 2FA code sending system). I think in the future someone will come up with such a solution and translate 'Convenience and Availability' into the green zone.
The cost of sending a 2FA code is actually low — 0.001 ADM, currently around 0.00001 USD. Again, one can raise their own blockchain and set the price to zero.
How to connect 2FA on the blockchain to your service
I hope I have managed to interest a few readers to add blockchain authorization to their services.
I will explain how to do this using our messenger as an example, and you can apply the same analogy to other blockchains. In the 2FA demo application, we use postgresql10 to store account information.
Connection steps:
- Create an account in the blockchain from which you will send 2FA codes. You will receive a passphrase that is used as a private key for encrypting messages with codes and for signing transactions.
- Add a script to your server to generate 2FA codes. If you are already using any other 2FA method with one-time password delivery, you have already completed this step.
- Add a script to your server to send codes to the user in the blockchain messenger.
- Create a user interface for sending and entering the 2FA code. If you are already using any other 2FA method with one-time password delivery, you have already completed this step.
1 Account Creation
Creating an account on the blockchain involves generating a private key, a public key, and an address derived from it.
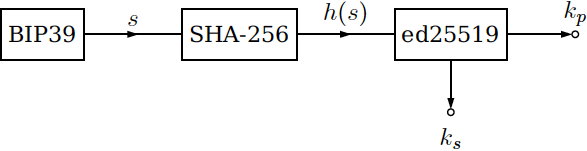
First, a BIP39 passphrase is generated, from which a SHA-256 hash is calculated. This hash is used to generate the private key ks and the public key kp. From the public key, we derive the blockchain address using SHA-256 with inversion.
If you want to send 2FA codes each time from a new account, the code to create the account needs to be added to the server:
import Mnemonic from 'bitcore-mnemonic'
this.passphrase = new Mnemonic(Mnemonic.Words.ENGLISH).toString()

…

import * as bip39 from 'bip39'
import crypto from 'crypto'

adamant.createPassphraseHash = function (passphrase) {
  const seedHex = bip39.mnemonicToSeedSync(passphrase).toString('hex')
  return crypto.createHash('sha256').update(seedHex, 'hex').digest()
}

…

import sodium from 'sodium-browserify-tweetnacl'

adamant.makeKeypair = function (hash) {
  var keypair = sodium.crypto_sign_seed_keypair(hash)
  return {
    publicKey: keypair.publicKey,
    privateKey: keypair.secretKey
  }
}

…

import crypto from 'crypto'

adamant.getAddressFromPublicKey = function (publicKey) {
  const publicKeyHash = crypto.createHash('sha256').update(publicKey, 'hex').digest()
  const temp = Buffer.alloc(8)
  for (var i = 0; i < 8; i++) {
    temp[i] = publicKeyHash[7 - i]
  }
  return 'U' + bignum.fromBuffer(temp).toString()
}
In the demo application, we streamlined the process — created one account in the web app, and we send codes from it. In most cases, this is more convenient for the user: they know that the service sends 2FA codes from a specific account and can label it.
2 2FA Code Generation
A 2FA code needs to be generated for each user login. We use the library , but you can choose any other.
const hotp = speakeasy.hotp({
  counter,
  secret: account.seSecretAscii,
});
Validating the 2FA code entered by the user:
se2faVerified = speakeasy.hotp.verify({
  counter: this.seCounter,
  secret: this.seSecretAscii,
  token: hotp,
});
3 Sending the 2FA Code
To send the 2FA code, you can use the blockchain node’s API, a JS API library, or the console. In this example, we use the console — this is the Command Line Interface, a utility that simplifies interaction with the blockchain. To send a message with the 2FA code, you need to use the command send message of the console.
const util = require('util');
const exec = util.promisify(require('child_process').exec);

…

const command = `adm send message ${adamantAddress} "2FA code: ${hotp}"`;
let { error, stdout, stderr } = await exec(command);
An alternative way to send messages is to use the method send from the JS API library.
4 User Interface
Users should be allowed to input the 2FA code, which can be done in various ways depending on your application's platform. In our example, this is Vue.
The source code of the two-factor authentication demo application on the blockchain can be viewed at . The Readme includes a link to the Live demo for you to try out.
Source: habr.com
