

In many IT systems, there is a mandatory rule for periodic password changes. This is perhaps the most hated and most useless requirement of security systems. Some users, as a life hack, simply change the last digit.
This practice caused a lot of inconvenience. However, people had to endure it, since it was for security. Now, this advice is entirely outdated. In May 2019, even Microsoft finally removed the requirement for periodic password changes from the baseline security requirements for both personal and server versions of Windows 10: here is with the list of changes for Windows 10 v 1903 (note the phrase Dropping the password-expiration policies that require periodic password changes). The rules and system policies Windows 10 Version 1903 and Windows Server 2019 Security Baseline are included in the package .
You can show these documents to your management and say: times have changed. Mandatory password changes are an anachronism, now practically official. Even security audits will no longer check this requirement (if they refer to the official rules for basic protection of Windows computers).
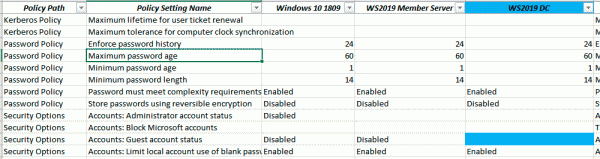
A fragment of the list with basic security policies of Windows 10 v1809 and changes in 1903, where the corresponding time-limited password policies are no longer applied. By the way, in the new version, administrator and guest accounts are also disabled by default.
Microsoft explains in the blog why it abandoned the mandatory password change rule: "Periodic password expiration provides protection only against the likelihood that a password (or hash) will be stolen during its validity and used by an unauthorized person. If a password is not stolen, there is no point in changing it. And if you have evidence that a password has been stolen, you will obviously want to act immediately, rather than wait for it to expire to address the problem."
Microsoft further explains that it is incorrect to protect against password theft in this manner under modern circumstances: "If it is known that a password is likely to be stolen, how many days is an acceptable timeframe to allow a thief to use that stolen password? The default is 42 days. Doesn't that seem like an absurdly long time? Indeed, it is quite a long time, and yet our current baseline was set at 60 days — and previously at 90 days — because enforcing frequent expiration introduces its own set of problems. And if the password isn't necessarily going to be stolen, then you're acquiring these problems without any benefit. Furthermore, if your users are willing to trade their password for a piece of candy, no expiration policy will help."
Alternative
Microsoft states that its baseline security policies are intended to be used by well-managed organizations that care about security. They are also designed to serve as guidance for auditors. If such an organization has implemented banned password lists, multi-factor authentication, detection of password brute-force attacks, and abnormal sign-in attempt detection, is periodic password expiration required? And if they haven't implemented modern protections, will password expiration help them?
Microsoft's logic is surprisingly compelling. We have two options:
- The organization has implemented modern protections.
- Company do not has implemented modern protections.
In the first case, periodic password changes offer no additional benefits.
In the second case, periodic password changes are pointless.
Therefore, instead of a password expiration, one should primarily use multi-factor authentication. Additional protective measures are listed above: banned password lists, brute-force detection, and other abnormal sign-in attempt detections.
«Periodic password expiration is an outdated and archaic security measure., Microsoft concludes, “and we do not believe that any specific value should be applied for our level of basic protection. By removing it from our baseline, organizations can choose what best fits their intended needs without contradicting our recommendations.”
Output
If a company today requires users to change their passwords periodically, what might an outside observer think?
- Given: the company is using an archaic security mechanism.
- Assumption: the company has not implemented modern security mechanisms.
- Output: these passwords are easier to retrieve and use.
Thus, periodic password changes make the company a more attractive target for attacks.
Source: habr.com
