

The implementation of any IT solution in an enterprise begins with design. At this stage, the IT manager must calculate the number of servers and their specifications to ensure that there are enough resources for all users, while also optimizing the price-to-quality ratio of these servers so that the costs of creating the computing infrastructure for the new information system do not significantly impact the enterprise's IT budget. Let’s take a closer look at how to design the infrastructure for deploying Zimbra Collaboration Suite in an organization.
The main feature of Zimbra, compared to other solutions, is that with ZCS, the bottleneck rarely becomes the processing power or RAM. The primary limitation usually lies in the speed of the disk I/O, so the main focus should be on the storage systems. The officially stated minimum requirements for Zimbra in a production environment are a 4-core 64-bit processor with a clock speed of 2 GHz, 10 GB for system files and logs, and at least 8 GB of RAM. Usually, such specifications are sufficient for the responsive operation of the server. But what if you need to deploy Zimbra for 10,000 users? Which servers should be implemented in that case?
First, the infrastructure for 10,000 users must be multi-server. A multi-server infrastructure allows Zimbra to be scalable on one hand and ensures responsive operation of the information system even during peak user loads on the other hand. It is often quite difficult to predict how many users a Zimbra server can effectively serve since it heavily depends on the intensity of their use of calendars and emails, as well as the protocols used. For this example, we will deploy 4 mail stores. In case of insufficient or excessive capacity, we can either shut down or add another one.
Thus, when designing infrastructure for 10,000 users, it will be necessary to create LDAP, MTA, and Proxy servers along with 4 mail storage systems. It is worth noting that the LDAP, MTA, and Proxy servers can be virtual. This will reduce costs for server hardware and simplify data backup and recovery; however, on the flip side, in the event of a physical server failure, you risk losing access to MTA, LDAP, and Proxy simultaneously. That is why the choice between physical or virtual servers should be made based on the allowable downtime in case of an emergency. Mail storage should ideally be placed on physical servers since they will handle the majority of write cycles that limit Zimbra's performance, and therefore, a larger number of data transfer channels will significantly increase Zimbra's productivity.
In principle, after creating servers LDAP, MTA, Proxy, network storage, and integrating them into a unified infrastructure, the Zimbra Collaboration Suite for 10,000 users is ready for deployment. The operational scheme of such a configuration will be quite simple:
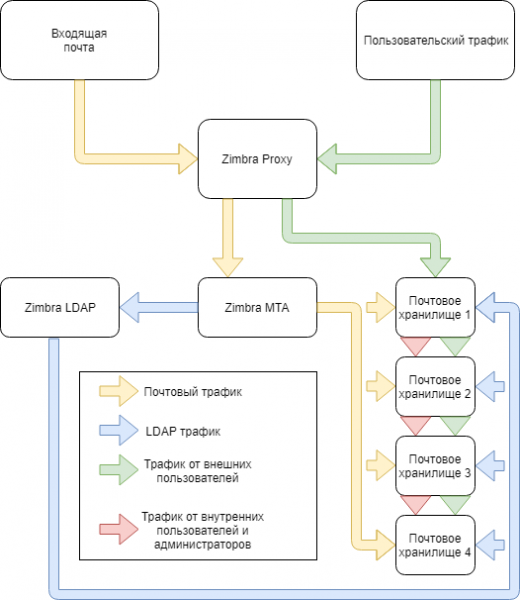
The diagram shows the main nodes of the system and the data flows that will circulate between them. With this configuration, the infrastructure will be completely unprotected against data loss, downtime caused by the failure of any of the servers, and so on. Let's look at how to protect your infrastructure from these problems.
The main method is hardware redundancy. Additional MTA and Proxy nodes can temporarily take over the role of the main servers in the event of the failure of the primary servers. Duplicating nodes of critical infrastructure is almost always a good idea, but it is not always feasible to the desired extent. A prime example is the redundancy of servers that store mail. Currently, the Zimbra Collaboration Suite Open-Source Edition does not support the creation of duplicate storages, so if one of these servers fails, downtime will be unavoidable. To reduce the downtime caused by the failure of the mail storage, the IT manager can deploy its backup on another server. server.
Since there is no built-in backup system in Zimbra OSE, we will need Zextras Backup, which supports real-time backup, and external storage. Given that Zextras Backup stores all data in the /opt/zimbra/backup folder while taking full and incremental backups, it would be wise to mount external, network, or even cloud storage to have a current backup available in case one of the servers fails. It can be deployed on a backup physical server, a virtual machine, or in the cloud. It would also be a good idea to install an MTA with a spam filter in front of the Zimbra Proxy server to reduce the amount of junk traffic coming to the server.
As a result, the protected Zimbra infrastructure will look something like this:
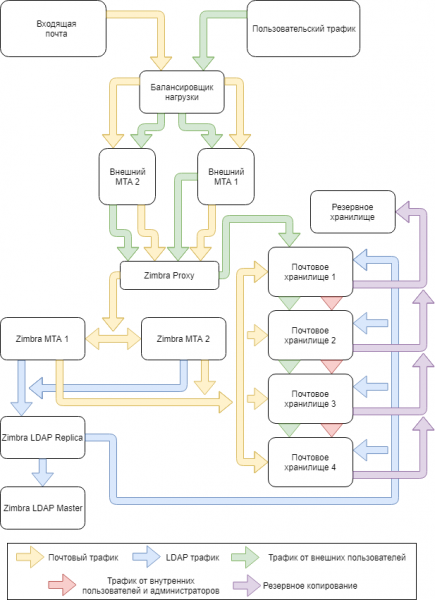
With this configuration, the Zimbra infrastructure will not only be able to provide quality services to 10,000 users but will also allow for a rapid response to any emergency situations.
Source: habr.com
