

Hello everyone! In December, OTUS is launching a new course — . In anticipation of the launch of this course, we are sharing an interesting translation on the topic.
is a solution that helps clients quickly set up a secure AWS environment with multiple accounts based on best practices.
For over five years, our team at Mitoc Group has tirelessly worked to help large organizations successfully undergo digital transformation and build or migrate their digital presence to the AWS cloud. In other words, quoting our friends at AWS: “Our clients are rediscovering themselves with AWS.” It’s an endless effort to reinvent and simplify mechanics on behalf of the clients themselves, and AWS excels at solving complex problems with easy-to-understand solutions.
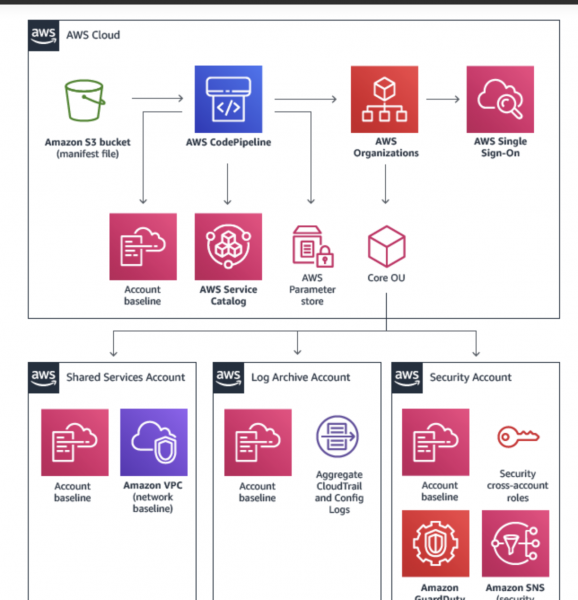
AWS Landing Zone ()
What is AWS Landing Zone?
According to official sources:
AWS Landing Zone is a solution that helps clients set up a secure AWS environment with multiple accounts more quickly, based on AWS best practices. With a large number of options, setting up an environment with multiple accounts can take significant time, involve configuring many accounts and services, and require a deep understanding of how AWS services work.
The AWS Landing Zone solution significantly reduced the complexity and consistency of similar design templates provided to various clients. On the other hand, our team had to reconfigure some CloudFormation components into Terraform components for further automation.
Therefore, we wondered why not build the entire AWS Landing Zone solution in Terraform? Can we do this, and will it solve our clients' problems? Spoiler: It will, and it already is! 🙂
When should you not use AWS Landing Zone?
If you are dealing with standard cloud services and cloud resources within one or two AWS accounts, these measures may be excessive. Everyone who does not fall into this category can continue reading 🙂
What should be considered before getting started?
Many large organizations we've worked with already have some strategy for utilizing cloud technologies. Companies struggle with the successful implementation of cloud services without a clear vision and articulated expectations. Please take the time to define your strategy and understand how AWS fits into it.
When defining their strategy, successful AWS Landing Zone clients actively emphasize the following:
- Just automating is not an option. Native cloud automation is preferred.
- Teams consistently use the same mechanisms with the same toolkit for preparing cloud resources. It's better to use Terraform.
- The most productive cloud service users have the ability to create reusable processes and provide them as reusable services rather than reusable code. Serverless architecture is preferred.
Introducing the Terraform module for AWS Landing Zone
After several months of hard work, I am pleased to present to you . which is hosted on GitHub, and are published on the Terraform Module Registry.
To get started, simply include main.tf in your code:
module "landing_zone" {
  source     = "TerraHubCorp/landing-zone/aws"
  version    = "0.0.6"
  root_path  = "${path.module}"
  account_id = "${var.account_id}"
  region     = "${var.region}"
  landing_zone_components = "${var.landing_zone_components}"
}
Note: Be sure to include variables.tf and anything else you might need from outputs.tf.
To simplify understanding, we've added default values in terraform.tfvars:
account_id = "123456789012"
region = "us-east-1"
landing_zone_components = {
  landing_zone_pipeline_s3_bucket = "s3://terraform-aws-landing-zone/mycompany/landing_zone_pipeline_s3_bucket/default.tfvars"
  [...]
}
This means that when using this module terraform you will need to:
- Change the values
account_idandregionto your own, matching the data in AWS Organization; - Change the values
landing_zone_componentsto those that align with your use case for AWS Landing Zone; - Change
s3://terraform-aws-landing-zone/mycompanyto your block S3 and the key prefix S3, where you will store the.tfvars(or absolute path to the files.tfvarsin your local storage).
This module can have dozens, hundreds, or thousands of deployable components, but not all of them need to be or will be deployed. At runtime, components that are not part of the variable map landing_zone_components will be ignored.
Conclusion
We are very pleased and proud to share the fruits of our efforts that help clients create native cloud automation. The Terraform module for AWS Landing Zone is another solution that assists organizations in quickly setting up a secure AWS environment with multiple accounts, based on AWS best practices. We know that AWS is evolving at an incredible pace, and we strive to develop the Terraform solution just as quickly, covering all the basics while integrating with other AWS working solutions.
That's all for now. We look forward to your comments and invite you to where we will explore the design of the Cloud Landing Zone domain architecture and examine architectural patterns for core domains..
Source: habr.com
