

WPA3 has already been adopted and has been mandatory for devices undergoing certification with the WiFi Alliance since July 2020. WPA2 has not been discontinued and is not going anywhere. Both WPA2 and WPA3 support operation in PSK and Enterprise modes; however, we suggest considering the Private PSK technology in our article, as well as the advantages it can provide.
The issues with WPA2-Personal are well-known and have mostly been addressed (Priority Management Frames, fixes for the KRACK vulnerability, etc.). The primary remaining drawback of WPA2 with PSK is that weak passwords can be easily compromised through a dictionary attack. In case of compromise and changing the password, all connected devices (and access points) will need to be reconfigured, which can be quite a cumbersome process. To address the ‘weak password’ problem, the WiFi Alliance recommends using passwords that are at least 20 characters long.
Another issue that cannot always be resolved with WPA2-Personal is the assignment of different profiles (vlan, QoS, firewall…) to groups of devices connected to the same SSID.
Using WPA2-Enterprise can address all of the issues described above, but the cost of this solution will be:
- The necessity of having or deploying a PKI (Public Key Infrastructure) and security certificates;
- There may be difficulties with installation;
- There may be difficulties with troubleshooting;
- It is not an optimal solution for IoT devices or guest access.
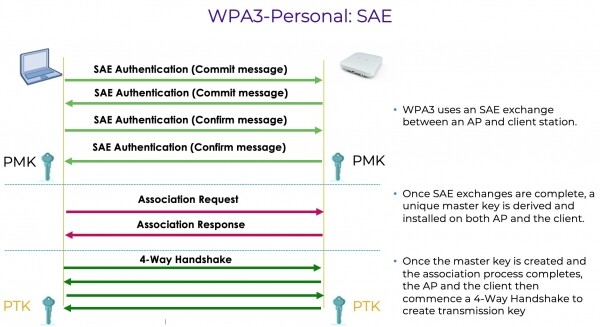
A more radical solution to the problems of WPA2-Personal is to transition to WPA3, whose main improvement is the use of SAE (Simultaneous Authentication of Equals) and static PSK. WPA3-Personal addresses the dictionary attack issue, but does not provide unique identification during authentication and consequently the ability to assign profiles (as a common static password is still used).
Additionally, it is important to consider that over 95% of existing clients currently do not support WPA3 and SAE, while WPA2 continues to function successfully on billions of already deployed devices.
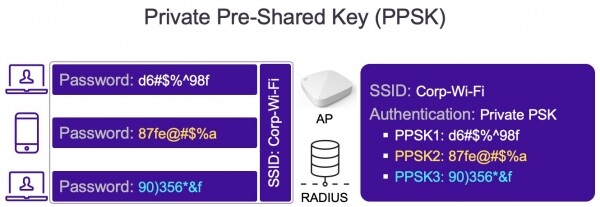
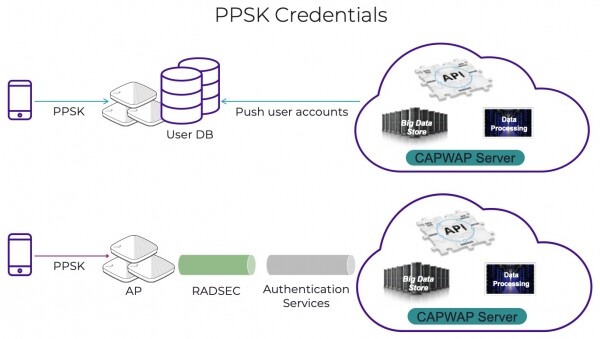
To address the existing or potentially possible issues described above, Extreme Networks has developed the Private Pre-Shared Key (PPSK) technology. PPSK is compatible with any Wi-Fi client that supports WPA2-PSK, and it provides a level of security comparable to that achieved with WPA2-Enterprise, without the need to build a 802.1X/EAP infrastructure. Private PSK is essentially WPA2-PSK, but each user (or group of users) can have their own dynamically generated password. Managing PPSK is no different from managing PSK, as the entire process is automated. The key database can be stored locally on access points or in the cloud.
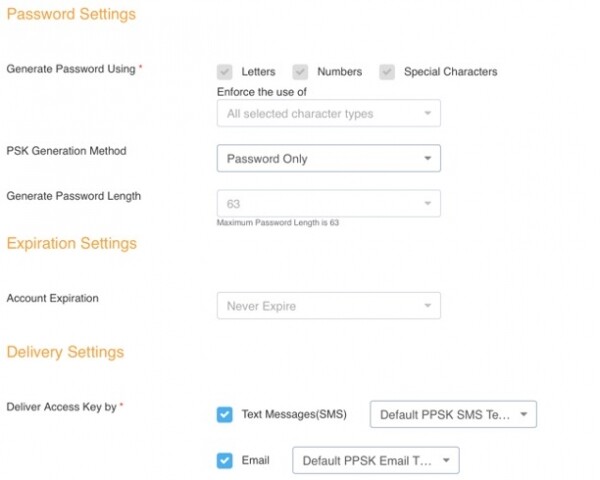
Passwords can be generated automatically, with the flexibility to set their length/resilience, duration, or expiration period, and the delivery method to the user (via email or SMS):
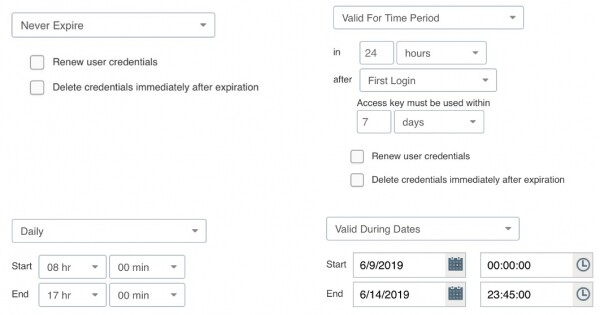
You can also configure the maximum number of clients that can connect using a single PPSK or even set up MAC binding for connecting devices. At the administrator's command, any key can be easily revoked, preventing network access without the need to reconfigure all other devices. If a client is connected at the time the key is revoked, the access point will automatically disconnect them from the network.
Key advantages of PPSK include:
- ease of use combined with a high level of security;
- dictionary attack resistance is handled with long and resilient passwords that ExtremeCloudIQ can automatically generate and distribute;
- the ability to assign different security profiles to various devices connected to a single SSID;
- ideal for secure guest access;
- excellent for secure access when devices do not support 802.1X/EAP (manual scanners or IoT/VoWiFi devices);
- successful use and refinement for over 10 years.
Any questions that arise or remain can always be directed to our office staff – .
Source: habr.com
